Uploaded October 2026 | Updated November 2026, 3 hours ago
Quantum computers do not need to be operational today for network operators to have a problem. Traffic with long-term value can be captured now, stored, and attacked later—a threat commonly known as Harvest Now, Decrypt Later.
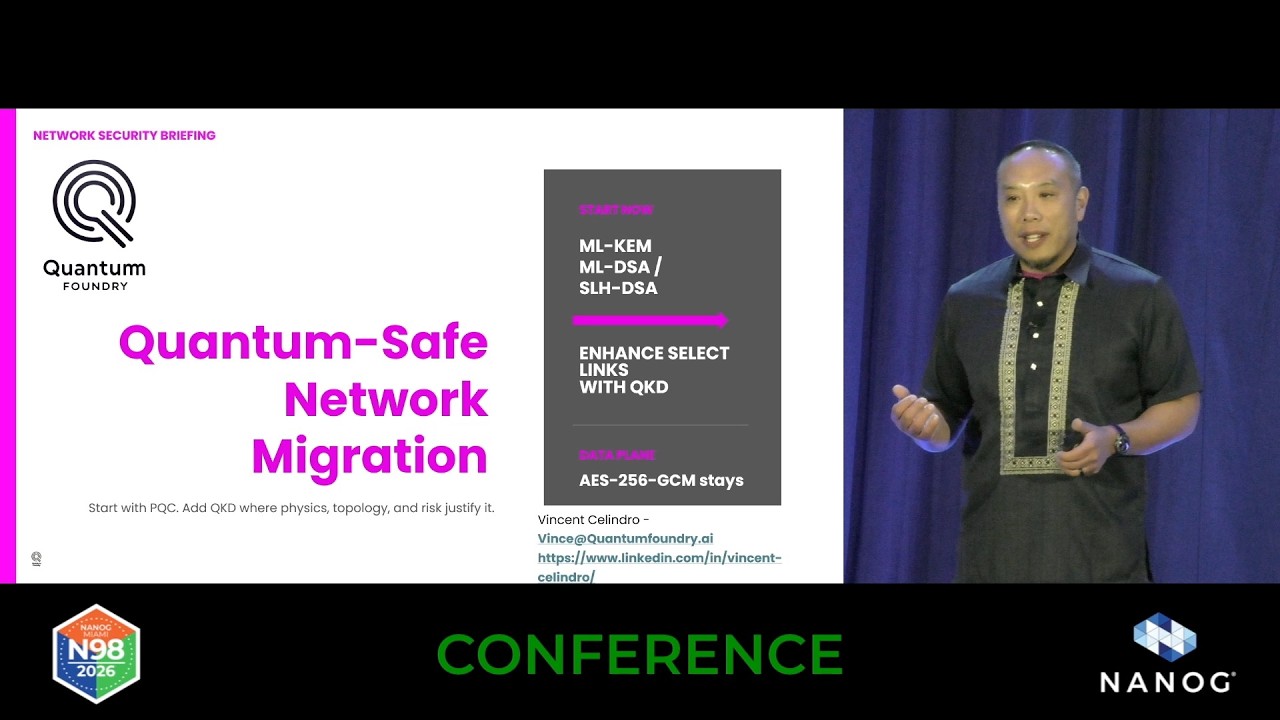
Becoming quantum-safe does not require replacing IPsec, AES, or existing networks; it means modernizing the vulnerable public-key functions used for authentication and key establishment. Starting with familiar IKEv1 and IKEv2 architecture, this operator-focused session explains how Shor’s and Grover’s algorithms affect RSA, ECDSA, DH, and ECDH while AES-256-GCM remains suitable for bulk encryption. We will compare classical and quantum-safe IPsec, introduce hybrid ECDH plus ML-KEM and NIST FIPS 203–205, and explain why PQC should be deployed broadly while QKD is applied selectively.
Attendees will leave with a practical migration roadmap: inventory cryptography, prioritize data by confidentiality lifetime, build crypto-agility into network designs, evaluate vendor interoperability, and begin testing quantum-resistant key establishment. Executive Order 14412 and current standards milestones will be placed in operational context.
No quantum-computing background is required, and this is not a vendor pitch. The goal is to make quantum-safe networking understandable and actionable for the engineers who will ultimately deploy and operate it.
Quantum computers do not need to be operational today for network operators to have a problem. Traffic with long-term value can be captured now, stored, and attacked later—a threat commonly known as Harvest Now, Decrypt Later.
Becoming quantum-safe does not require replacing IPsec, AES, or existing networks; it means modernizing the vulnerable public-key functions used for authentication and key establishment. Starting with familiar IKEv1 and IKEv2 architecture, this operator-focused session explains how Shor’s and Grover’s algorithms affect RSA, ECDSA, DH, and ECDH while AES-256-GCM remains suitable for bulk encryption. We will compare classical and quantum-safe IPsec, introduce hybrid ECDH plus ML-KEM and NIST FIPS 203–205, and explain why PQC should be deployed broadly while QKD is applied selectively.
Attendees will leave with a practical migration roadmap: inventory cryptography, prioritize data by confidentiality lifetime, build crypto-agility into network designs, evaluate vendor interoperability, and begin testing quantum-resistant key establishment. Executive Order 14412 and current standards milestones will be placed in operational context.
No quantum-computing background is required, and this is not a vendor pitch. The goal is to make quantum-safe networking understandable and actionable for the engineers who will ultimately deploy and operate it.