Uploaded November 2026 | Updated November 2026, 1 day ago
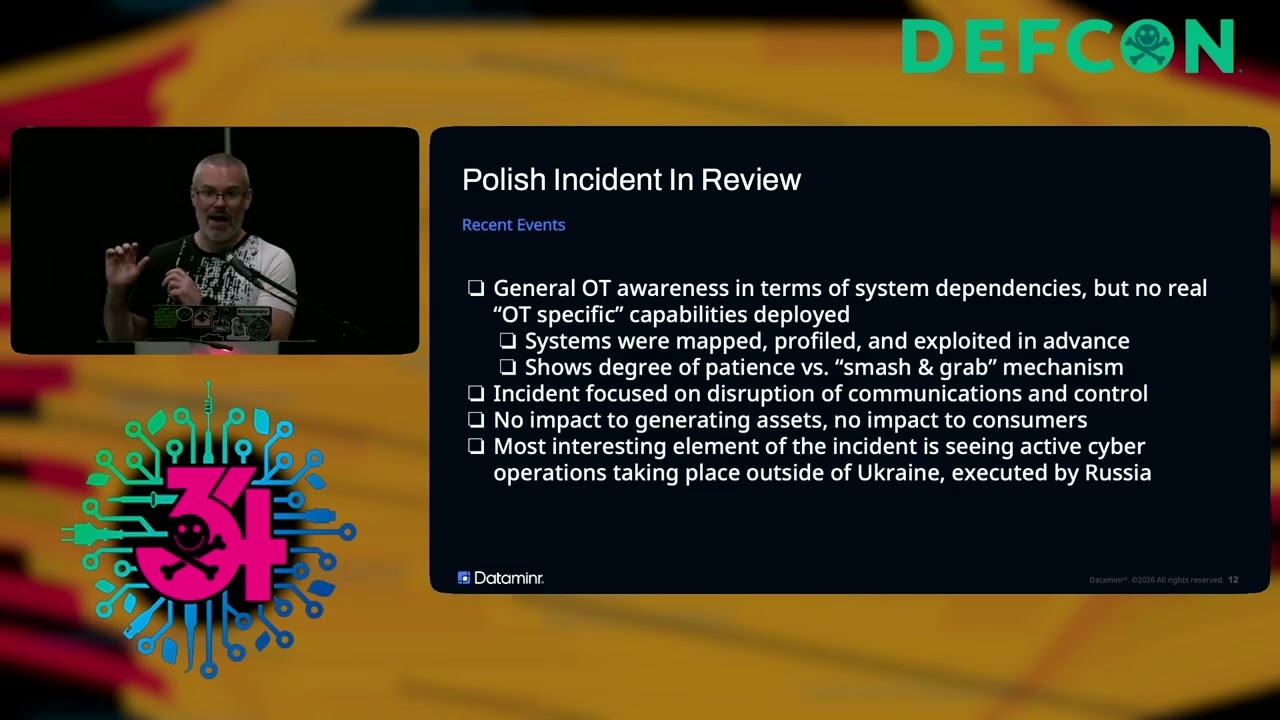
026 featured news of a new attempted, disruptive cyber attack against the electric sector. Instead of transmission or distribution in Ukraine, however, the event focused on generating assets in Poland. Irrespective of impact, the very fact such an action was attempted is concerning and newsworthy. However, the details of the event demonstrate the state of the "now" for electric sector events, in terms of their successes as well as failures.
In this discussion we will leverage all available public reporting to look at where the attackers innovated, borrowed from past events, and failed to learn from history in the December 2025 Polish event. From this discussion we will set the incident in context of both concurrent intrusions, such as Volt Typhoon activity, and historical incidents, linked to the Sandworm threat actor, to see just where adversaries are today with respect to tradecraft and sector knowledge.
From this exploration, attendees will emerge with a better understanding of what adversaries are "getting right" about such events, and where they still fall short. Furthermore, review of events will show the significance of physical safeguards and controls in ensuring continuous operations in the face of cyber effects, and how adversaries remain challenged to overcome such barriers.
026 featured news of a new attempted, disruptive cyber attack against the electric sector. Instead of transmission or distribution in Ukraine, however, the event focused on generating assets in Poland. Irrespective of impact, the very fact such an action was attempted is concerning and newsworthy. However, the details of the event demonstrate the state of the "now" for electric sector events, in terms of their successes as well as failures.
In this discussion we will leverage all available public reporting to look at where the attackers innovated, borrowed from past events, and failed to learn from history in the December 2025 Polish event. From this discussion we will set the incident in context of both concurrent intrusions, such as Volt Typhoon activity, and historical incidents, linked to the Sandworm threat actor, to see just where adversaries are today with respect to tradecraft and sector knowledge.
From this exploration, attendees will emerge with a better understanding of what adversaries are "getting right" about such events, and where they still fall short. Furthermore, review of events will show the significance of physical safeguards and controls in ensuring continuous operations in the face of cyber effects, and how adversaries remain challenged to overcome such barriers.