Uploaded November 2026 | Updated November 2026, 1 day ago
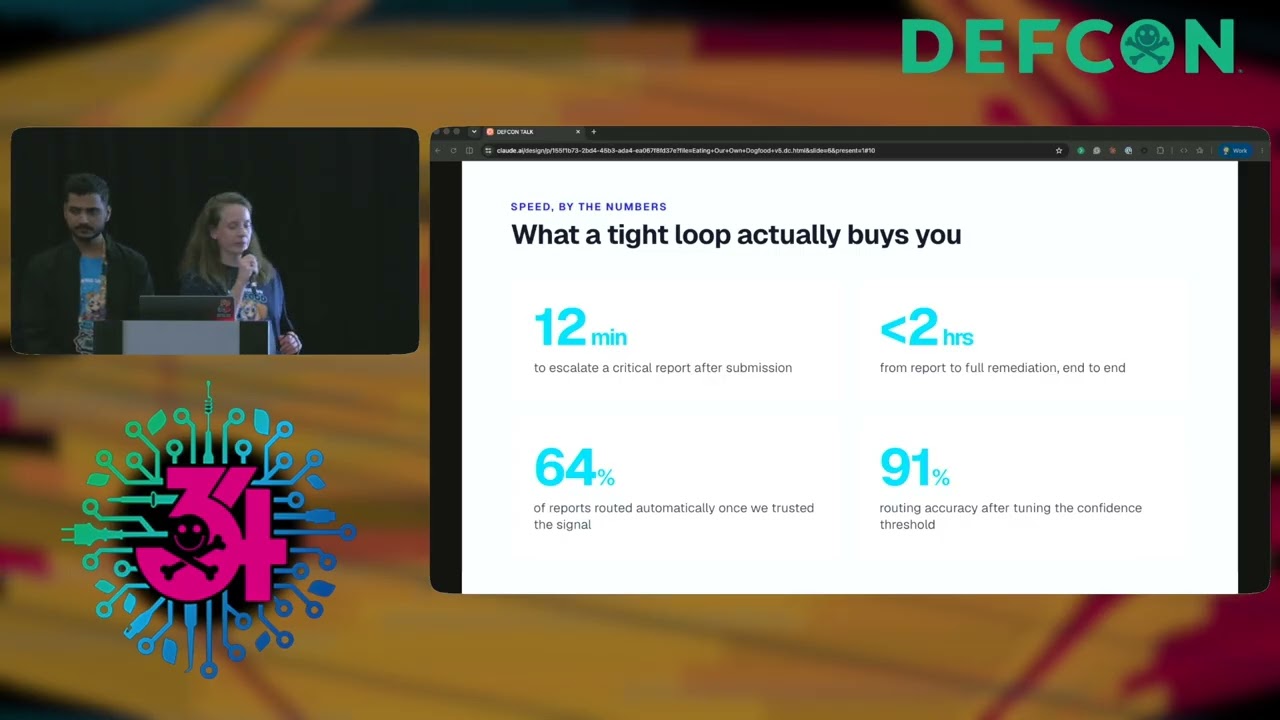
At HackerOne, the same community that submits vulnerability reports also tests the platform they use to report them. Every report becomes a live stress test of our product, workflows, assumptions, and newly shipped features. In this talk, a Senior Triage Lead and a Product Security Engineer share what we learned from running HackerOne’s own bug bounty program while shipping GraphQL features, AI-assisted tooling, disclosure workflows, and platform-scale infrastructure changes. Using three real disclosed reports, we walk through how seemingly small bugs escalated into platform-wide security lessons: 1. An Elasticsearch query parameter that enabled metadata enumeration through raw script execution. 2. A PDF export feature that unintentionally exposed internal triage activity. 3. An AI agent that exposed non-public report metadata because a researcher asked the right question. We will show how reports move from submission to validation, severity debates, engineering response, remediation, retesting, and disclosure. We will also discuss how we use our own program as a testing ground for AI-assisted triage, automated validation workflows, and disclosure policies before rolling changes out more broadly. This is not a “how to run a bug bounty program” talk. It is a behind-the-scenes look at what happens when hackers continuously attack the bug bounty platform itself and how that pressure forces rapid security evolution. Attendees will leave with practical lessons on: 1. building tighter triage-to-engineering feedback loops, 2. handling modern attack surfaces like GraphQL and AI agents, 3. scaling remediation without losing researcher trust, 4. and turning bug bounty programs into product improvement engines instead of passive inboxes. All case studies are based on disclosed HackerOne reports. No customer data was accessed or exposed.
At HackerOne, the same community that submits vulnerability reports also tests the platform they use to report them. Every report becomes a live stress test of our product, workflows, assumptions, and newly shipped features. In this talk, a Senior Triage Lead and a Product Security Engineer share what we learned from running HackerOne’s own bug bounty program while shipping GraphQL features, AI-assisted tooling, disclosure workflows, and platform-scale infrastructure changes. Using three real disclosed reports, we walk through how seemingly small bugs escalated into platform-wide security lessons: 1. An Elasticsearch query parameter that enabled metadata enumeration through raw script execution. 2. A PDF export feature that unintentionally exposed internal triage activity. 3. An AI agent that exposed non-public report metadata because a researcher asked the right question. We will show how reports move from submission to validation, severity debates, engineering response, remediation, retesting, and disclosure. We will also discuss how we use our own program as a testing ground for AI-assisted triage, automated validation workflows, and disclosure policies before rolling changes out more broadly. This is not a “how to run a bug bounty program” talk. It is a behind-the-scenes look at what happens when hackers continuously attack the bug bounty platform itself and how that pressure forces rapid security evolution. Attendees will leave with practical lessons on: 1. building tighter triage-to-engineering feedback loops, 2. handling modern attack surfaces like GraphQL and AI agents, 3. scaling remediation without losing researcher trust, 4. and turning bug bounty programs into product improvement engines instead of passive inboxes. All case studies are based on disclosed HackerOne reports. No customer data was accessed or exposed.