Uploaded May 2026 | Updated September 2026, 2 weeks ago
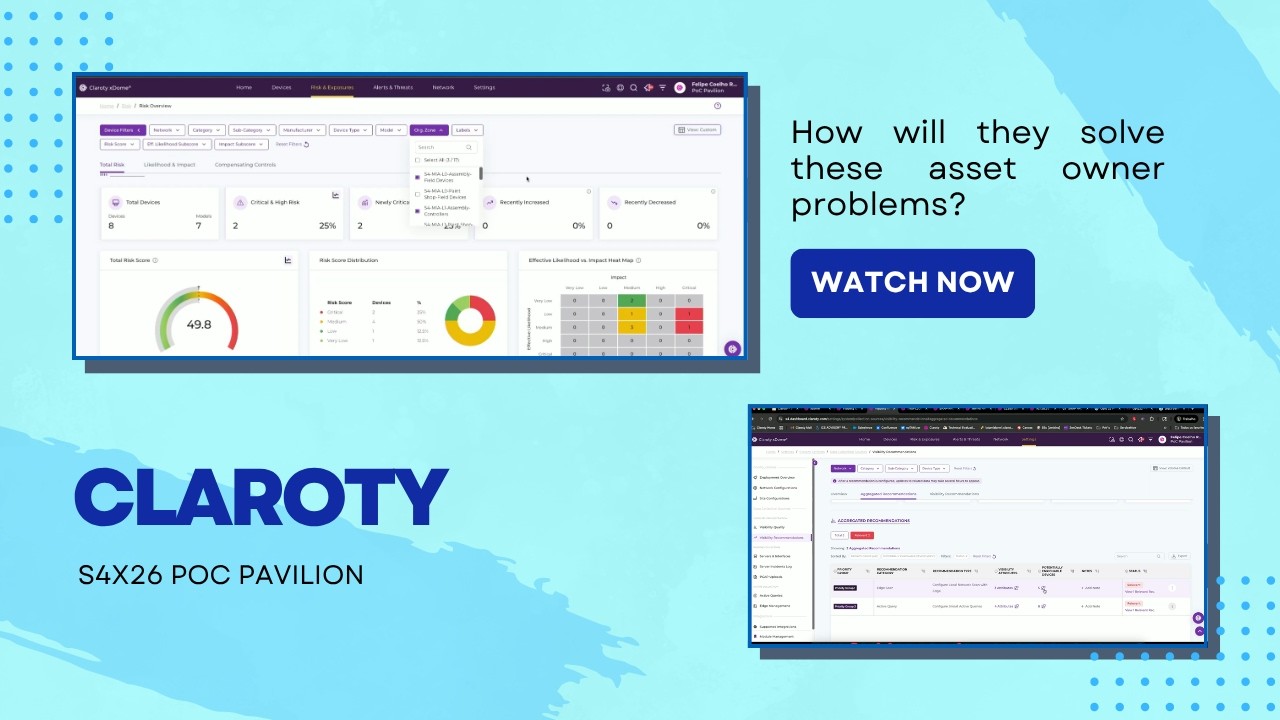
Problem: How do we know what cyber assets are in our OT environment, the vulnerabilities in these cyber assets, and which actions will most effectively reduce related risk?
Success Criteria:
Objective 1: Provide a detailed asset inventory that can support the engineering team’s understanding of what assets are on their network, and demonstrate that the approach we take can be scaled across their entire estate to optimize insight while minimizing time to roll out and cost to implement, as measure by:
● Visibility Quality greater than 85% Excellent Visibility for the OT assets in scope (defined below)
● Demonstrate that the time to accomplish this is minimized using the approach we are taking across the customer’s estate
● Demonstrate that the cost required to accomplish this is minimal in terms of footprint using the approach we are taking
Objective 2: Demonstrate that the solution can accurately identify vulnerabilities and exposures (non source code risk factors) comprehensively and accurately, the risk implications to operations, and the prioritized actions to mitigate the risk, as measured by:
● Correctly identifying 85% of the KEVs and easily exploitable exposures on the assets deployed in the environment
● Specific actions that can be taken on a prioritized basis, including patches and/or compensating controls that can be used to mitigate the risk.
Subscribe to Dale’s ICS Security: Friday News & Notes email here:
friday.dale-peterson.com/signup
Check out S4x27. Feb 8 - 11 in Tampa:
[https://s4xevents.com](https://s4xevents.com/)
Problem: How do we know what cyber assets are in our OT environment, the vulnerabilities in these cyber assets, and which actions will most effectively reduce related risk?
Success Criteria:
Objective 1: Provide a detailed asset inventory that can support the engineering team’s understanding of what assets are on their network, and demonstrate that the approach we take can be scaled across their entire estate to optimize insight while minimizing time to roll out and cost to implement, as measure by:
● Visibility Quality greater than 85% Excellent Visibility for the OT assets in scope (defined below)
● Demonstrate that the time to accomplish this is minimized using the approach we are taking across the customer’s estate
● Demonstrate that the cost required to accomplish this is minimal in terms of footprint using the approach we are taking
Objective 2: Demonstrate that the solution can accurately identify vulnerabilities and exposures (non source code risk factors) comprehensively and accurately, the risk implications to operations, and the prioritized actions to mitigate the risk, as measured by:
● Correctly identifying 85% of the KEVs and easily exploitable exposures on the assets deployed in the environment
● Specific actions that can be taken on a prioritized basis, including patches and/or compensating controls that can be used to mitigate the risk.
Subscribe to Dale’s ICS Security: Friday News & Notes email here:
friday.dale-peterson.com/signup
Check out S4x27. Feb 8 - 11 in Tampa:
[https://s4xevents.com](https://s4xevents.com/)


