Uploaded March 2026 | Updated November 2026, 1 day ago
Check out KnocKnoc here: https://ul.live/knocknoc_yt
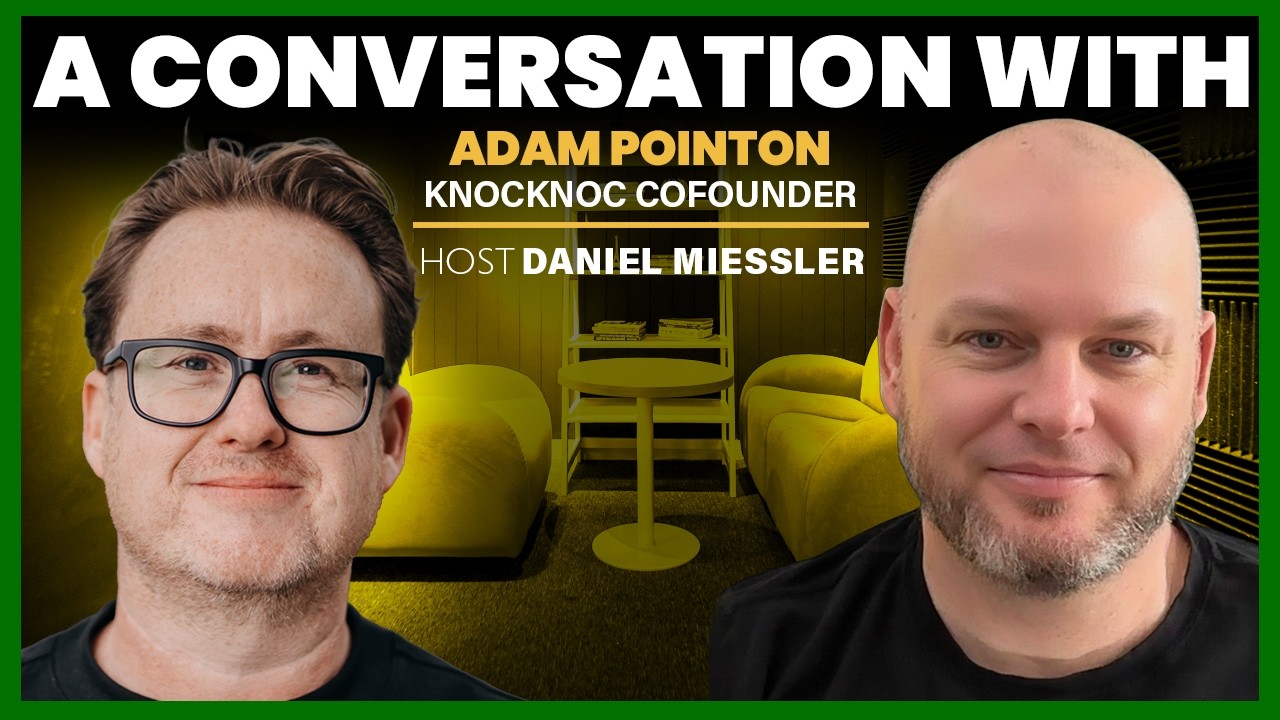
In this episode of Unsupervised Learning, I sit down with Adam to discuss KnocKnoc, a platform created to solve just-in-time network access and drastically reduce attack surfaces. Join us as we explore how hiding services behind pre-authentication modernizes default-deny security policies and keeps your infrastructure completely invisible to attackers until trust is proven.
What we talk about:
The Evolution of Port Knocking:
How Knock-Knock was born out of traditional port knocking and evolved to completely hide network services, eliminating pre-authentication attack surfaces.
Security vs. Obscurity:
A deep dive into the "security through obscurity" debate and how hiding the mechanism while requiring a specific "key" drastically increases the cost, effort, and time required for attackers to map a network.
Real-World Infrastructure Shielding:
Practical use cases for the platform, from protecting frequently targeted services like Citrix from zero-day exploits to completely cloaking cloud development and test environments from the public internet.
Self-Defending Endpoints at Scale:
Expanding just-in-time access controls beyond edge firewalls directly to host machines, including Linux, Windows, and even legacy systems like HP-UX and Solaris SPARC.
The Future of Universal Policy:
How this foundational default-deny approach paves the way for universal security policies, translating human-readable business rules into strict access controls across all network levels and data layers.
Subscribe to the newsletter at:
danielmiessler.com/subscribe
Join the UL community at:
danielmiessler.com/upgrade
Follow on X:
https://x.com/danielmiessler
Follow on LinkedIn:
linkedin.com/in/danielmiessler
Check out KnocKnoc here: https://ul.live/knocknoc_yt
In this episode of Unsupervised Learning, I sit down with Adam to discuss KnocKnoc, a platform created to solve just-in-time network access and drastically reduce attack surfaces. Join us as we explore how hiding services behind pre-authentication modernizes default-deny security policies and keeps your infrastructure completely invisible to attackers until trust is proven.
What we talk about:
The Evolution of Port Knocking:
How Knock-Knock was born out of traditional port knocking and evolved to completely hide network services, eliminating pre-authentication attack surfaces.
Security vs. Obscurity:
A deep dive into the "security through obscurity" debate and how hiding the mechanism while requiring a specific "key" drastically increases the cost, effort, and time required for attackers to map a network.
Real-World Infrastructure Shielding:
Practical use cases for the platform, from protecting frequently targeted services like Citrix from zero-day exploits to completely cloaking cloud development and test environments from the public internet.
Self-Defending Endpoints at Scale:
Expanding just-in-time access controls beyond edge firewalls directly to host machines, including Linux, Windows, and even legacy systems like HP-UX and Solaris SPARC.
The Future of Universal Policy:
How this foundational default-deny approach paves the way for universal security policies, translating human-readable business rules into strict access controls across all network levels and data layers.
Subscribe to the newsletter at:
danielmiessler.com/subscribe
Join the UL community at:
danielmiessler.com/upgrade
Follow on X:
https://x.com/danielmiessler
Follow on LinkedIn:
linkedin.com/in/danielmiessler