Uploaded May 2026 | Updated September 2026, 1 week ago
Problem:
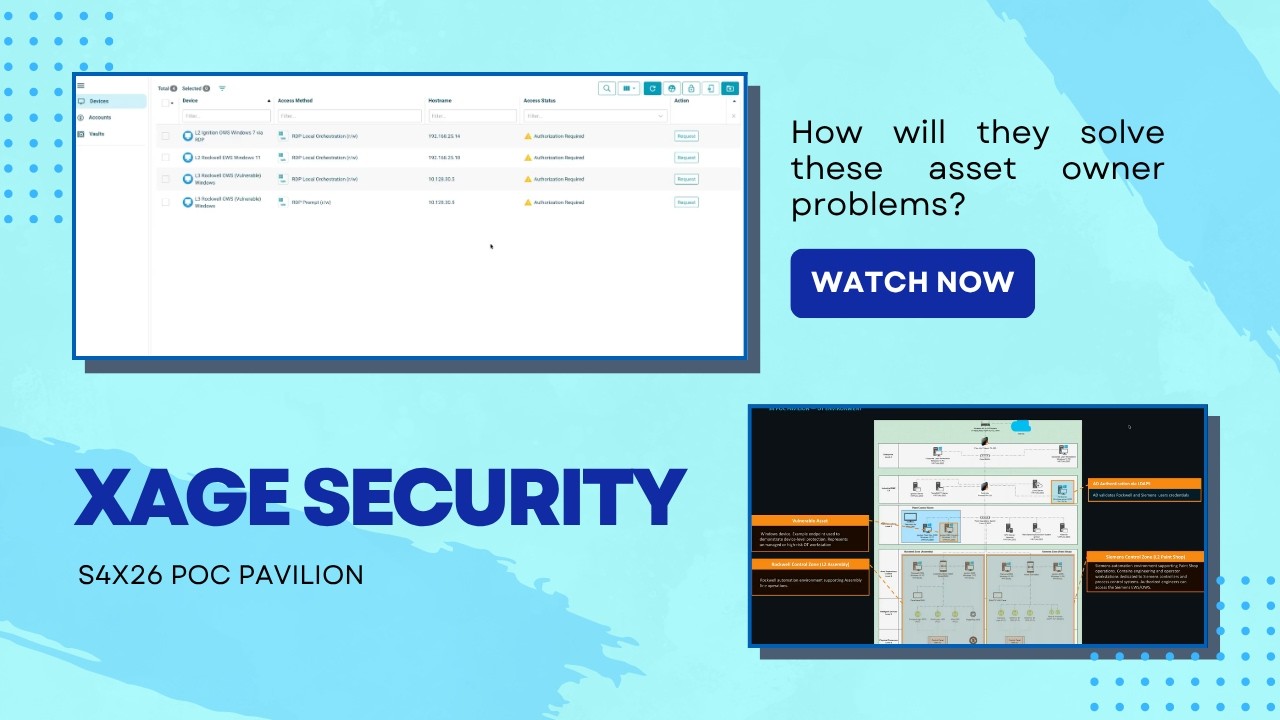
1) How can we allow access to our OT environment, but ensure that access is only granted to the right users, for the right assets, and only when they should have access—without impacting productivity?
2) If our vulnerable devices cannot be or are not patched, how can we ensure that they do not become threat vectors used in breach?
Success Criteria:
1. Users are granted just-in-time, task-specific access to defined OT assets; any access outside the approved asset scope or time window is automatically denied.
2. Authorized users can connect only to the systems explicitly required for their role or work order; all other OT and IT systems are inaccessible by default.
3. If vulnerable or legacy devices cannot be patched, access to those assets is enforced by XEP with default-deny and explicit, time-limited approval, reducing their risk as threat vectors.
4. Even where a proof-of-concept exploit would normally succeed, attacks are blocked.
Problem:
1) How can we allow access to our OT environment, but ensure that access is only granted to the right users, for the right assets, and only when they should have access—without impacting productivity?
2) If our vulnerable devices cannot be or are not patched, how can we ensure that they do not become threat vectors used in breach?
Success Criteria:
1. Users are granted just-in-time, task-specific access to defined OT assets; any access outside the approved asset scope or time window is automatically denied.
2. Authorized users can connect only to the systems explicitly required for their role or work order; all other OT and IT systems are inaccessible by default.
3. If vulnerable or legacy devices cannot be patched, access to those assets is enforced by XEP with default-deny and explicit, time-limited approval, reducing their risk as threat vectors.
4. Even where a proof-of-concept exploit would normally succeed, attacks are blocked.