Uploaded October 2024 | Updated September 2026, 2 hours ago
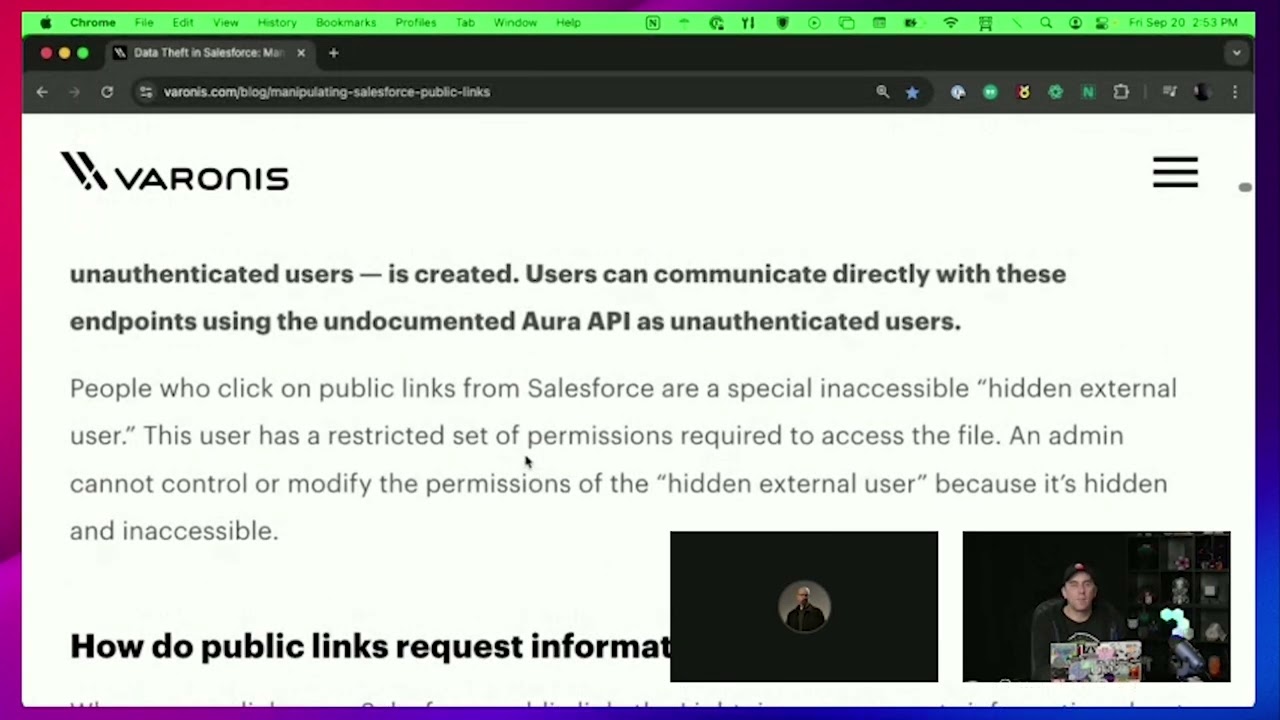
The Varonis Threat Labs team identified a vulnerability in Salesforce's public link feature, allowing hackers to access sensitive data character-by-character via a clever attack.
This attack is a real-world application of the tools we covered last week. Using Burpsuite, researchers were able to reverse engineer and exploit vulnerable behavior.
While the vulnerability is now patched, attackers could have manipulate API calls to an undocumented Salesforce Aura API combined with SOQL subqueries to perform a blind SOQL injection, retrieving PII and customer information.
Read more here:
varonis.com/blog/manipulating-salesforce-public-links
Follow me:
Mastodon: https://infosec.exchange/@skickar
Thanks to our sponsor Varonis ⬇️
LinkedIn: / varonis
Visit our website: varonis.com
The Varonis Threat Labs team identified a vulnerability in Salesforce's public link feature, allowing hackers to access sensitive data character-by-character via a clever attack.
This attack is a real-world application of the tools we covered last week. Using Burpsuite, researchers were able to reverse engineer and exploit vulnerable behavior.
While the vulnerability is now patched, attackers could have manipulate API calls to an undocumented Salesforce Aura API combined with SOQL subqueries to perform a blind SOQL injection, retrieving PII and customer information.
Read more here:
varonis.com/blog/manipulating-salesforce-public-links
Follow me:
Mastodon: https://infosec.exchange/@skickar
Thanks to our sponsor Varonis ⬇️
LinkedIn: / varonis
Visit our website: varonis.com