Uploaded September 2024 | Updated September 2026, 2 hours ago
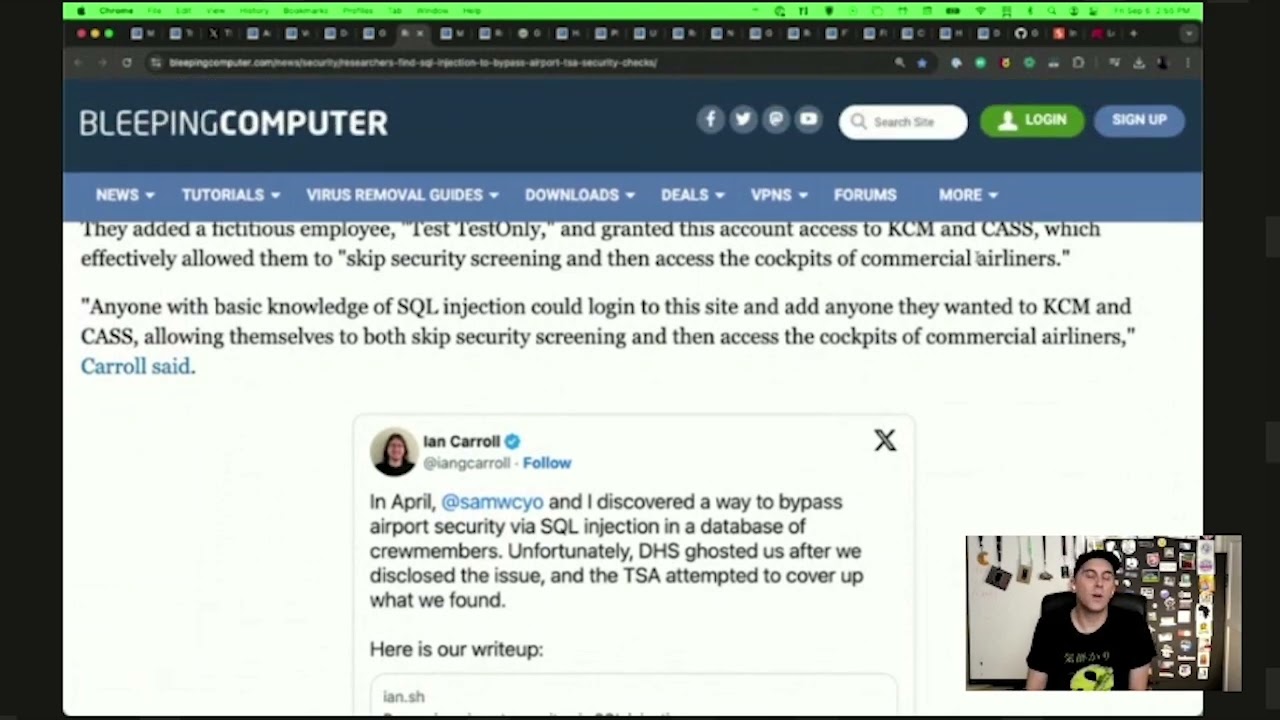
An online portal responsible for granting access to aircraft cockpits and more was vulnerable to a simple SQL injection attack.
This vulnerability means hackers could have logged in as an administrator, created accounts for themselves, and granted themselves permission to opt-out of security screenings for cockpit access.
An online portal responsible for granting access to aircraft cockpits and more was vulnerable to a simple SQL injection attack.
This vulnerability means hackers could have logged in as an administrator, created accounts for themselves, and granted themselves permission to opt-out of security screenings for cockpit access.