Uploaded October 2016 | Updated September 2026, 2 hours ago
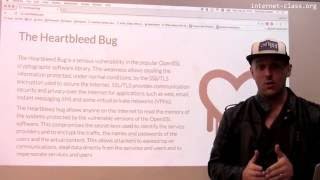
A great example of a software flaw in a deployed cryptosystem is the Heartbleed vulnerability identified in 2014: also known as CVE-2014-0160. Heartbleed was an extremely serious problem. It exploited a bug in the widespread and popular OpenSSL cryptographic software library. Attackers could read arbitrary memory contents from the machine that they were attacking, allowing them to steal keys, passwords, server content, and anything else that might be stored in the server’s memory. Even today we are not yet sure of the amount of information that it exposed.
Credits: Talking: Geoffrey Challen (Assistant Professor, Computer Science and Engineering, University at Buffalo). Producing: Greg Bunyea (Undergraduate, Computer Science and Engineering, University at Buffalo).
Part of the internet-class.org online internet course. A blue Systems Research Group (https://blue.cse.buffalo.edu) production.
A great example of a software flaw in a deployed cryptosystem is the Heartbleed vulnerability identified in 2014: also known as CVE-2014-0160. Heartbleed was an extremely serious problem. It exploited a bug in the widespread and popular OpenSSL cryptographic software library. Attackers could read arbitrary memory contents from the machine that they were attacking, allowing them to steal keys, passwords, server content, and anything else that might be stored in the server’s memory. Even today we are not yet sure of the amount of information that it exposed.
Credits: Talking: Geoffrey Challen (Assistant Professor, Computer Science and Engineering, University at Buffalo). Producing: Greg Bunyea (Undergraduate, Computer Science and Engineering, University at Buffalo).
Part of the internet-class.org online internet course. A blue Systems Research Group (https://blue.cse.buffalo.edu) production.