Uploaded October 2026 | Updated November 2026, 3 days ago
USENIX Security '26 - Efficient Threshold ML-DSA
Sofía Celi, Brave Research and University of Bristol; Rafael del Pino and Thomas Espitau, PQShield; Guilhem Niot, PQShield and Univ Rennes, CNRS, IRISA; Thomas Prest, PQShield
Threshold signature schemes allow a group of users to jointly generate a digital signature, providing resilience against faults and enhancing decentralization. With the advent of post-quantum cryptography, lattice-based threshold signatures have gained attention as viable alternatives. Nevertheless, existing constructions frequently encounter challenges related to scalability, robustness, or compatibility with standardized schemes, particularly with the NIST-selected and standardised Module-Lattice-based Digital Signature Algorithm (ML-DSA) algorithm.
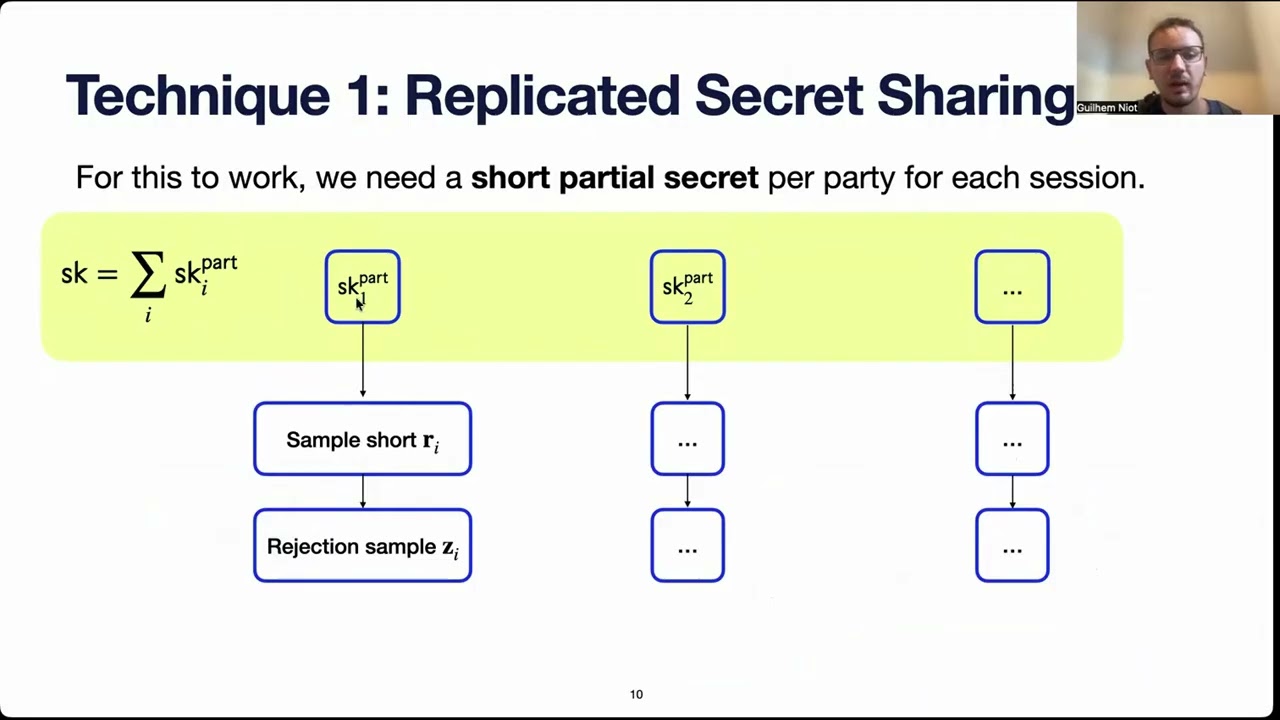
In this work, we present the first threshold signature scheme that is fully compatible with ML-DSA, supporting secure and efficient signing among up to six parties. Our construction leverages advanced short secret sharing techniques and integrates optimized rejection sampling to achieve a favourable balance between communication efficiency and correctness in distributed environments. We implement our construction in Go and evaluate its performance across local, LAN, and WAN network settings. Our benchmarks demonstrate that our threshold ML-DSA scheme is not only practically deployable but also well-suited for real-world applications, including multi-device cryptocurrency wallets, threshold-based TLS authentication, and for Tor's directory authorities.
View the full USENIX Security '26 program at usenix.org/conference/usenixsecurity26/technical-sessions
USENIX Security '26 - Efficient Threshold ML-DSA
Sofía Celi, Brave Research and University of Bristol; Rafael del Pino and Thomas Espitau, PQShield; Guilhem Niot, PQShield and Univ Rennes, CNRS, IRISA; Thomas Prest, PQShield
Threshold signature schemes allow a group of users to jointly generate a digital signature, providing resilience against faults and enhancing decentralization. With the advent of post-quantum cryptography, lattice-based threshold signatures have gained attention as viable alternatives. Nevertheless, existing constructions frequently encounter challenges related to scalability, robustness, or compatibility with standardized schemes, particularly with the NIST-selected and standardised Module-Lattice-based Digital Signature Algorithm (ML-DSA) algorithm.
In this work, we present the first threshold signature scheme that is fully compatible with ML-DSA, supporting secure and efficient signing among up to six parties. Our construction leverages advanced short secret sharing techniques and integrates optimized rejection sampling to achieve a favourable balance between communication efficiency and correctness in distributed environments. We implement our construction in Go and evaluate its performance across local, LAN, and WAN network settings. Our benchmarks demonstrate that our threshold ML-DSA scheme is not only practically deployable but also well-suited for real-world applications, including multi-device cryptocurrency wallets, threshold-based TLS authentication, and for Tor's directory authorities.
View the full USENIX Security '26 program at usenix.org/conference/usenixsecurity26/technical-sessions