Uploaded August 2011 | Updated September 2026, 6 hours ago
A special thanks to LXShadow, who worked very hard to hack level editor's code in the game. Also, another special thanks to him for the editor guide (explanations you see at the beginning of each tutorial videos about the editor). It helped me a lot to understand how the editor works.
Français:
-Contenu de la vidéo en Anglais seulement-
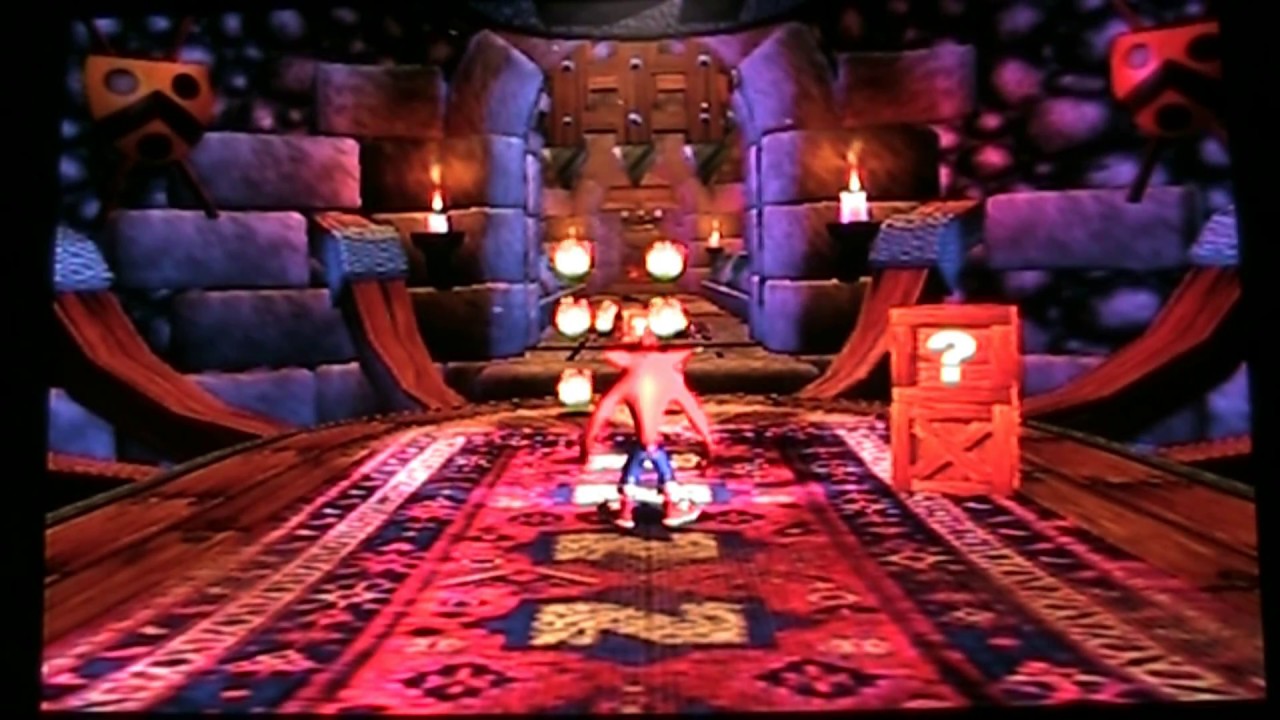
La deuxième partie du guide de l'éditeur de niveau caché du jeu Crash Bandicoot 4: The Warth Of Cortex (Ps2). Cette partie présente l'éditeur d'animations (Anim Editor) qui demande un certain niveau de programmation en matière de jeux vidéo. Cette vidéo va vous montrer à quoi cet éditeur ressemble, mais vous ne verrez pas d'animations complètes puisqu'il est très difficile à utiliser. je vais quand même vous présenter beaucoup de ses fonctions. Une de ses fonctionnalités que je préfères est le Memory Card Test Bed. Il permet de faire toutes sortes de tests avec la carte mémoire de la Ps2. AVERTISSEMENT: CETTE FONCTION PEUT EFFACER DÉFINITIVEMENT ET IMPRÉVISIBLEMENT TOUTES CARTES MÉMOIRES ENTRÉS DANS N'IMPORTE QUEL SLOT DE LA PS2. Utilisez-là à vos propres risques... Alors, pour les programmeurs, voici une autre façon de redonner à notre bon vieux jeu de Crash une nouvelle vie!
English:
Part 2 of the guide for the hidden level editor found in Crash Bandicoot 4: The Wrath Of Cortex (Ps2). This part presents the Animation Editor (Anim Editor). For use it, you need to know a little bit of game programmation because this Anim Editor is really hard to understand and use. So, you will not see in this video a big animation because I dont know really how this editor works:S I will show even a lot of his features! My favourite one is the Memory Card Test Bed. it allow you to do some evil things with you Ps2 Memory Card. WARNING: VISIT THIS MENU WITH NO MEMORY CARDS PLUGGED IN YOUR PS2, BECAUSE THIS FEATURE CAN CRASH DEFINITIVELY AND UNPREDICTABLY YOUR MEMORY CARD. Use it at your own risks, a format could be required to use it again... So, for programmers, this Anim Editor is a good way to give a second life to our old Crash game!
A special thanks to LXShadow, who worked very hard to hack level editor's code in the game. Also, another special thanks to him for the editor guide (explanations you see at the beginning of each tutorial videos about the editor). It helped me a lot to understand how the editor works.
Français:
-Contenu de la vidéo en Anglais seulement-
La deuxième partie du guide de l'éditeur de niveau caché du jeu Crash Bandicoot 4: The Warth Of Cortex (Ps2). Cette partie présente l'éditeur d'animations (Anim Editor) qui demande un certain niveau de programmation en matière de jeux vidéo. Cette vidéo va vous montrer à quoi cet éditeur ressemble, mais vous ne verrez pas d'animations complètes puisqu'il est très difficile à utiliser. je vais quand même vous présenter beaucoup de ses fonctions. Une de ses fonctionnalités que je préfères est le Memory Card Test Bed. Il permet de faire toutes sortes de tests avec la carte mémoire de la Ps2. AVERTISSEMENT: CETTE FONCTION PEUT EFFACER DÉFINITIVEMENT ET IMPRÉVISIBLEMENT TOUTES CARTES MÉMOIRES ENTRÉS DANS N'IMPORTE QUEL SLOT DE LA PS2. Utilisez-là à vos propres risques... Alors, pour les programmeurs, voici une autre façon de redonner à notre bon vieux jeu de Crash une nouvelle vie!
English:
Part 2 of the guide for the hidden level editor found in Crash Bandicoot 4: The Wrath Of Cortex (Ps2). This part presents the Animation Editor (Anim Editor). For use it, you need to know a little bit of game programmation because this Anim Editor is really hard to understand and use. So, you will not see in this video a big animation because I dont know really how this editor works:S I will show even a lot of his features! My favourite one is the Memory Card Test Bed. it allow you to do some evil things with you Ps2 Memory Card. WARNING: VISIT THIS MENU WITH NO MEMORY CARDS PLUGGED IN YOUR PS2, BECAUSE THIS FEATURE CAN CRASH DEFINITIVELY AND UNPREDICTABLY YOUR MEMORY CARD. Use it at your own risks, a format could be required to use it again... So, for programmers, this Anim Editor is a good way to give a second life to our old Crash game!


![iMultiBoot v0.6a (0F0817a) - Preview
This video is a preview of iMultiBoot, a software to install and manage multiple operating systems on 32-bit iOS devices. An alpha version is planned to be publicly released soon. Since its an alpha build, it will have many bugs pretty much everywhere. Some features are interactive partition management and custom boot images for additional operating systems. In order to boot additional operating systems, iMultiBoot uses kloader by @winocm (improved by @xerub). Actually, iMultiBoot only supports the iOS 6.1.6 (latest) with 5.1 (9B176) dual-boot combination on iPod Touch 4 (N81AP). However, some other combinations might work if proper decryption keys and patches are provided. Data-Protection hacks are not implemented yet, iOS 7.x and newer as main with iOS 6.x and lower combination will wont work. Reverse combination, iOS 6.x and older as main with 7.x might be possible since system bag is properly updated when secondary iOS boot for the first time.
Do not try iMultiBoot on A6 devices (iPhone 5 and iPad 4th) because it needs to restore your device in order to flash additional boot images in the firmware. Actually, the latest signed iOS version for A6 devices cant be jailbroken. So, iMultiBoot wont be able to continue the setup once the restore process is finished because it requires jailbreak to complete it. Jailbreak must also have tfp0 enabled to properly execute kloader.
The soundtrack of this video is a mix made by me with the following tracks :
A) DJ ASSASS1N - Frag Out [NCS Release],
https://www.youtube.com/watch?v=gWapX12pHPQ
B) DEAF KEV - Invincible [NCS Release],
https://www.youtube.com/watch?v=J2X5mJ3HDYE
C) Syn Cole - Feel Good [NCS Release],
https://www.youtube.com/watch?v=q1ULJ92aldE
D) Tobu & Itro - Sunburst [NCS Release],
https://www.youtube.com/watch?v=4lXBHD5C8do
E) Spektrem - Shine (Gabriel Drew & Bloom Remix) [NCS Release],
https://www.youtube.com/watch?v=rWVjht-MIto
F) Waysons - Daydream [NCS Release],
https://www.youtube.com/watch?v=ZynbJWCjJxg
G) Lensko - Cetus [NCS Release],
https://www.youtube.com/watch?v=i3vrV-WNmsc
H) Tobu - Candyland [NCS Release],
https://www.youtube.com/watch?v=IIrCDAV3EgI
I) Jim Yosef - Eclipse [NCS Release],
https://www.youtube.com/watch?v=1WP_YLn1D1c iMultiBoot v0.6a (0F0817a) - Preview](https://i.ytimg.com/vi/cY6wMoFmdQA/mqdefault.jpg)
![De Rebus Antiquis - iPad 4 (P102AP) iOS 7.x iBoot Exploit [Demo]
This is a demo of a complete De Rebus Antiquis iBoot exploit setup running on iPad 4 (P102AP). Once iBoot re-runs after the exploitation, it mounts a secondary HFS+ volume that contains a new bootloader image and executes it. In this demo, I simply used the same iBoot as the signed one, except running unsigned with custom patches and verbose boot enabled.
Im currently working on a complete write-up about De Rebus Antiquis iBoot exploit. Once it will be released, you should get most of the necessary knowledge to implement what you see in this video. See my personal blog here, https://www.pmbonneau.com/ for more details.
Many thanks to @dora2ios (Twitter) for help with some issues I had while debugging. De Rebus Antiquis - iPad 4 (P102AP) iOS 7.x iBoot Exploit [Demo]](https://i.ytimg.com/vi/d6b_G1gxu-Q/mqdefault.jpg)
![HFS+ Heap Buffer Overflow - iPad 2 (K94AP) iOS 5.x iBoot Exploit [Demo]
This is a post-exploitation demo of an HFS+ heap buffer overflow in iOS 5.x iBoot, running on iPad 2nd (K94AP). One particular use case of an iBoot exploit such as this one is the ability to downgrade or upgrade the device to any iOS version as long as it can run on it. This iPad 2nd is downgraded to iOS 5.x using previously saved SHSH blobs, so when powered-on, the signed iOS 5.x iBoot is executed. An HFS+ volume is specifically crafted to trigger an heap buffer overflow when iBoot attempts to mount it. Then, we get control over the PC register and eventually execute a custom payload which jumps to a completely new patched iBoot image. From there, additional unsigned bootchain images are executed and so, to fully boot iOS. In this video, iPad start up with the iOS 5.0.1 signed bootchain, exploit is triggered, then jumps to an iOS 7.1.2 bootchain.
See the complete write-up I did about this iBoot exploit on my personal blog here, https://www.pmbonneau.com/ios5-iboot-hfs-hbo/
This video was originally posted on X (Twitter) here, https://x.com/ShadowLee19/status/1074533504610918400?s=20 HFS+ Heap Buffer Overflow - iPad 2 (K94AP) iOS 5.x iBoot Exploit [Demo]](https://i.ytimg.com/vi/dJbakxWSy18/mqdefault.jpg)