Uploaded July 2026 | Updated September 2026, 18 hours ago
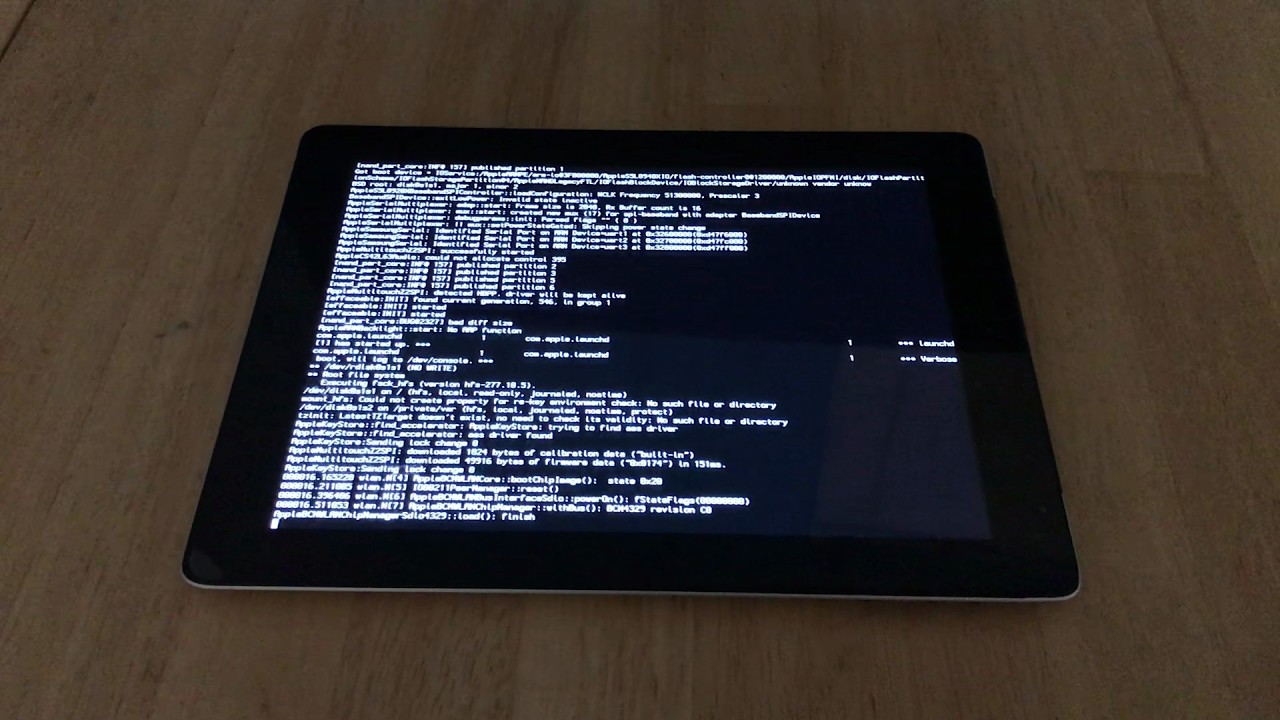
This is a post-exploitation demo of an HFS+ heap buffer overflow in iOS 5.x iBoot, running on iPad 2nd (K94AP). One particular use case of an iBoot exploit such as this one is the ability to downgrade or upgrade the device to any iOS version as long as it can run on it. This iPad 2nd is downgraded to iOS 5.x using previously saved SHSH blobs, so when powered-on, the signed iOS 5.x iBoot is executed. An HFS+ volume is specifically crafted to trigger an heap buffer overflow when iBoot attempts to mount it. Then, we get control over the PC register and eventually execute a custom payload which jumps to a completely new patched iBoot image. From there, additional unsigned bootchain images are executed and so, to fully boot iOS. In this video, iPad start up with the iOS 5.0.1 signed bootchain, exploit is triggered, then jumps to an iOS 7.1.2 bootchain.
See the complete write-up I did about this iBoot exploit on my personal blog here, pmbonneau.com/ios5-iboot-hfs-hbo
This video was originally posted on X (Twitter) here, https://x.com/ShadowLee19/status/1074533504610918400?s=20
This is a post-exploitation demo of an HFS+ heap buffer overflow in iOS 5.x iBoot, running on iPad 2nd (K94AP). One particular use case of an iBoot exploit such as this one is the ability to downgrade or upgrade the device to any iOS version as long as it can run on it. This iPad 2nd is downgraded to iOS 5.x using previously saved SHSH blobs, so when powered-on, the signed iOS 5.x iBoot is executed. An HFS+ volume is specifically crafted to trigger an heap buffer overflow when iBoot attempts to mount it. Then, we get control over the PC register and eventually execute a custom payload which jumps to a completely new patched iBoot image. From there, additional unsigned bootchain images are executed and so, to fully boot iOS. In this video, iPad start up with the iOS 5.0.1 signed bootchain, exploit is triggered, then jumps to an iOS 7.1.2 bootchain.
See the complete write-up I did about this iBoot exploit on my personal blog here, pmbonneau.com/ios5-iboot-hfs-hbo
This video was originally posted on X (Twitter) here, https://x.com/ShadowLee19/status/1074533504610918400?s=20



![iPhone 4 (N90AP) iOS 7.1.2 Pangu Jailbreak - Cydia Applications Stashing Fail
I was prepearing a video about how to jailbreak iOS 7.1.2 on iPhone 4 (N90AP) using Pangu 7, but it seems that Cydia had some problems during the application stashing process. This step is also known as Prepearing the FileSystem, after opening Cydia for the first time. When jailbreaking your iOS device, the most important thing to do before is to backup important data before doing the process. Using iTunes for backup usually do a good work.
In technical details, Application Stashing is the process where Cydia moves /Applications folder from the first partition (/dev/disk0s1s1) to /var/stash/[random string]/Applications, which is on the second partition (/dev/disk0s1s2). After moving applications, a Unix symlink refeering /Applications folder to /var/stash/[random string]/Applications is made to trick the iOS system. The goal of Application Stashing is to free up disk space on the system partition (/dev/disk0s1s1) for Cydia packages, some iOS system tweaking and so.
I now have to restore (again) that N90AP. iPhone 4 (N90AP) iOS 7.1.2 Pangu Jailbreak - Cydia Applications Stashing Fail](https://i.ytimg.com/vi/nhku20ETHCU/mqdefault.jpg)
![Futurama - Holophonor Sonnet for Leela [Piano]
Here is a piano arrangment of the holophonor song played by Fry for Leela in the Parasite Lost (S03E04) episode of Futurama.
There are five softwares used in the making of this arrangement.
1 - Nero Recode (probably, I dont remember exactly): To extract the audio from the original video. Then, I cut all the audio except the holophonor part and exported to WAV format using audacity.
2 - AnthemScore: To reverse the song. This software allows me to see a visual representation of the actual song and guess notes, plus it uses an IA to automatically do a part of this work. The final product is a sheet music in MusicXML file format.
3 - MuseScore: To re-encode the MusicXML output of AnthemScore to a more versatile MusicXML format. I dont know why, but using AnthemScores MusicXML output in Synthesia doesnt work well, the BPM isnt the right one. Converting the file with Musescore will produce a MusicXML file that will be better with Synthesia.
4 - Synthesia: To get this nice piano roll and also to practice the song on a real piano.
Album : N/A
Title : Holophonor Sonnet for Leela
Arrangment type : Reversed from soundtrack
Download sheet music from my blog here : https://www.pmbonneau.com/music/arrangements/ Futurama - Holophonor Sonnet for Leela [Piano]](https://i.ytimg.com/vi/nnynLpZVWno/mqdefault.jpg)

![iPhone 4 (N90AP) iOS Multi Boot - Kloader and Limera1n DFU Bootstrap
IMPORTANT!!! Please note that this video is for educational purpose only. By watching this video, you agree that Im not responsible of what might happen with the use of informations provided.
WARNING : This video involves hacking on Low-Level parts of iOS. Unlike userland, those parts contains lot of critical informations about the devices hardware, which could be corrupted and lead to a hard brick if something goes wrong by following instructions provided in this video.
From a jailbroken iOS 7.1.2 kernel on which TaskforPid() is patched, Winocms Kloader can be executed to bootstrap the beginning of another iOS bootchain instance (in this video, its an iOS 6.1.3 one). The ARM image usually used with kloader is iBSS, from the DFU Bootchain. Most Kloader bootstraps use DFU Bootchains images even if it is also possible to use Flashed Bootchain ones, which are usually more complete (like flashed iBoot can interact with File System, while iBEC cant). DFU one usually involve more loading in memory than Flashed Bootchain, which is more File System friendly. Once Kloader did its magic and loaded iBSS, we have to send to it iBEC ARM image, the second stage of the DFU Bootchain. The LCD screen of the iOS device light up when iBEC is launched. Now the most interesting part begins. We have to send to iBEC each boot components in a specific order. First, send and execute the DeviceTree. Second, send and load a Ramdisk (seems to make no sense because we want to boot the File System, but there is something tricky here). Third, send the iOS Kernel and launch it using bootx.
If you do those steps using original decrypted and patched files, without patching boot-args, this will load the restore Ramdisk. If you dont specify a Ramdisk in steps above, this will load the File System, but without taking in consideration boot-args (no verbose boot). If you open the decrypted iBEC file using a Hex editor, you will notice that boot-args are set like that : rd=md0 nand-enable-reformat=1 -progress. Those are boot-args used when booting a Ramdisk. If we change this boot-args string to : -v, iBEC will load the File System by default, because we removed rd=md0 which sets the RootDevice to MemoryDevice0, which is the Ramdisk. Its also possible to change the default root device by adding rd=[Root Device] in iBECs boot-args string.
Limera1n BootROM exploit is superior than Kloader. It acts directly from DFU mode, so an installed Operating System is not required. In the second part of this video, I simply use RedSn0w jailbreak utility to inject Limera1n over the DFU Mode. The root device is set to the iOS 5.1.1 filesystem in iBECs boot-args. Then, RedSn0w will automatically send and execute each bootloaders in their respective order. iPhone 4 (N90AP) iOS Multi Boot - Kloader and Limera1n DFU Bootstrap](https://i.ytimg.com/vi/oJbuS_qjrlI/mqdefault.jpg)