Uploaded October 2019 | Updated September 2026, 1 day ago
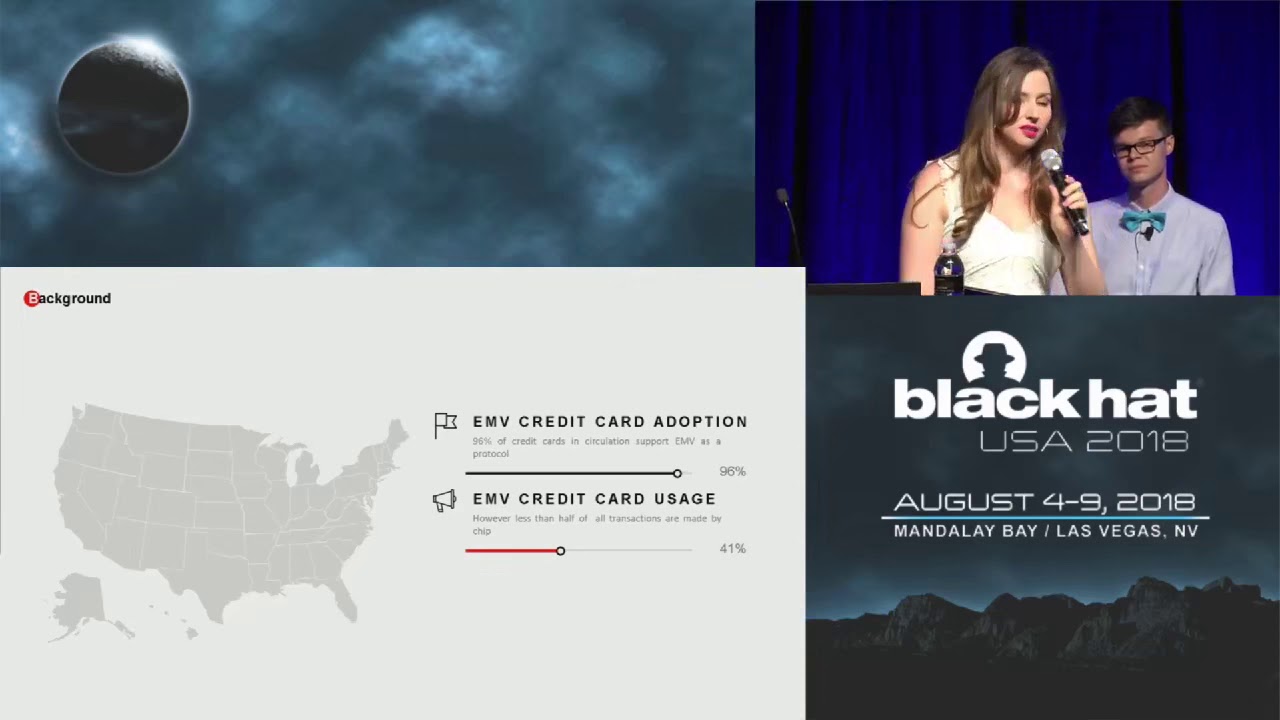
These days it's hard to find a business that doesn't accept faster payments. Mobile Point of Sales (mPOS) terminals have propelled this growth lowering the barriers for small and micro-sized businesses to accept non-cash payments. Older payment technologies like mag-stripe still account for the largest majority of all in-person transactions. This is complicated further by the introduction of new payment standards such as NFC. As with each new iteration in payment technology, inevitably weaknesses are introduced into this increasingly complex payment eco-system.
In this talk, we ask what are the security and fraud implications of removing the economic barriers to accepting card payments; and what are the risks associated with continued reliance on old card standards like mag-stripe? In the past, testing for payment attack vectors has been limited to the scope of individual projects and to those that have permanent access to POS and payment infrastructure. Not anymore!
In what we believe to be the most comprehensive research conducted in this area, we consider four of the major mPOS providers spread across the US and Europe; Square, SumUp, iZettle, and Paypal. We provide live demonstrations of new vulnerabilities that allow you to MitM transactions, send arbitrary code via Bluetooth and mobile application, modify payment values for mag-stripe transactions, and a vulnerability in firmware; DoS to RCE. Using this sampled geographic approach, we are able to show the current attack surface of mPOS and, to predict how this will evolve over the coming years.
For audience members that are interested in integrating testing practices into their organization or research practices, we will show you how to use mPOS to identify weaknesses in payment technologies, and how to remain undetected in spite of anti-fraud and security mechanisms.
Black Hat USA 2018
These days it's hard to find a business that doesn't accept faster payments. Mobile Point of Sales (mPOS) terminals have propelled this growth lowering the barriers for small and micro-sized businesses to accept non-cash payments. Older payment technologies like mag-stripe still account for the largest majority of all in-person transactions. This is complicated further by the introduction of new payment standards such as NFC. As with each new iteration in payment technology, inevitably weaknesses are introduced into this increasingly complex payment eco-system.
In this talk, we ask what are the security and fraud implications of removing the economic barriers to accepting card payments; and what are the risks associated with continued reliance on old card standards like mag-stripe? In the past, testing for payment attack vectors has been limited to the scope of individual projects and to those that have permanent access to POS and payment infrastructure. Not anymore!
In what we believe to be the most comprehensive research conducted in this area, we consider four of the major mPOS providers spread across the US and Europe; Square, SumUp, iZettle, and Paypal. We provide live demonstrations of new vulnerabilities that allow you to MitM transactions, send arbitrary code via Bluetooth and mobile application, modify payment values for mag-stripe transactions, and a vulnerability in firmware; DoS to RCE. Using this sampled geographic approach, we are able to show the current attack surface of mPOS and, to predict how this will evolve over the coming years.
For audience members that are interested in integrating testing practices into their organization or research practices, we will show you how to use mPOS to identify weaknesses in payment technologies, and how to remain undetected in spite of anti-fraud and security mechanisms.
Black Hat USA 2018