Uploaded October 2019 | Updated September 2026, 2 days ago
Credential compromise in the cloud is not a threat that one company faces, rather it is a widespread concern as more and more companies operate in the cloud. Credential compromise can lead to many different outcomes depending on the motive of the attacker who compromised the credentials. In some cases in the past, it has led to erroneous AWS service usage for bitcoin mining or other non-destructive yet costly abuse, and in others it has led to companies shutting down due to the loss of data and infrastructure.
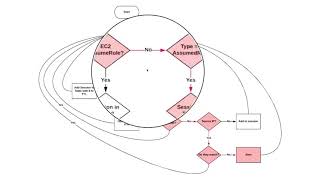
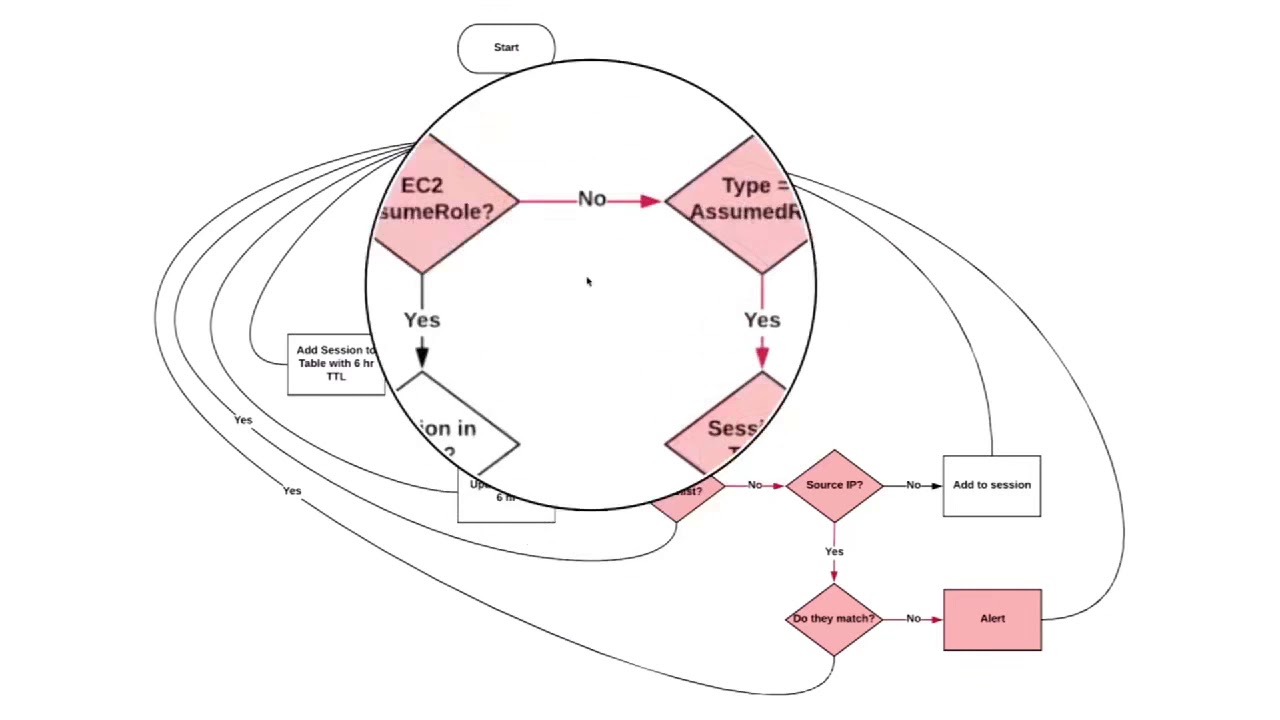
This paper describes an approach for detection of compromised credentials in AWS without needing to know all IPs in your infrastructure beforehand.
Credential compromise in the cloud is not a threat that one company faces, rather it is a widespread concern as more and more companies operate in the cloud. Credential compromise can lead to many different outcomes depending on the motive of the attacker who compromised the credentials. In some cases in the past, it has led to erroneous AWS service usage for bitcoin mining or other non-destructive yet costly abuse, and in others it has led to companies shutting down due to the loss of data and infrastructure.
This paper describes an approach for detection of compromised credentials in AWS without needing to know all IPs in your infrastructure beforehand.