Uploaded October 2019 | Updated September 2026, 15 minutes ago
Black Hat USA 2018
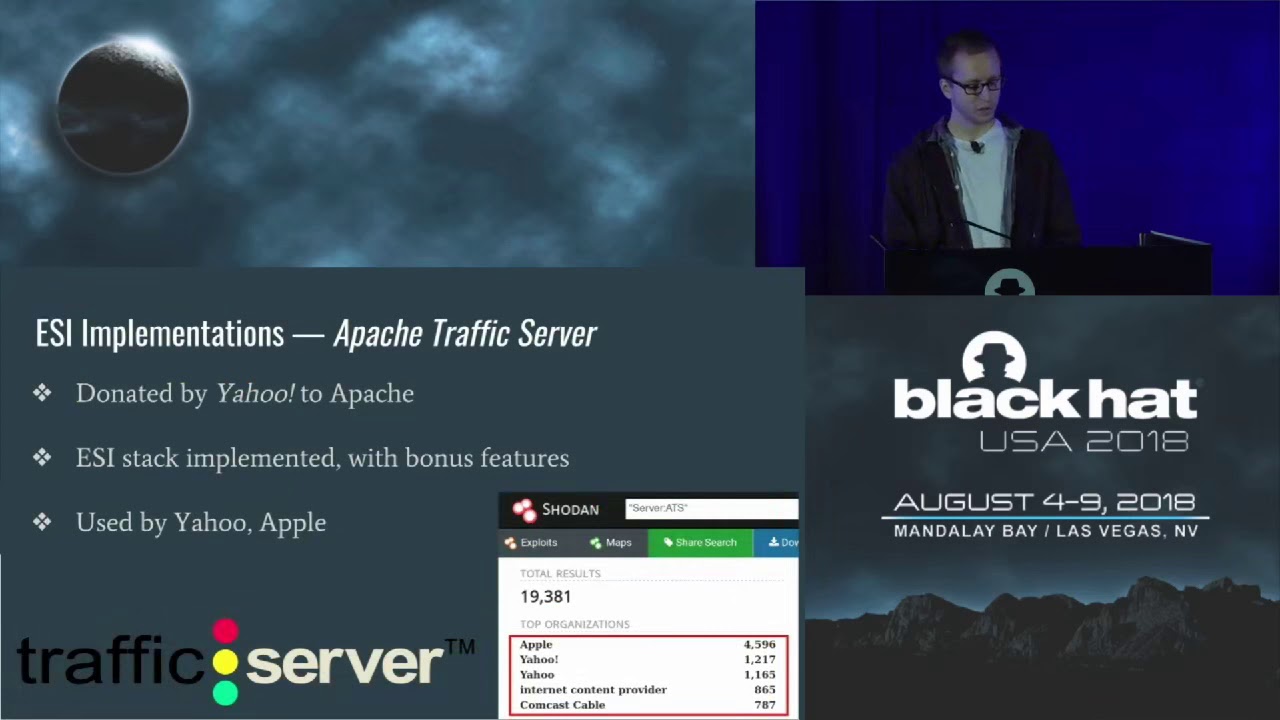
When caching servers and load balancers became an integral part of the Internet's infrastructure, vendors introduced what is called "Edge Side Includes" (ESI), a technology allowing malleability in caching systems. This legacy technology, still implemented in nearly all popular HTTP surrogates (caching/load balancing services), is dangerous by design and brings a yet unexplored vector for web-based attacks.
The ESI language consists of a small set of instructions represented by XML tags, served by the backend application server, which are processed on the Edge servers (load balancers, reverse proxies). Due to the upstream-trusting nature of Edge servers, the ESI engine tasked to parse and execute these instructions are not able to distinguish between ESI instructions legitimately provided by the application server, and malicious instructions injected by a malicious party. Through our research, we explored the risks that may be encountered through ESI injection: We identified that ESI can be used to perform SSRF, bypass reflected XSS filters (Chrome), and silently extract cookies. Because this attack vector leverages flaws on Edge servers and not on the client-side, the ESI engine can be reliably exploited to steal all cookies, including those protected by the HttpOnly mitigation flag, allowing JavaScript-less session hijacking.
Identified affected vendors include Akamai, Varnish Cache, Squid Proxy, Fastly, IBM WebSphere, Oracle WebLogic, F5, and countless language-specific solutions (NodeJS, Ruby, etc.). This presentation will start by defining ESI and visiting typical infrastructures leveraging this model. We will then delve into to the good stuff; identification and exploitation of popular ESI engines, and mitigation recommendations.
Black Hat USA 2018
When caching servers and load balancers became an integral part of the Internet's infrastructure, vendors introduced what is called "Edge Side Includes" (ESI), a technology allowing malleability in caching systems. This legacy technology, still implemented in nearly all popular HTTP surrogates (caching/load balancing services), is dangerous by design and brings a yet unexplored vector for web-based attacks.
The ESI language consists of a small set of instructions represented by XML tags, served by the backend application server, which are processed on the Edge servers (load balancers, reverse proxies). Due to the upstream-trusting nature of Edge servers, the ESI engine tasked to parse and execute these instructions are not able to distinguish between ESI instructions legitimately provided by the application server, and malicious instructions injected by a malicious party. Through our research, we explored the risks that may be encountered through ESI injection: We identified that ESI can be used to perform SSRF, bypass reflected XSS filters (Chrome), and silently extract cookies. Because this attack vector leverages flaws on Edge servers and not on the client-side, the ESI engine can be reliably exploited to steal all cookies, including those protected by the HttpOnly mitigation flag, allowing JavaScript-less session hijacking.
Identified affected vendors include Akamai, Varnish Cache, Squid Proxy, Fastly, IBM WebSphere, Oracle WebLogic, F5, and countless language-specific solutions (NodeJS, Ruby, etc.). This presentation will start by defining ESI and visiting typical infrastructures leveraging this model. We will then delve into to the good stuff; identification and exploitation of popular ESI engines, and mitigation recommendations.