Uploaded October 2019 | Updated September 2026, 5 days ago
Black Hat USA 2018
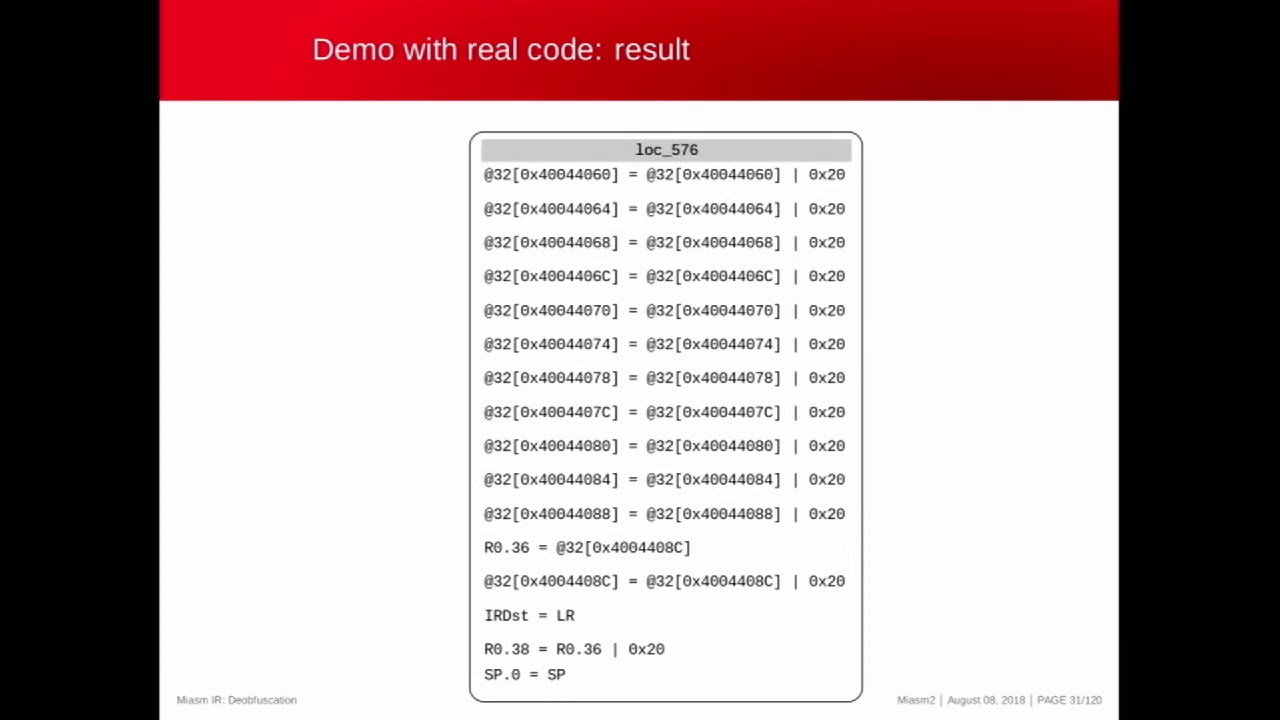
Miasm is a reverse engineering framework created in 2006 and first published in 2011 (GPL). Since then, it has been continuously improved through a daily use. The framework is made of several parts, including an assembler/disassembler for several architectures (x86, aarch64, arm, etc.), an human readable intermediate language describing their instructions' semantic, or sandboxing capabilities of Windows/Linux environment. On top of these foundations, higher level analysis are provided to address more complex tasks, such as variable backtracking and dynamic symbolic execution.
In this talk, we will introduce some of these features. The journey will start with the basics of the framework, go through symbolic emulation and function divination (Sibyl), and end with various components useful for malware analysis.
We will also talk about some of the new features which will be released for Black Hat. For example, the freshly implemented SSA transformation will be illustrated by applications in code simplification. Then, we will demonstrate how this feature, jointly with new operators description, enables more accurate code analyses. Finally, we will highlight what a better environment simulations and a wider support of recent instructions provides.
Miasm being a practical tool, each topic will be covered with real life use-cases.
Black Hat USA 2018
Miasm is a reverse engineering framework created in 2006 and first published in 2011 (GPL). Since then, it has been continuously improved through a daily use. The framework is made of several parts, including an assembler/disassembler for several architectures (x86, aarch64, arm, etc.), an human readable intermediate language describing their instructions' semantic, or sandboxing capabilities of Windows/Linux environment. On top of these foundations, higher level analysis are provided to address more complex tasks, such as variable backtracking and dynamic symbolic execution.
In this talk, we will introduce some of these features. The journey will start with the basics of the framework, go through symbolic emulation and function divination (Sibyl), and end with various components useful for malware analysis.
We will also talk about some of the new features which will be released for Black Hat. For example, the freshly implemented SSA transformation will be illustrated by applications in code simplification. Then, we will demonstrate how this feature, jointly with new operators description, enables more accurate code analyses. Finally, we will highlight what a better environment simulations and a wider support of recent instructions provides.
Miasm being a practical tool, each topic will be covered with real life use-cases.