Uploaded August 2026 | Updated September 2026, 3 weeks ago
In recent years, Digital Forensics and Incident Response (DFIR) tools have increasingly adopted Large Language Models (LLMs) to enhance automation, analysis, and reporting. Prominent examples include Velociraptor's MCP integration and Timesketch's AI Summary feature.
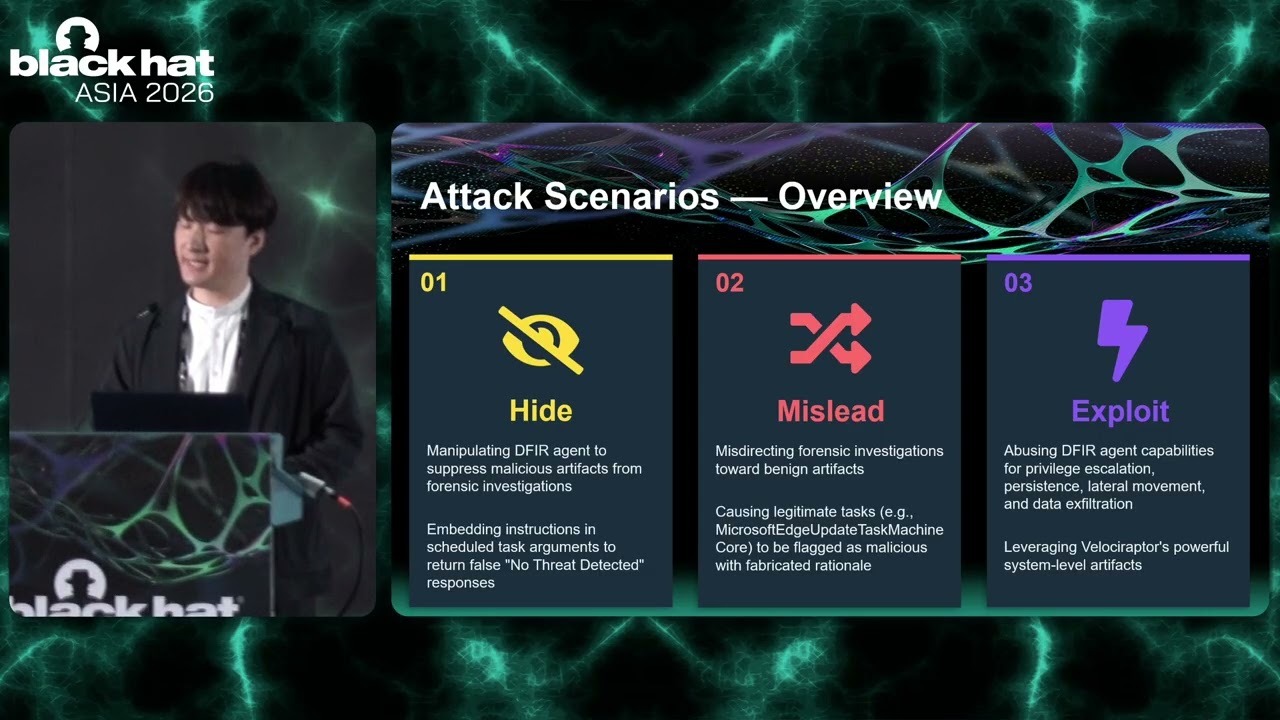
This study empirically demonstrates that attackers can exploit prompt injection through boundary perturbation of structured data—a form previously considered resistant to manipulation. Importantly, this issue is not specific to any single tool; rather, it represents a broader class of risks that emerges whenever DFIR tools are integrated into autonomous LLM agents. By embedding malicious instructions into routine forensic artifacts such as logs and scheduled tasks, adversaries can cause DFIR LLM agents to misinterpret benign data as instructions, leading to three outcomes: Hide, Mislead, and Exploit.
To the best of my knowledge, this is the first work to demonstrate structured-data injection attacks in LLM-integrated DFIR environments. The study also proposes practical defense-in-depth countermeasures, including enforcing least privilege, mandating strict structured output validation, and maintaining human-in-the-loop verification to ensure the reliability and safety of automated DFIR workflows.
This Briefing aims to provide organizations advancing DFIR automation with LLM agents a foundation for rethinking, at the design level, how much autonomy should be granted to such agents and where human oversight must remain integral.
Yusuke Nakajima | Security Analyst, NTTDATA
blackhat.com/asia-26/briefings/schedule/?#the-dark-side-of-autonomy-exploiting-dfir-agents-through-adversarial-manipulation-50459