Uploaded August 2026 | Updated September 2026, 3 weeks ago
Event Tracing for Windows (ETW) is a built-in Windows logging and tracing framework that collects system and application events, providing detailed visibility into what's happening on a machine. In security, ETW is widely leveraged as one of the key telemetry sources for modern Endpoint Detection and Response (EDR) products because of the wealth of data it provides.
This trace data is generated by components known as providers. While four types exist—Managed Object Format (MOF), Windows software trace preprocessor (WPP), Manifest-based, and TraceLogging—Microsoft generally recommends using the two modern variants: Manifest-based and TraceLogging providers [1].
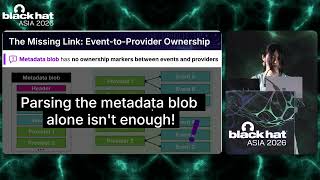
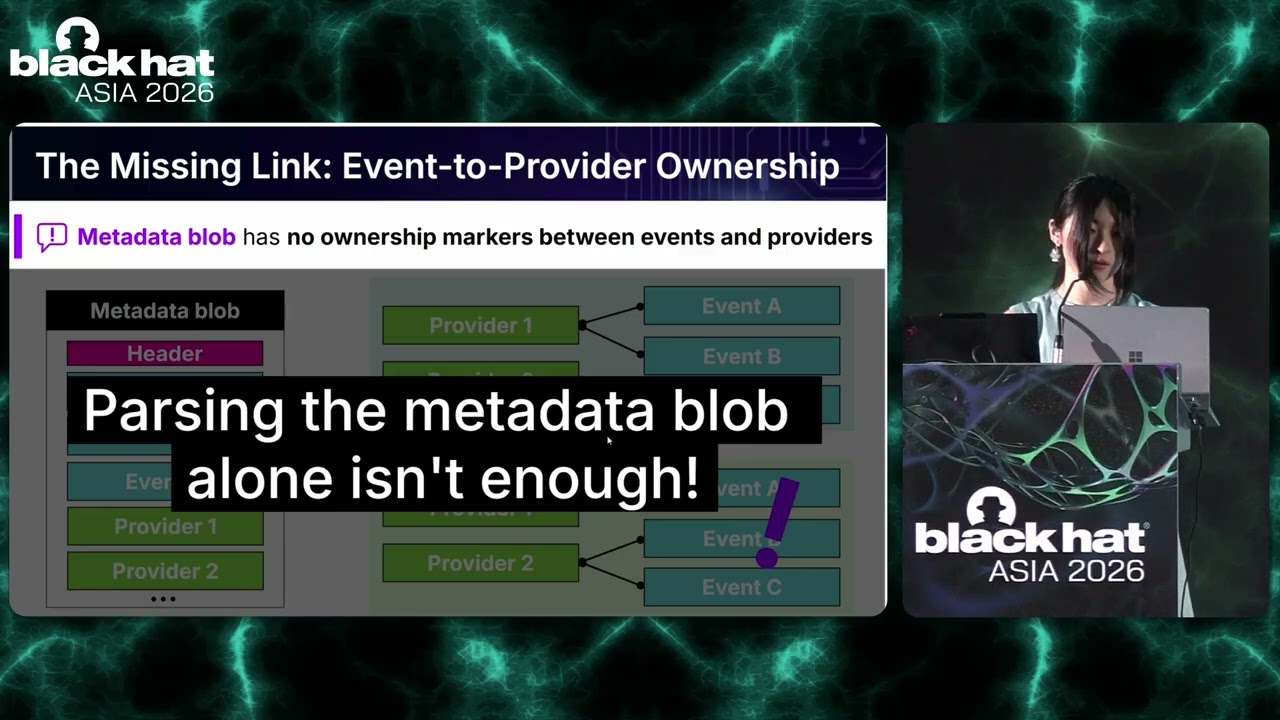
However, a significant knowledge gap exists. While Manifest-based providers are relatively well-understood [2], information regarding TraceLogging providers remains scarce. Consequently, it is questionable whether the security community is truly maximizing ETW's full potential.
To bridge this gap and enable defenders to better leverage ETW, we will present our findings on TraceLogging providers in the latest Windows. We will cover how to work with them, highlight providers potentially useful for security (e.g., AttackSurfaceMonitor), and walk through practical use cases.
Asuka Nakajima | Senior Security Research Engineer, Elastic
blackhat.com/asia-26/briefings/schedule/?#hidden-telemetry-uncovering-tracelogging-etw-providers-youre-not-using-yet-51991