Uploaded August 2026 | Updated September 2026, 2 days ago
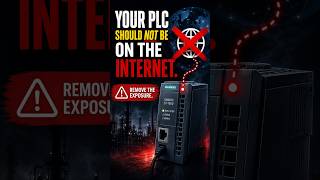
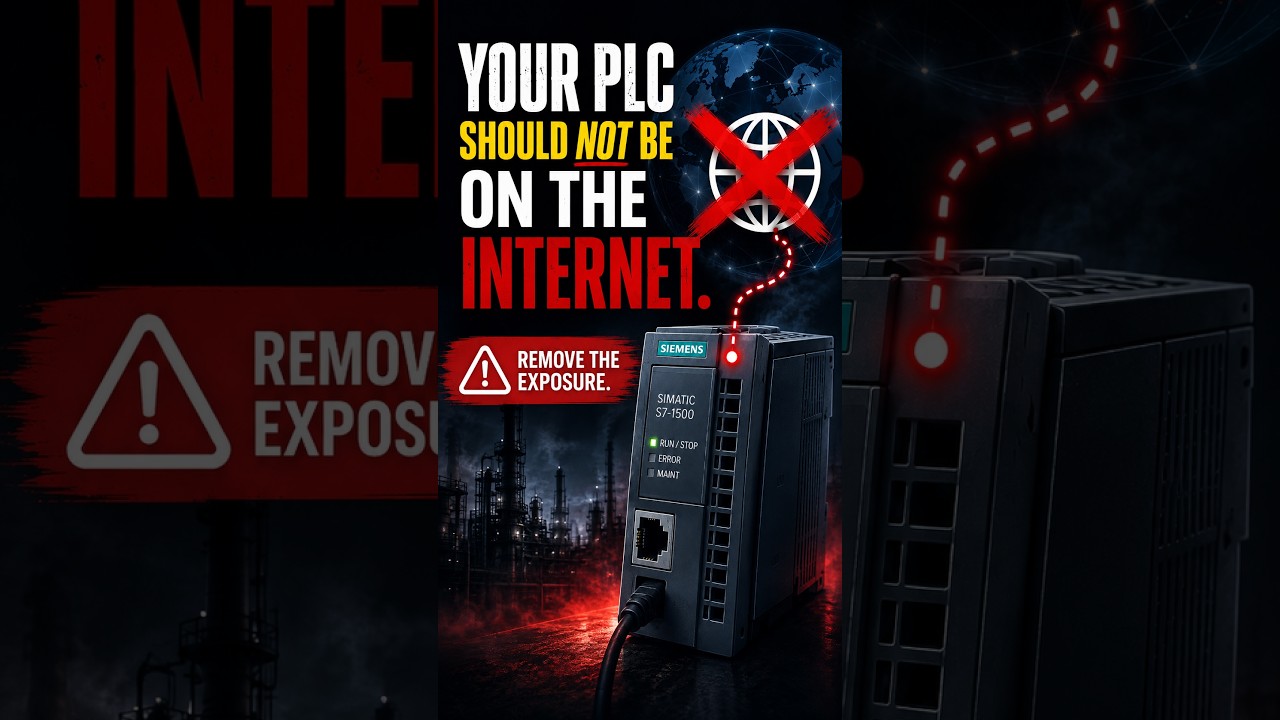
The first response to an Internet-exposed PLC shouldn’t be complicated.
Remove the direct Internet access.
Then review your network segmentation and make sure only legitimate systems—such as engineering stations and HMI servers—can communicate with the PLC.
Before chasing sophisticated attack scenarios, address the root exposure.
Get it off the Internet. Then lock down who can talk to it.
#OTSecurity #PLC #Siemens #NetworkSegmentation #Cybersecurity #Shorts
The first response to an Internet-exposed PLC shouldn’t be complicated.
Remove the direct Internet access.
Then review your network segmentation and make sure only legitimate systems—such as engineering stations and HMI servers—can communicate with the PLC.
Before chasing sophisticated attack scenarios, address the root exposure.
Get it off the Internet. Then lock down who can talk to it.
#OTSecurity #PLC #Siemens #NetworkSegmentation #Cybersecurity #Shorts