Uploaded November 2026 | Updated November 2026, 2 days ago
Biography:
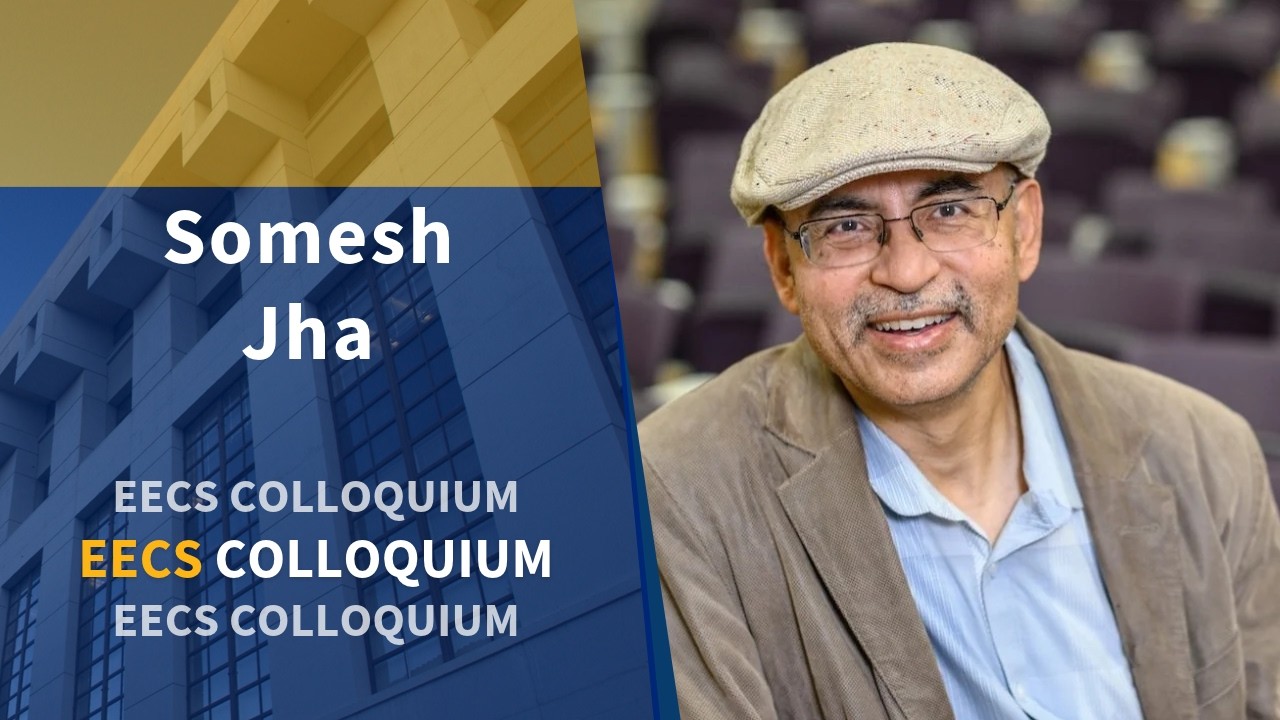
Somesh Jha received his B.Tech from Indian Institute of Technology, New Delhi in Electrical Engineering. He received his Ph.D. in Computer Science from Carnegie Mellon University under the supervision of Prof. Edmund Clarke (a Turing award winner). Currently, Somesh Jha is the Lubar Professor in the Computer Sciences Department at the University of Wisconsin (Madison). His work focuses on analysis of security protocols, survivability analysis, intrusion detection, formal methods for security, and analyzing malicious code. Recently, he has focused on trustworthy ML. Somesh Jha has published several articles in highly referenced conferences and prominent journals. He has won numerous best-paper and distinguished-paper awards. Prof. Jha received the CAV award for his work on CEGAR and also has received the IIT-Delhi Distinguished Alumni award. Prof. Jha is a fellow of the ACM, IEEE, and AAAS.
Abstract:
In this talk, we take the position that agent security must be approached as a systems problem: the AI model powering the agent must be treated as an untrusted component, and security invariants must be enforced at the system level. Through this lens, efforts to increase model robustness (the dominant viewpoint in the ML community) are insufficient on their own. Instead, we must complement existing efforts with techniques from the systems security domain. We will cover some example solutions that follow this viewpoint, and discuss their pros and cons. We will also identify the challenges that stand in the way of implementing these principles in agents.
EECS Colloquium
Wednesday November 18, 2026
1220 Gateway
4 - 5p
Biography:
Somesh Jha received his B.Tech from Indian Institute of Technology, New Delhi in Electrical Engineering. He received his Ph.D. in Computer Science from Carnegie Mellon University under the supervision of Prof. Edmund Clarke (a Turing award winner). Currently, Somesh Jha is the Lubar Professor in the Computer Sciences Department at the University of Wisconsin (Madison). His work focuses on analysis of security protocols, survivability analysis, intrusion detection, formal methods for security, and analyzing malicious code. Recently, he has focused on trustworthy ML. Somesh Jha has published several articles in highly referenced conferences and prominent journals. He has won numerous best-paper and distinguished-paper awards. Prof. Jha received the CAV award for his work on CEGAR and also has received the IIT-Delhi Distinguished Alumni award. Prof. Jha is a fellow of the ACM, IEEE, and AAAS.
Abstract:
In this talk, we take the position that agent security must be approached as a systems problem: the AI model powering the agent must be treated as an untrusted component, and security invariants must be enforced at the system level. Through this lens, efforts to increase model robustness (the dominant viewpoint in the ML community) are insufficient on their own. Instead, we must complement existing efforts with techniques from the systems security domain. We will cover some example solutions that follow this viewpoint, and discuss their pros and cons. We will also identify the challenges that stand in the way of implementing these principles in agents.
EECS Colloquium
Wednesday November 18, 2026
1220 Gateway
4 - 5p