Uploaded November 2026 | Updated November 2026, 6 days ago
Prabhu Barathi and Aaron Woland of Cisco explained how Cisco is extending zero trust to AI agents as part of securing the workforce. They covered why agents require a shift from access control to action control, agent and non-human identity discovery in Cisco Cloud Control, stream-level visibility through Cisco Secure Client, and authorization for agents based on OAuth 2.1. The session opened the secure the workforce portion of Cisco Security’s appearance at Security Field Day 16.
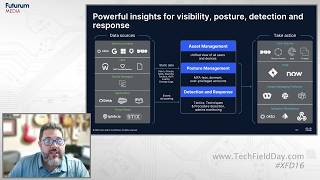
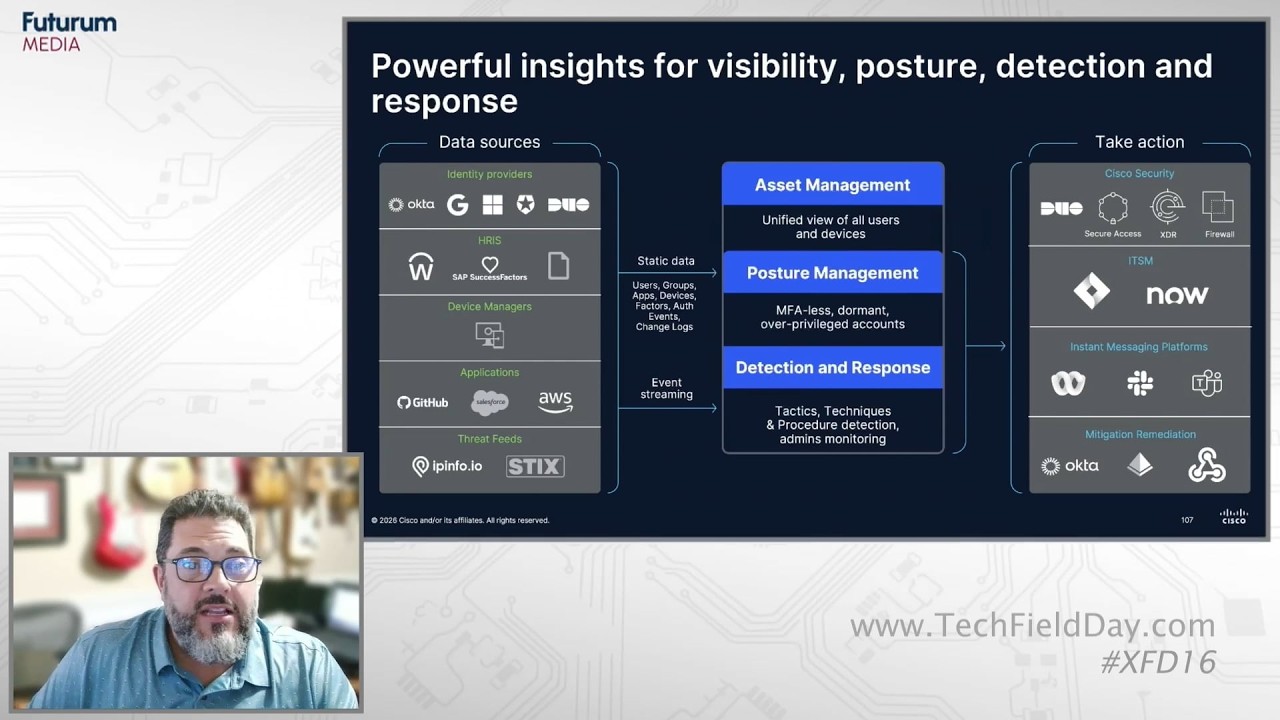
Barathi, a global security technologist focused on SASE and identity, said a single agent request spawns many machine-to-machine tasks across SaaS APIs, MCP connectors, and enterprise apps. Any delay in those tasks hurts the business, and users blame the network. Agents combine broad data access with machine speed but lack human judgment and fear of consequences. He grouped zero trust for agents into three areas: knowing every agent, authorizing actions, and adapting to risk in real time. Woland, a distinguished engineer focused on identity, said the identity app in Cisco Cloud Control unifies human, device, and agent identities using technology from the Oort and Astrix acquisitions. It combines signals from EDR tools, AI platforms, identity providers, and HR systems like Workday. That lets it identify individual agent instances and sub-agents, and flag agents left running after their owners depart.
Woland said Cisco Secure Client runs on more than 250 million endpoints. Its stream-level interceptor records agent traffic metadata before encryption, without capturing payloads or interfering with VPNs. Its agentic module includes Defense Claw, whose enterprise version is being renamed AI Defense for Endpoints, plus osquery for inventory. It feeds the identity app, AI Defense, the firewall, and Splunk Agent Observability. For authorization, MCP servers or the agent gateway route agents through OAuth 2.1 dynamic client registration. Duo or a third-party identity provider then issues fine-grained tokens for just-in-time, just-enough, just-long-enough access. Woland noted that an inactive accounts check recently helped one customer remove more than 140 stale accounts.
Presented by Aaron Woland, Distinguished Technical Marketing Engineer, and Prabhu Barathi, Global Security Technologist. Recorded live at Security Field Day 16 in San Jose, CA on October 28, 2026. Watch the entire presentation at techfieldday.com/appearance/cisco-security-presents-at-security-field-day-16 or visit techfieldday.com/event/xfd16 or Cisco.com for more information.
Prabhu Barathi and Aaron Woland of Cisco explained how Cisco is extending zero trust to AI agents as part of securing the workforce. They covered why agents require a shift from access control to action control, agent and non-human identity discovery in Cisco Cloud Control, stream-level visibility through Cisco Secure Client, and authorization for agents based on OAuth 2.1. The session opened the secure the workforce portion of Cisco Security’s appearance at Security Field Day 16.
Barathi, a global security technologist focused on SASE and identity, said a single agent request spawns many machine-to-machine tasks across SaaS APIs, MCP connectors, and enterprise apps. Any delay in those tasks hurts the business, and users blame the network. Agents combine broad data access with machine speed but lack human judgment and fear of consequences. He grouped zero trust for agents into three areas: knowing every agent, authorizing actions, and adapting to risk in real time. Woland, a distinguished engineer focused on identity, said the identity app in Cisco Cloud Control unifies human, device, and agent identities using technology from the Oort and Astrix acquisitions. It combines signals from EDR tools, AI platforms, identity providers, and HR systems like Workday. That lets it identify individual agent instances and sub-agents, and flag agents left running after their owners depart.
Woland said Cisco Secure Client runs on more than 250 million endpoints. Its stream-level interceptor records agent traffic metadata before encryption, without capturing payloads or interfering with VPNs. Its agentic module includes Defense Claw, whose enterprise version is being renamed AI Defense for Endpoints, plus osquery for inventory. It feeds the identity app, AI Defense, the firewall, and Splunk Agent Observability. For authorization, MCP servers or the agent gateway route agents through OAuth 2.1 dynamic client registration. Duo or a third-party identity provider then issues fine-grained tokens for just-in-time, just-enough, just-long-enough access. Woland noted that an inactive accounts check recently helped one customer remove more than 140 stale accounts.
Presented by Aaron Woland, Distinguished Technical Marketing Engineer, and Prabhu Barathi, Global Security Technologist. Recorded live at Security Field Day 16 in San Jose, CA on October 28, 2026. Watch the entire presentation at techfieldday.com/appearance/cisco-security-presents-at-security-field-day-16 or visit techfieldday.com/event/xfd16 or Cisco.com for more information.