Uploaded April 2021 | Updated September 2026, 1 hour ago
Presenters: Nisha Kumar, VMware, Brandon Lum, IBM, Steve Lasker, Microsoft, Louis DeLosSantos, Red Hat
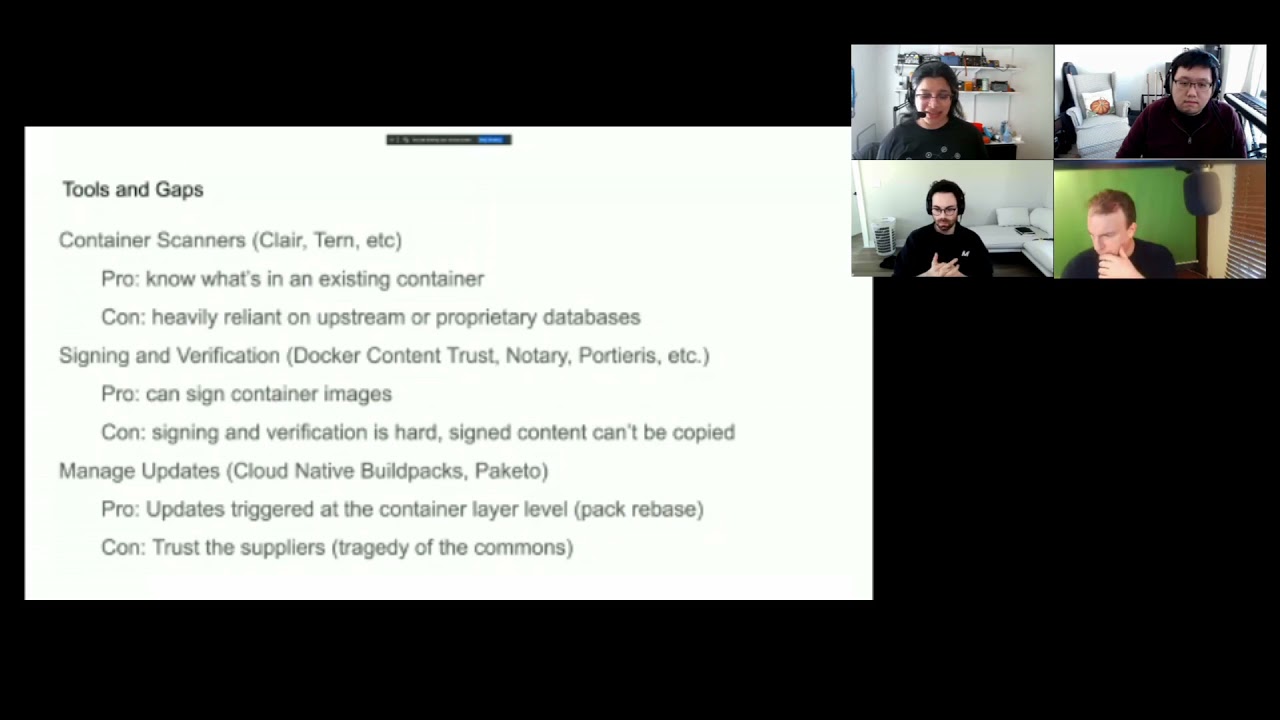
Securing the Software Supply Chain has rapidly become a top concern for Open Source communities. There are many initiatives, most notably, the work by GitHub, to track and audit source code dependencies. However, this level of scrutiny is not applied when building container images, even though the resulting artifact is the product of various software supply chains, from the base OS’s package manager to the system dependencies required to make the top level application work. There are currently several projects trying to address the specific concerns of securing the supply chain for containers. These include the work of Notary V2, In-toto, OCI Artifacts, and Tern, in conjunction with the work of the CNCF’s SIG-Security Secure Supply Chain Security Working Group. Come join the discussion on how these projects may facilitate Open Source communities securing their container builds, and address any gaps that are currently present.
Presenters: Nisha Kumar, VMware, Brandon Lum, IBM, Steve Lasker, Microsoft, Louis DeLosSantos, Red Hat
Securing the Software Supply Chain has rapidly become a top concern for Open Source communities. There are many initiatives, most notably, the work by GitHub, to track and audit source code dependencies. However, this level of scrutiny is not applied when building container images, even though the resulting artifact is the product of various software supply chains, from the base OS’s package manager to the system dependencies required to make the top level application work. There are currently several projects trying to address the specific concerns of securing the supply chain for containers. These include the work of Notary V2, In-toto, OCI Artifacts, and Tern, in conjunction with the work of the CNCF’s SIG-Security Secure Supply Chain Security Working Group. Come join the discussion on how these projects may facilitate Open Source communities securing their container builds, and address any gaps that are currently present.


