Uploaded December 2012 | Updated September 2026, 2 weeks ago
Merry Christmas everyone and thank you for 2,000 subscribers! (Though, it's not much activity these days.)
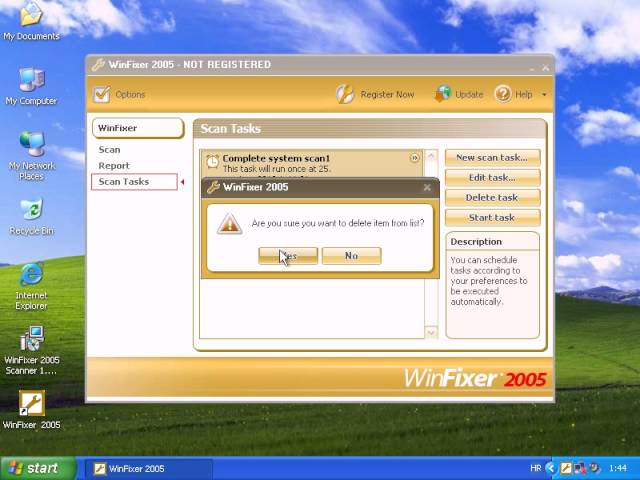
After searching and digging, I'll demonstrate the infamous WinFixer, the "WinSoftware" which started with all those fake products.
I've only managed to get 4 different variants. You'll know which version is shown in video.
Variants:
2005: Trial (Supposed to be fully featured and time limited), Scanner and Full version.
2006: Free version.
Pretty much this rogue didn't causeany fake reports, but it does cause lots of false positives and whatever misleading details. However, the full version seems to work completely as it should.
I could have posted few more versions, but there were no specific differences in general, so I've posted these with most major changes (sort of) and for whole check video would be 2 hours long.
This isn't the only thing which I'll show. There are other videos related with WinSoftware.
Enjoy and thanks!
Merry Christmas everyone and thank you for 2,000 subscribers! (Though, it's not much activity these days.)
After searching and digging, I'll demonstrate the infamous WinFixer, the "WinSoftware" which started with all those fake products.
I've only managed to get 4 different variants. You'll know which version is shown in video.
Variants:
2005: Trial (Supposed to be fully featured and time limited), Scanner and Full version.
2006: Free version.
Pretty much this rogue didn't causeany fake reports, but it does cause lots of false positives and whatever misleading details. However, the full version seems to work completely as it should.
I could have posted few more versions, but there were no specific differences in general, so I've posted these with most major changes (sort of) and for whole check video would be 2 hours long.
This isn't the only thing which I'll show. There are other videos related with WinSoftware.
Enjoy and thanks!



![E-mail Worm (Visual Basic Script): Timofonica.A
This is a VBS (Visual Basic Script) E-mail worm which sends mail to all contacts and for each contact it sends an SMS to some number through MoviStar service (NOTE: I havent done research about MoviStar service and therefore any info I say about it might be incorrect).
In addition, it drops a trojan horse in System directory named CMOS.COM which destroys CMOS information and information on hard disks. It might be possible that only boot information is deleted and all data should be fine. However, I havent tested that, but as far as I know, there should be no way to destroy hard drive data from Windows which could cause errors (FlashKiller is the only exception in this case, but it may cause BSODs). Therefore, I would consider that only boot information is gone, but everything else should be fine.
There are 2 more variants. Timofonica.B variant is just based on Apache, while Timofonica.C variant removed trojan horse part in code.
Aliases:
Email-Worm.VBS.Timofonica (Kaspersky Lab)
I-Worm.Timofonica (Kaspersky Lab)
Virus: VBS/Generic@MM (McAfee)
VBS/Timo-A (Sophos)
Worm.Timofonica (ClamAV)
VBS/Timofonica (Panda)
VBS/Timofon.B@m (FPROT)
Virus:VBS/Timofon.A (MS(OneCare))
VBS.Timofonica (DrWeb)
Generic.ScriptWorm.B15CB7EF (BitDef7)
VBS.Timofonica (VirusBuster)
VBS:MailWorm-gen [Wrm] (AVAST)
Email-Worm.VBS.Timofonica (Ikarus)
VBS/Timofon.A (AVG)
VBS/Timofonica (AVIRA)
VBS.Timofonica (NAV)
VBS/Timofon.A@mm (Norman)
VBS/Generic@MM (NAI)
VBS_TIMOFONICA (PCCIL)
VBS.Worm.Zokrim.z (Rising)
VBS/Timofon.B@mm [Libra] (FSecure)
VBS_TIMOFONICA (TrendMicro) E-mail Worm (Visual Basic Script): Timofonica.A](https://i.ytimg.com/vi/fMeeK2RA_As/mqdefault.jpg)


![Virus (DOS): IDEA.6126
Payload of this virus is activated at 15:30 (by that I mean system time), and shows a spinning video effect with text Warning! strong crypto inside.
Additionally, this virus can infect ZIP files when they are accessed by FindFirst/Next DOS commands (like using dir command to list a file) by dropping a infected copy named readme.com. After 6-7 tries to zip and unzip it and whatever, you can see 3 more video effect payloads, containing text:
Da BeSt BoaRd In SPaiN: El GriLLo Loco (34-1-352 24 45)
Downloaded From hxxp://wxx.narkotic.com/~vico (Cant confirm anything about website, not safe at some point.)
* ROADKILL BBS * Call now 028-6621590
Ive added to end of video slowed down versions of first two payloads so that you can see the text properly.
Aliases:
Virus.DOS.IDEA.6126 (Kaspersky Lab)
Virus: Idea.6126 (McAfee)
Idea-6126 (Sophos)
VGEN.51495 (ClamAV)
Spanska.6126 (FPROT)
Virus:DOS/Spanska.6126 (MS(OneCare))
Spanska.6126 (DrWeb)
Spanska.6126 (BitDef7)
Idea-6126 (AVAST)
Virus.DOS.IDEA (Ikarus)
Spanska.6180 (NAV)
Suspicious_Gen2.EHZCE (Norman)
Virus.DOS.IDEA.6126 [AVP] (FSecure)
IDEA.1626-O (TrendMicro) Virus (DOS): IDEA.6126](https://i.ytimg.com/vi/h1wmMYYB1S8/mqdefault.jpg)