Uploaded March 2026 | Updated September 2026, 1 week ago
Edwige Cyffers (CNRS)
https://simons.berkeley.edu/talks/edwige-cyffers-cnrs-2026-02-24
Learning from Heterogeneous Sources
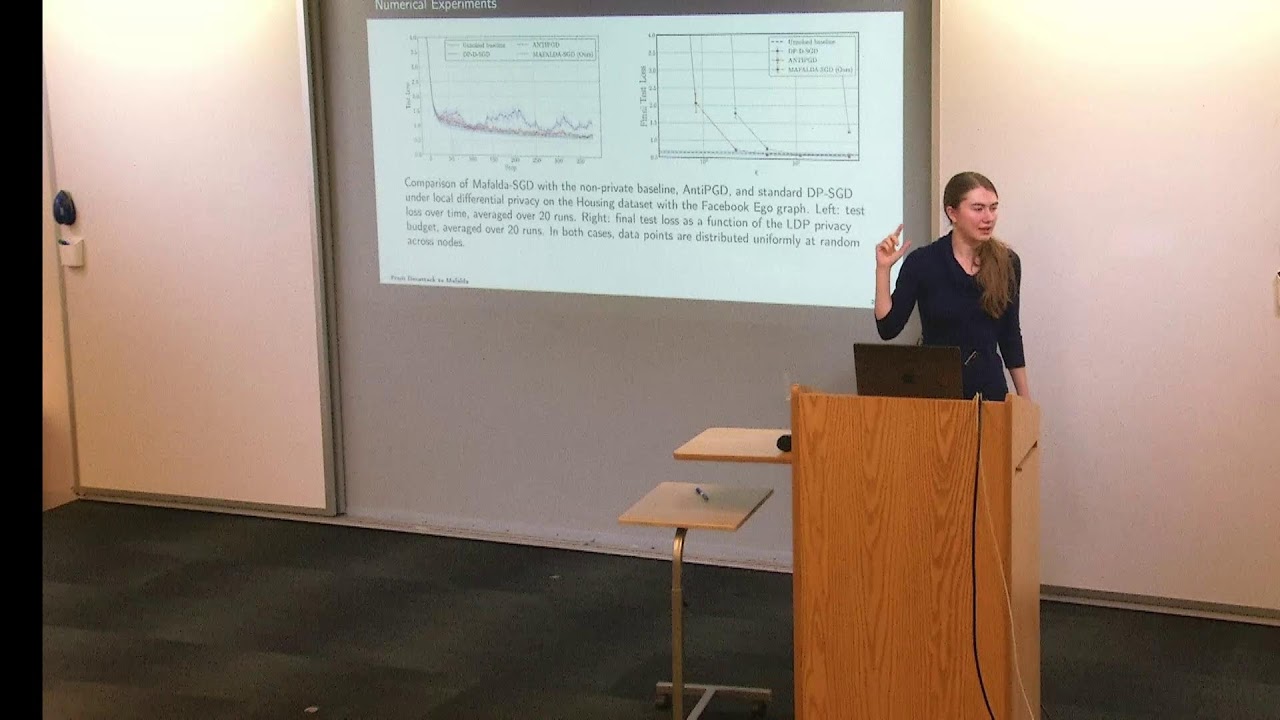
Even in decentralized learning, we show that data can be leaked through the training of machine learning models, motivating the need for protection mechanisms. While differential privacy is the gold standard for centralized privacy-preserving machine learning, it is not well suited to decentralized learning, where participants collaboratively train a model via peer-to-peer messages. We present a relaxation of differential privacy that captures a relevant trust setting for decentralized learning. We show that decentralization can lead to a better privacy-utility tradeoff in this regime.
Edwige Cyffers (CNRS)
https://simons.berkeley.edu/talks/edwige-cyffers-cnrs-2026-02-24
Learning from Heterogeneous Sources
Even in decentralized learning, we show that data can be leaked through the training of machine learning models, motivating the need for protection mechanisms. While differential privacy is the gold standard for centralized privacy-preserving machine learning, it is not well suited to decentralized learning, where participants collaboratively train a model via peer-to-peer messages. We present a relaxation of differential privacy that captures a relevant trust setting for decentralized learning. We show that decentralization can lead to a better privacy-utility tradeoff in this regime.