Uploaded November 2026 | Updated November 2026, 17 hours ago
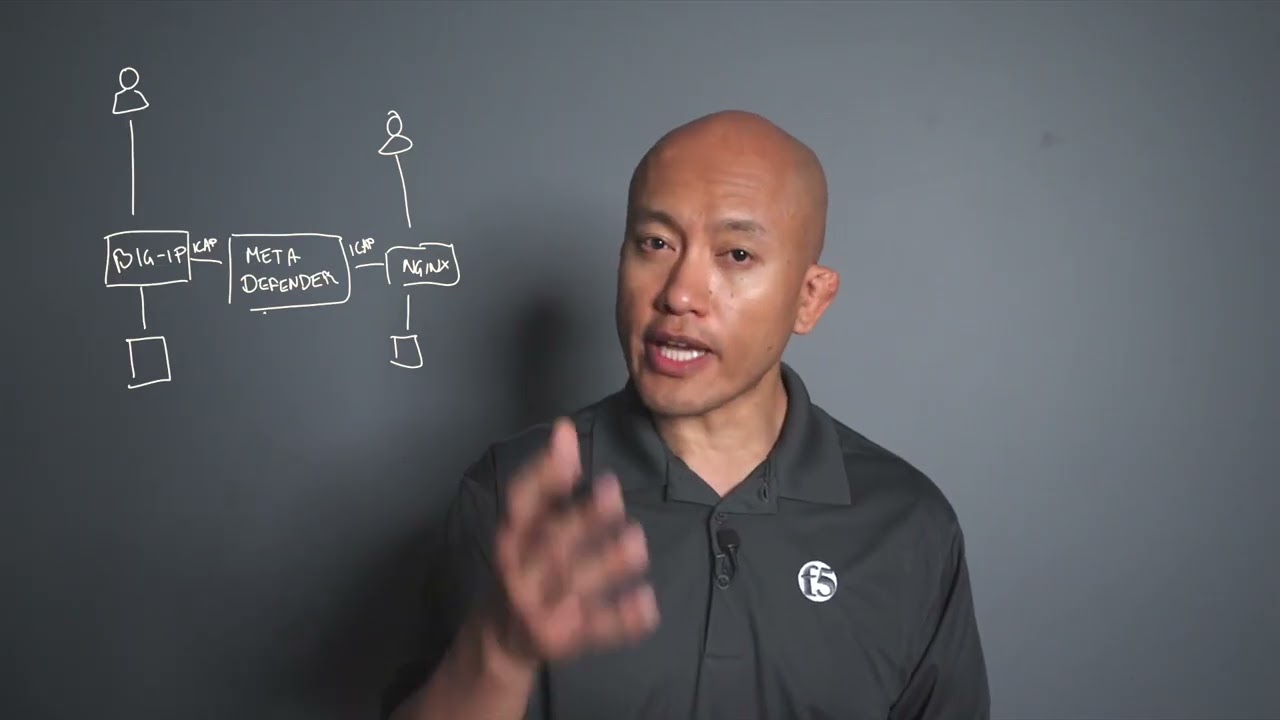
This video explains how OPSWAT MetaDefender and F5 products work together to inspect both the traffic and the file contents entering your organization. The goal is to stop malicious payloads regardless of source trust and to sanitize files containing risky content before delivery.
What the video covers:
- How ICAP, a command and response protocol, passes verdicts between F5 and OPSWAT, and how it can return adjusted payloads once files are cleansed
- How F5 BIG-IP Local Traffic Manager, F5 BIG-IP Application Security Manager, and NGINX steer traffic to MetaDefender over ICAP for inspection, returning allow or block decisions
- Why layered detection matters: more than 30 independent antivirus engines, plus AI and machine learning pre-execution detection (OPSWAT Predictive AI) running alongside MetaScan
- Adaptive sandboxing for suspicious files that evade signature detection, surfacing behavior-based indicators
- Deep content disarm and reconstruction (Deep CDR), which removes macros, JavaScript, and embedded objects while rebuilding the file so users still get a usable document
- OPSWAT AI content inspector, which assesses whether documents such as invoices, claims, or identity documents are authentic, with allow, flag, block, or review verdicts returned to F5
- How F5 Distributed Cloud extends these protections to cloud-native deployments, including NGINX as a container on a customer edge node with the OPSWAT module
- Software Bill of Materials (SBOM) analysis from OPSWAT, covering source code in more than 10 programming languages and more than 5 million recognized third-party open source components, to address software supply chain risk
Why it matters: signatures handle known malware, while pre-execution AI detection, sandboxing, and content disarm address zero-day threats and weaponized documents before they reach downstream workflows. The same posture applies whether you run BIG-IP in traditional architecture or NGINX on an F5 Distributed Cloud customer edge.
Keywords: OPSWAT, MetaDefender, F5 BIG-IP, F5 Distributed Cloud, NGINX, ICAP, Deep CDR, content disarm and reconstruction, malware detection, sandboxing, file inspection, SBOM, software supply chain security, web application security, DevCentral
▬▬▬ ABOUT DEVCENTRAL ▬▬▬
We're DevCentral: the how of F5, since 2003. A community of engineers, architects, and IT folks pushing each other forward, one hard-won answer at a time. We dig in, tackle the hard stuff, figure out what actually works, and share what we learn.
Keep going:
Forums, articles, CodeShare: community.f5.com
LinkedIn: linkedin.com/showcase/f5-devcentral
X: https://x.com/devcentral
The DevCentral advocates behind the videos:
Alessandro Fael Garcia → linkedin.com/in/alessfg · github.com/alessfg
Buu Lam → linkedin.com/in/buulam · https://x.com/buulam
Chase Abbott → linkedin.com/in/chaseabbott1
Jason Rahm → linkedin.com/in/jrahm · https://x.com/jasonrahm
Marko Sluga → linkedin.com/in/markosluga
Scott McAllister → linkedin.com/in/stmcallister
This video explains how OPSWAT MetaDefender and F5 products work together to inspect both the traffic and the file contents entering your organization. The goal is to stop malicious payloads regardless of source trust and to sanitize files containing risky content before delivery.
What the video covers:
- How ICAP, a command and response protocol, passes verdicts between F5 and OPSWAT, and how it can return adjusted payloads once files are cleansed
- How F5 BIG-IP Local Traffic Manager, F5 BIG-IP Application Security Manager, and NGINX steer traffic to MetaDefender over ICAP for inspection, returning allow or block decisions
- Why layered detection matters: more than 30 independent antivirus engines, plus AI and machine learning pre-execution detection (OPSWAT Predictive AI) running alongside MetaScan
- Adaptive sandboxing for suspicious files that evade signature detection, surfacing behavior-based indicators
- Deep content disarm and reconstruction (Deep CDR), which removes macros, JavaScript, and embedded objects while rebuilding the file so users still get a usable document
- OPSWAT AI content inspector, which assesses whether documents such as invoices, claims, or identity documents are authentic, with allow, flag, block, or review verdicts returned to F5
- How F5 Distributed Cloud extends these protections to cloud-native deployments, including NGINX as a container on a customer edge node with the OPSWAT module
- Software Bill of Materials (SBOM) analysis from OPSWAT, covering source code in more than 10 programming languages and more than 5 million recognized third-party open source components, to address software supply chain risk
Why it matters: signatures handle known malware, while pre-execution AI detection, sandboxing, and content disarm address zero-day threats and weaponized documents before they reach downstream workflows. The same posture applies whether you run BIG-IP in traditional architecture or NGINX on an F5 Distributed Cloud customer edge.
Keywords: OPSWAT, MetaDefender, F5 BIG-IP, F5 Distributed Cloud, NGINX, ICAP, Deep CDR, content disarm and reconstruction, malware detection, sandboxing, file inspection, SBOM, software supply chain security, web application security, DevCentral
▬▬▬ ABOUT DEVCENTRAL ▬▬▬
We're DevCentral: the how of F5, since 2003. A community of engineers, architects, and IT folks pushing each other forward, one hard-won answer at a time. We dig in, tackle the hard stuff, figure out what actually works, and share what we learn.
Keep going:
Forums, articles, CodeShare: community.f5.com
LinkedIn: linkedin.com/showcase/f5-devcentral
X: https://x.com/devcentral
The DevCentral advocates behind the videos:
Alessandro Fael Garcia → linkedin.com/in/alessfg · github.com/alessfg
Buu Lam → linkedin.com/in/buulam · https://x.com/buulam
Chase Abbott → linkedin.com/in/chaseabbott1
Jason Rahm → linkedin.com/in/jrahm · https://x.com/jasonrahm
Marko Sluga → linkedin.com/in/markosluga
Scott McAllister → linkedin.com/in/stmcallister