Uploaded February 2017 | Updated November 2026, 2 hours ago
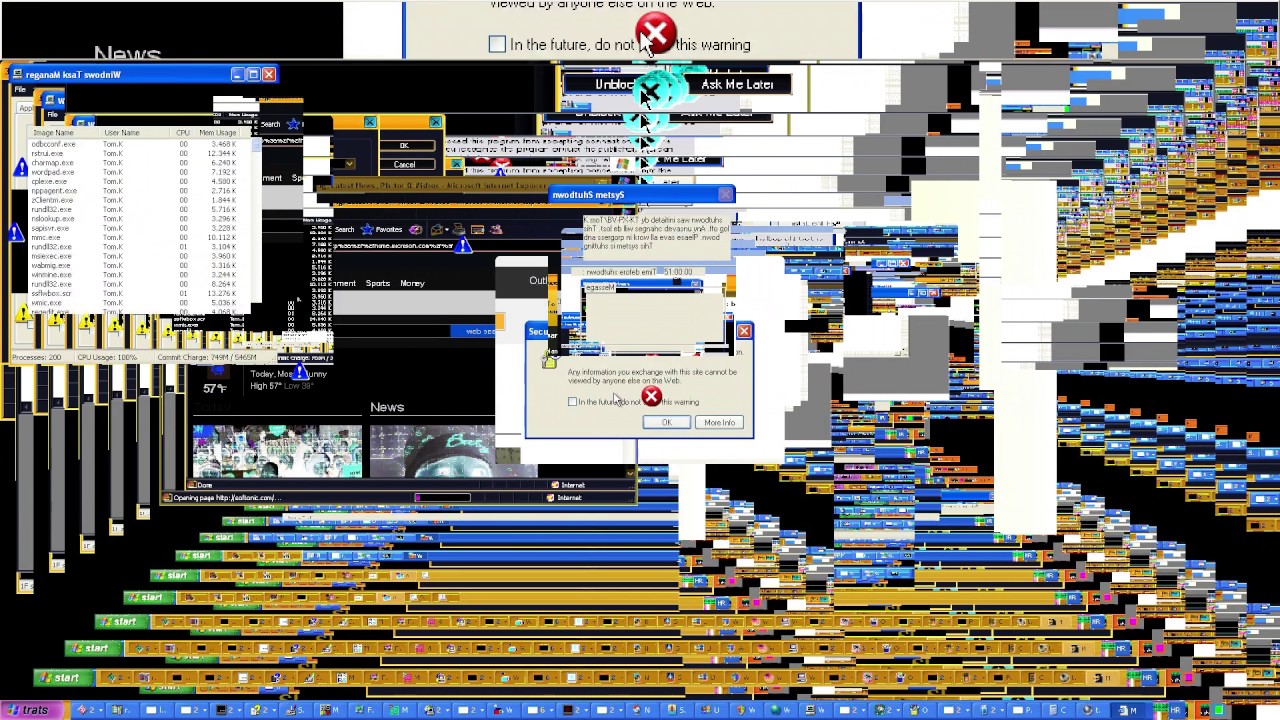
Overloading Windows XP with 400 programs, with few differences from first vid. I'm not searching for stuff, I just run everything that's possible, along with few loops to screw it up even more.
Derek asked me to make a video on MEMZ, so I've just combined overload with it, because doing it solo is not much of use when everyone else already did that with MEMZ itself.
Also, this is now 1080p with 60 FPS. I'm finally done with recording configuration.
Yes, the job caused a LONG delay. Developing for Android platform isn't easy, especially with goddamn deadlines and with small work experience, but that managed to create this video, though.
Overloading Windows XP with 400 programs, with few differences from first vid. I'm not searching for stuff, I just run everything that's possible, along with few loops to screw it up even more.
Derek asked me to make a video on MEMZ, so I've just combined overload with it, because doing it solo is not much of use when everyone else already did that with MEMZ itself.
Also, this is now 1080p with 60 FPS. I'm finally done with recording configuration.
Yes, the job caused a LONG delay. Developing for Android platform isn't easy, especially with goddamn deadlines and with small work experience, but that managed to create this video, though.



![E-mail Worm (Windows): Android
No, this is not about a worm which will show green robot or any kind of smartphone related thing, etc.
When activated, it drops ULTRAS.DLL and ANDROID.DLL to Windows directory, but also creates Wininit.ini file which in this case is used to replace WSOCK32.DLL with ULTRAS.DLL on reboot by renaming WSOCK32.DLL to WSOCK33.DLL and ULTRAS.DLL to WSOCK32.DLL. That way worm has access to network features. Worm forwards all requests to original WSOCK32 as worm itself doesnt have such features. Its supposed to add an attachment of itself to every e-mail being sent, but its not possible to demonstrate as I dont have such ability to simulate network.
On 5th of every month, worm will replace system wallpaper with ANDROID.BMP. To make it work properly, it requires Active Desktop disabled (otherwise it will show up only at logging off).
Destructive payload is supposed to happen after a week of being infected, which is deleting all files with ICO, DOC, TXT, HTM, JPG, GIF, ZIP, RAR extensions on local and remote drives, but it doesnt seem to work for me.
Dont be a fool if its called Android. Back then there were no such smartphones.
Aliases:
Email-Worm.Win32.Android (Kaspersky Lab)
I-Worm.Android (Kaspersky Lab)
Virus: W95/Android@M (McAfee)
W32/Android-A (Sophos)
Trojan.Suppl.Worm (ClamAV)
W32/Android (Panda)
W32/Malware!eb33 (FPROT)
Worm:Win32/Android@mm (MS(OneCare))
Win32.Suppl.40960 (DrWeb)
Win32/Android worm (Nod32)
Win32.Android.A@mm (BitDef7)
Win32.Android.B (VirusBuster)
Win32:Android [Wrm] (AVAST)
Email-Worm.MSWord.Suppl (Ikarus)
I-Worm/Android (AVG)
TR/Suppl.Worm_#1 (AVIRA)
W32.Android.Worm (NAV)
W32/Android.40960 (Norman)
W95/Android@M (NAI)
WORM_ANDROID.A (PCCIL)
Worm.Android (Rising)
WORM_ANDROID.A (TrendMicro) E-mail Worm (Windows): Android](https://i.ytimg.com/vi/KXhxGZPzQ38/mqdefault.jpg)