Uploaded May 2026 | Updated September 2026, 1 week ago
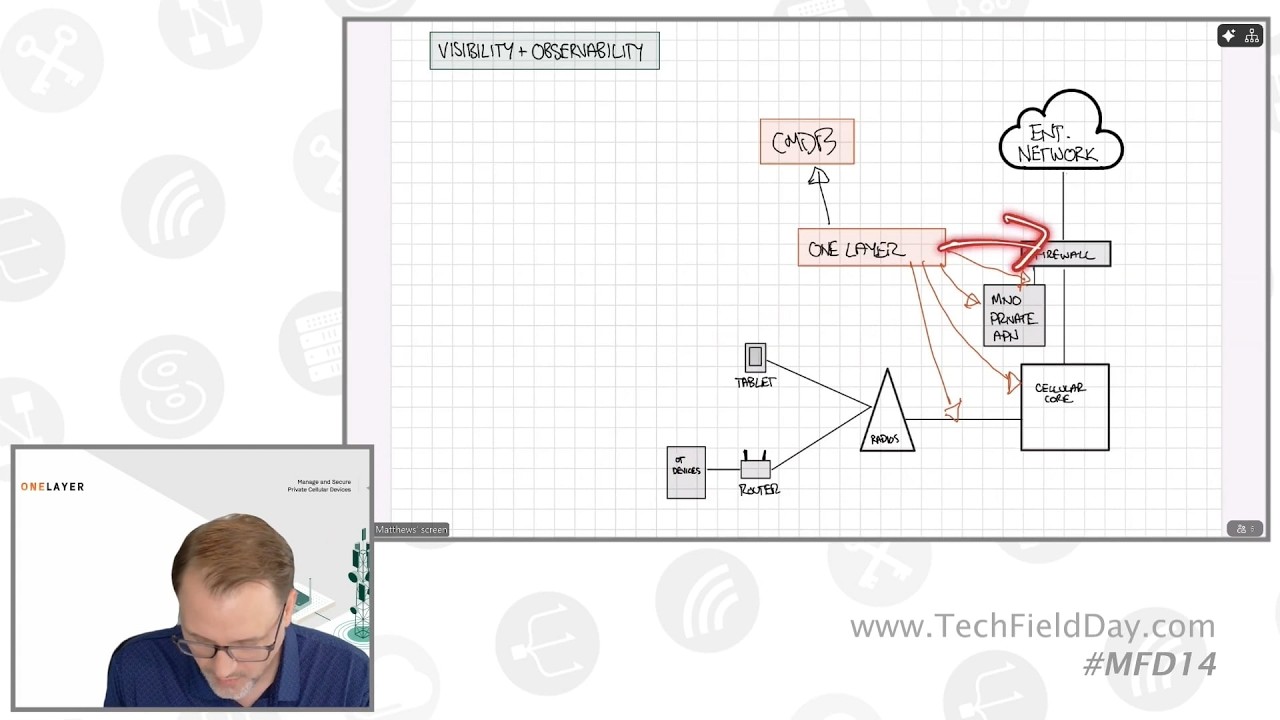
The OneLayer Visibility and Observability presentation focuses on how the company's platform integrates into existing private cellular architectures to provide deep device awareness. OneLayer utilizes an on-prem component to connect with mobile network operators (MNOs) and private cellular cores via direct API integrations. This allows the platform to ingest subscriber IDs, SIM card identifiers, and hardware IDs like the International Mobile Equipment Identity (IMEI). By capturing information on signal strength, attachment events, and movement between cells, OneLayer maps cellular-specific data to traditional IP addresses, effectively turning the black box of a cellular core into a transparent and manageable part of the enterprise network.
A key differentiator for OneLayer is its advanced fingerprinting capability, which goes beyond standard database lookups. While a basic IMEI lookup often only identifies the radio manufacturer, OneLayer leverages signaling data and direct partnerships with CPE vendors like Digi and Cradlepoint to identify the exact device model. Crucially, the platform overcomes the inherent visibility barrier of cellular routers by using protocols such as SNMP, NetConf, and SSH to see and fingerprint non-cellular equipment hidden behind them. This granular visibility is then shared with existing enterprise administrative and security tools, such as ServiceNow for CMDB enrichment or firewalls and NACs for unified policy enforcement across both cellular and traditional IT environments.
During the session, the speakers addressed security concerns regarding IMEI spoofing, a primary threat vector in private LTE and 5G networks. While SIM cards can be locked to specific IMEIs, sophisticated attackers can still spoof these identifiers to gain unauthorized access. OneLayer mitigates this risk by analyzing signaling and control traffic to validate that a device's radio capabilities match its reported identity; for instance, if a device claiming to be a smart meter exhibits the radio behavior of a laptop, the system flags the anomaly. This multi-layered approach ensures that organizations can move beyond a mere confidence build to a high-assurance security model, allowing them to group devices and apply consistent access policies based on verified identities.
Presented by Steve Banda, Director of Product Marketing, and Ryan Matthews, Sales Engineer. Recorded live at Mobility Field Day 14 in San Jose, CA on May 7, 2026. Watch the entire presentation at techfieldday.com/appearance/onelayer-presents-at-mobility-field-day-14 or visit TechFieldDay.com/event/mfd14 or OneLayer.com for more information.
The OneLayer Visibility and Observability presentation focuses on how the company's platform integrates into existing private cellular architectures to provide deep device awareness. OneLayer utilizes an on-prem component to connect with mobile network operators (MNOs) and private cellular cores via direct API integrations. This allows the platform to ingest subscriber IDs, SIM card identifiers, and hardware IDs like the International Mobile Equipment Identity (IMEI). By capturing information on signal strength, attachment events, and movement between cells, OneLayer maps cellular-specific data to traditional IP addresses, effectively turning the black box of a cellular core into a transparent and manageable part of the enterprise network.
A key differentiator for OneLayer is its advanced fingerprinting capability, which goes beyond standard database lookups. While a basic IMEI lookup often only identifies the radio manufacturer, OneLayer leverages signaling data and direct partnerships with CPE vendors like Digi and Cradlepoint to identify the exact device model. Crucially, the platform overcomes the inherent visibility barrier of cellular routers by using protocols such as SNMP, NetConf, and SSH to see and fingerprint non-cellular equipment hidden behind them. This granular visibility is then shared with existing enterprise administrative and security tools, such as ServiceNow for CMDB enrichment or firewalls and NACs for unified policy enforcement across both cellular and traditional IT environments.
During the session, the speakers addressed security concerns regarding IMEI spoofing, a primary threat vector in private LTE and 5G networks. While SIM cards can be locked to specific IMEIs, sophisticated attackers can still spoof these identifiers to gain unauthorized access. OneLayer mitigates this risk by analyzing signaling and control traffic to validate that a device's radio capabilities match its reported identity; for instance, if a device claiming to be a smart meter exhibits the radio behavior of a laptop, the system flags the anomaly. This multi-layered approach ensures that organizations can move beyond a mere confidence build to a high-assurance security model, allowing them to group devices and apply consistent access policies based on verified identities.
Presented by Steve Banda, Director of Product Marketing, and Ryan Matthews, Sales Engineer. Recorded live at Mobility Field Day 14 in San Jose, CA on May 7, 2026. Watch the entire presentation at techfieldday.com/appearance/onelayer-presents-at-mobility-field-day-14 or visit TechFieldDay.com/event/mfd14 or OneLayer.com for more information.