Uploaded August 2026 | Updated November 2026, 2 days ago
This talk was recorded at NDC Copenhagen in Copenhagen, Denmark. #ndccopenhagen #ndcconferences #developer #softwaredeveloper
Attend the next NDC conference near you:
ndcconferences.com
ndccopenhagen.com
Subscribe to our YouTube channel and learn every day:
/ @NDC
Follow our Social Media!
facebook.com/ndcconferences
twitter.com/NDC_Conferences
instagram.com/ndc_conferences
#security #ai #devops
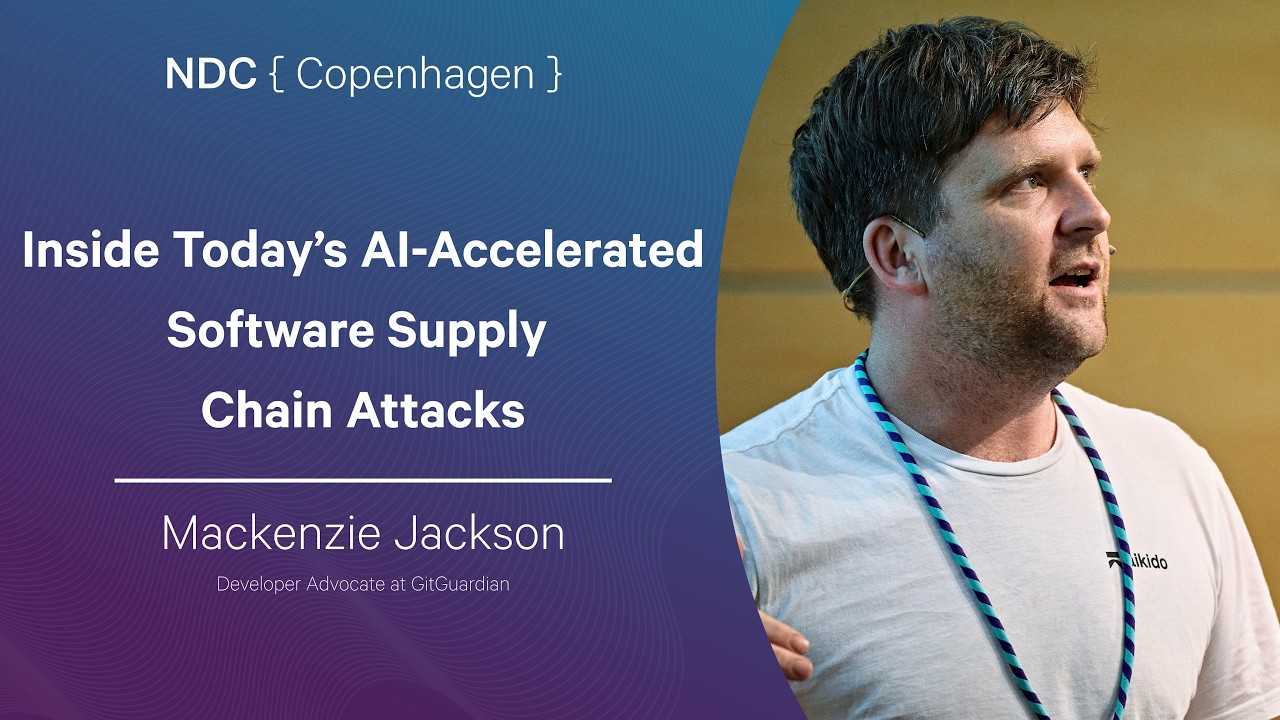
In 2026, software supply chain attacks grew dramatically in scale and sophistication.
The Aikido Security research team was the first to uncover several of the most impactful incidents, including the Shai-Hulud self-propagating worm, the largest mass compromise of npm packages involving debug and chalk, and the backdooring of an official XRP cryptocurrency SDK. Together, these discoveries revealed that supply chain attacks are no longer isolated events, but carefully engineered campaigns designed to scale.
Attackers are also increasingly leveraging artificial intelligence as part of this evolution. We’ve seen early signs of this in real-world incidents, including prompt injection attacks delivered through CI/CD pipelines, impacting multiple Fortune 500 companies. including Google.
This talk breaks down why attackers increasingly target the software supply chain and what makes it such a powerful leverage point. We’ll examine the anatomy of modern supply chain attacks, including how attackers gain initial access to trusted packages, workflows, and extension ecosystems; how they move laterally by harvesting tokens and abusing CI/CD systems; and what their ultimate objectives are. We’ll also explore why certain ecosystems, such as package registries and IDE extensions, are especially vulnerable, why detecting malicious behavior remains so difficult, and what practical steps organizations and the broader community can take to raise the bar against these threats.
This talk was recorded at NDC Copenhagen in Copenhagen, Denmark. #ndccopenhagen #ndcconferences #developer #softwaredeveloper
Attend the next NDC conference near you:
ndcconferences.com
ndccopenhagen.com
Subscribe to our YouTube channel and learn every day:
/ @NDC
Follow our Social Media!
facebook.com/ndcconferences
twitter.com/NDC_Conferences
instagram.com/ndc_conferences
#security #ai #devops
In 2026, software supply chain attacks grew dramatically in scale and sophistication.
The Aikido Security research team was the first to uncover several of the most impactful incidents, including the Shai-Hulud self-propagating worm, the largest mass compromise of npm packages involving debug and chalk, and the backdooring of an official XRP cryptocurrency SDK. Together, these discoveries revealed that supply chain attacks are no longer isolated events, but carefully engineered campaigns designed to scale.
Attackers are also increasingly leveraging artificial intelligence as part of this evolution. We’ve seen early signs of this in real-world incidents, including prompt injection attacks delivered through CI/CD pipelines, impacting multiple Fortune 500 companies. including Google.
This talk breaks down why attackers increasingly target the software supply chain and what makes it such a powerful leverage point. We’ll examine the anatomy of modern supply chain attacks, including how attackers gain initial access to trusted packages, workflows, and extension ecosystems; how they move laterally by harvesting tokens and abusing CI/CD systems; and what their ultimate objectives are. We’ll also explore why certain ecosystems, such as package registries and IDE extensions, are especially vulnerable, why detecting malicious behavior remains so difficult, and what practical steps organizations and the broader community can take to raise the bar against these threats.