Uploaded May 2026 | Updated September 2026, 2 weeks ago
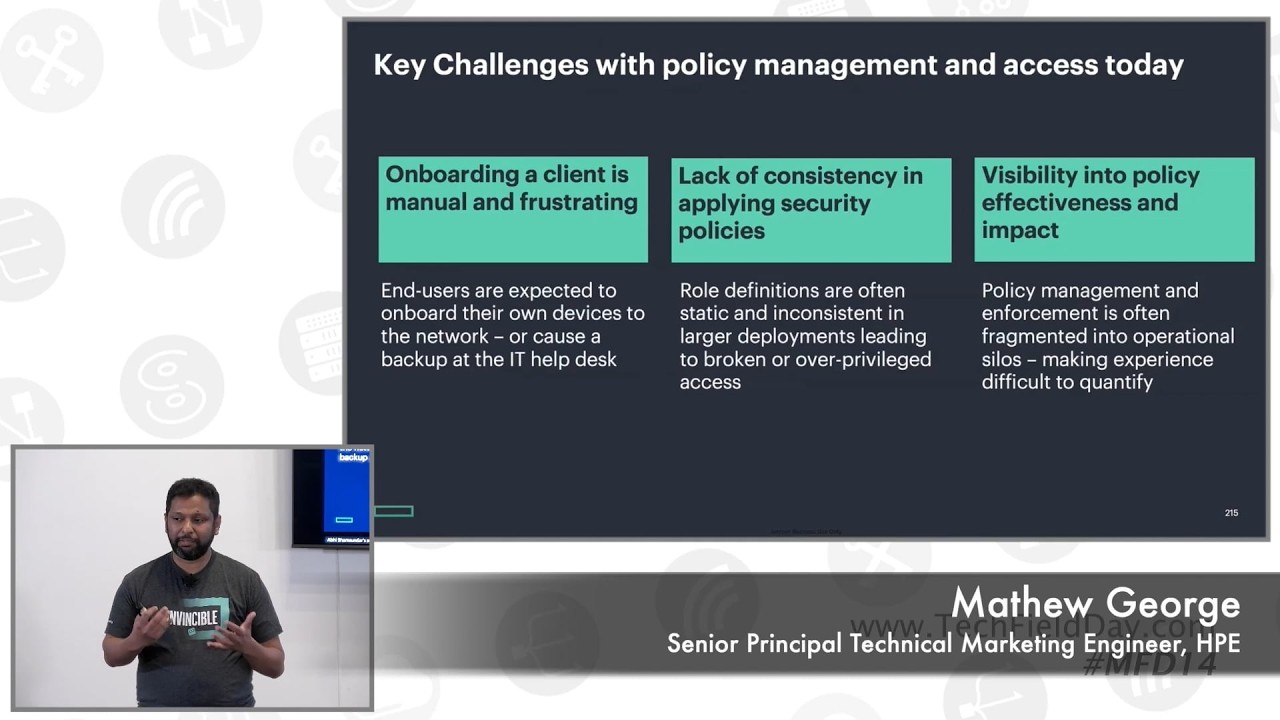
In this presentation at Mobility Field Day 14, Mathew George outlines the security enhancements within HPE Aruba Central designed to simplify the transition to a zero-trust architecture. George identifies common barriers to zero-trust adoption, such as fragmented onboarding workflows, inconsistent policies across different network locations, and a lack of visibility into policy enforcement. To address these, Aruba Central now includes Central NAC, an enterprise-grade, cloud-native network access control solution. This platform supports modern authentication methods like EAP-TLS and MPSK, and it integrates directly with identity sources like Okta and Microsoft Entra ID (formerly Azure AD), as well as MDM solutions such as Intune, JAMF, and Workspace ONE for automated, silent device provisioning.
A significant portion of the demonstration focuses on Client Insights, which uses AI and machine learning to fingerprint devices based on telemetry, DHCP signatures, and traffic flows. This capability allows the network to automatically detect and tag IoT devices, which are often security vulnerabilities. George demonstrates a zero-trust in action scenario where an Arlo security camera, once tagged as compromised via a manual security alert, is immediately forced to re-authenticate and reassigned to a restricted-access role within two minutes. This granular visibility extends to the Security Planet dashboard, which provides a live session view of the data path, allowing administrators to troubleshoot blocked traffic by seeing exactly which ACL or policy is impacting a specific user.
The presentation also highlights the shift toward unified, intent-based policy management. Instead of writing complex, device-specific ACLs, administrators can define a single policy based on user roles--such as preventing BYOD users from accessing corporate IoT devices--and Central handles the translation and deployment across access points, switches, and gateways. Addressing the future of the portfolio, the speakers confirm that while Central NAC is the primary path for cloud-first customers, HPE remains committed to on-premises offerings for complex, multi-vendor environments. They emphasize that the "New Central" platform is fully available as an on-premises solution, ensuring that organizations with strict data residency or connectivity requirements can still leverage these advanced AI-driven security features.
Presented by Mathew George, Sr. Principal Technical Marketing Engineer. Recorded live at Mobility Field Day 14 in San Jose, CA on May 6, 2026. Watch the entire presentation at techfieldday.com/appearance/hpe-presents-at-mobility-field-day-14 or visit TechFieldDay.com/event/mfd14 or hpe.com/us/en/networking.html for more information.