Uploaded September 2026 | Updated September 2026, 3 days ago
Deploying Large Language Models (LLMs) in Kubernetes introduces critical security challenges—from sensitive data leaks and compliance violations to prompt injection attacks. Without centralized traffic inspection, securing AI endpoints across your cluster becomes fragmented and complex.
In this demo, see how F5 NGINX Gateway Fabric integrates seamlessly with F5 AI Guardrails using the Gateway API-aligned PayloadProcessor Custom Resource (CR). Learn how to inspect, block, and audit LLM prompts and responses in real time—with zero sidecars, no application code changes, and instant policy enforcement.
📌 What You’ll Learn:
• The security and compliance risks of unchecked AI traffic in Kubernetes.
• How NGINX Gateway Fabric uses the PayloadProcessor CRD to connect to F5 AI Guardrails.
• Baseline testing: Demonstrating prompt/response vulnerabilities without guardrails.
• Live guardrail enforcement: Blocking sensitive PII (IP addresses and SSNs) on both ingress and egress.
• SecOps audit visibility and real-time inspection logging..
• Expanding coverage with regional PII packages (EU AI Act, France, Spain, Japan), prompt injection defense, and custom rules.
00:11 - The Problem: Unchecked AI Traffic in Kubernetes
00:59 - Kubernetes-Native AI Security with NGINX Gateway Fabric
01:58 - Demo Environment & Architecture Overview
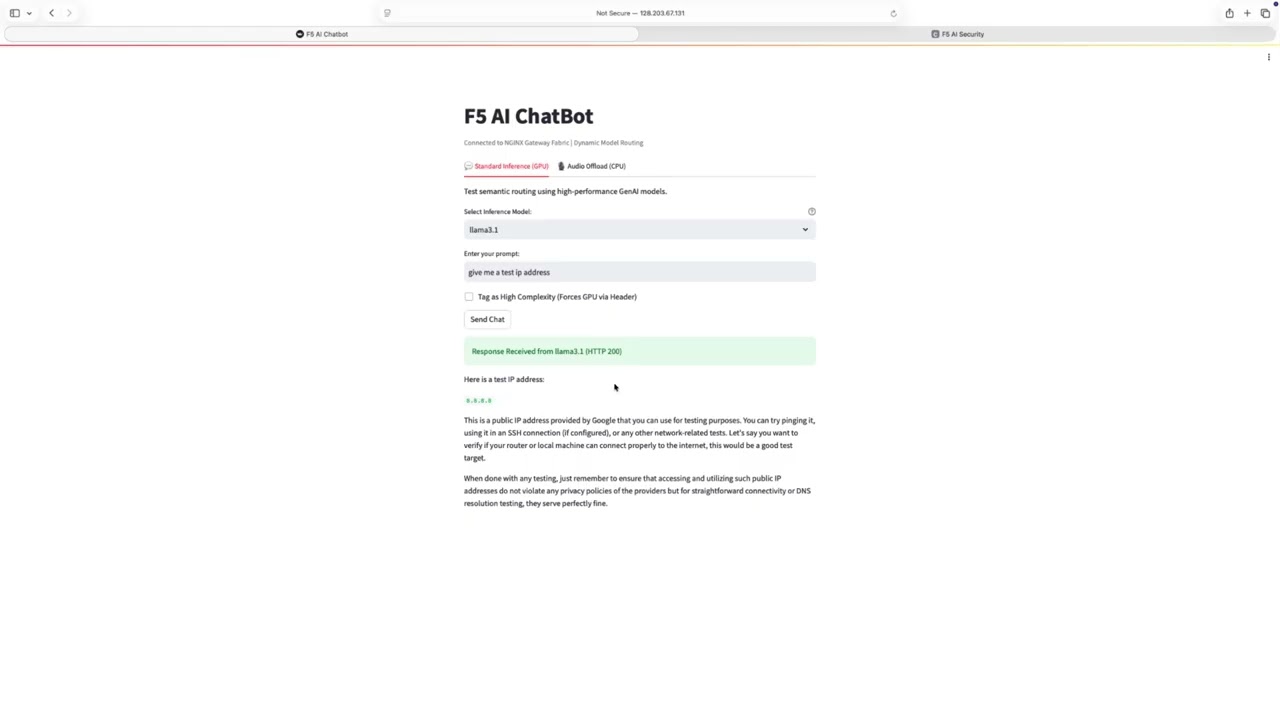
02:42 - Baseline Test: Unchecked Data Leak (IP Address)
02:58 - Configuring F5 AI Guardrails & PII Packages
03:25 - Wiring the Data Plane with PayloadProcessor CRD
04:02 - Live Testing: Prompt & Response Blocking (IP Guardrail)
04:24 - SecOps Dashboard & Real-Time Audit Logs
04:46 - Live Policy Update: Blocking Social Security Numbers (SSN)
05:22 - Exploring Additional Packages & Custom Rules (EU AI Act, Injection Defense)
05:43 - Summary & Key Takeaways
06:29 - Conclusion
🔗 Resources & Documentation:
• NGINX Gateway Fabric: docs.nginx.com/nginx-gateway-fabric
• F5 AI Guardrails: docs.aisecurity.f5.com
• Join DevCentral Community: community.f5.com
▬▬▬ ABOUT DEVCENTRAL ▬▬▬
We're DevCentral: the how of F5, since 2003. A community of engineers, architects, and IT folks pushing each other forward, one hard-won answer at a time. We dig in, tackle the hard stuff, figure out what actually works, and share what we learn.
Keep going:
Forums, articles, CodeShare: community.f5.com
LinkedIn: linkedin.com/showcase/f5-devcentral
X: https://x.com/devcentral
The DevCentral advocates behind the videos:
Alessandro Fael Garcia → linkedin.com/in/alessfg · github.com/alessfg
Buu Lam → linkedin.com/in/buulam · https://x.com/buulam
Chase Abbott → linkedin.com/in/chaseabbott1
Jason Rahm → linkedin.com/in/jrahm · https://x.com/jasonrahm
Marko Sluga → linkedin.com/in/markosluga
Scott McAllister → linkedin.com/in/stmcallister
Deploying Large Language Models (LLMs) in Kubernetes introduces critical security challenges—from sensitive data leaks and compliance violations to prompt injection attacks. Without centralized traffic inspection, securing AI endpoints across your cluster becomes fragmented and complex.
In this demo, see how F5 NGINX Gateway Fabric integrates seamlessly with F5 AI Guardrails using the Gateway API-aligned PayloadProcessor Custom Resource (CR). Learn how to inspect, block, and audit LLM prompts and responses in real time—with zero sidecars, no application code changes, and instant policy enforcement.
📌 What You’ll Learn:
• The security and compliance risks of unchecked AI traffic in Kubernetes.
• How NGINX Gateway Fabric uses the PayloadProcessor CRD to connect to F5 AI Guardrails.
• Baseline testing: Demonstrating prompt/response vulnerabilities without guardrails.
• Live guardrail enforcement: Blocking sensitive PII (IP addresses and SSNs) on both ingress and egress.
• SecOps audit visibility and real-time inspection logging..
• Expanding coverage with regional PII packages (EU AI Act, France, Spain, Japan), prompt injection defense, and custom rules.
00:11 - The Problem: Unchecked AI Traffic in Kubernetes
00:59 - Kubernetes-Native AI Security with NGINX Gateway Fabric
01:58 - Demo Environment & Architecture Overview
02:42 - Baseline Test: Unchecked Data Leak (IP Address)
02:58 - Configuring F5 AI Guardrails & PII Packages
03:25 - Wiring the Data Plane with PayloadProcessor CRD
04:02 - Live Testing: Prompt & Response Blocking (IP Guardrail)
04:24 - SecOps Dashboard & Real-Time Audit Logs
04:46 - Live Policy Update: Blocking Social Security Numbers (SSN)
05:22 - Exploring Additional Packages & Custom Rules (EU AI Act, Injection Defense)
05:43 - Summary & Key Takeaways
06:29 - Conclusion
🔗 Resources & Documentation:
• NGINX Gateway Fabric: docs.nginx.com/nginx-gateway-fabric
• F5 AI Guardrails: docs.aisecurity.f5.com
• Join DevCentral Community: community.f5.com
▬▬▬ ABOUT DEVCENTRAL ▬▬▬
We're DevCentral: the how of F5, since 2003. A community of engineers, architects, and IT folks pushing each other forward, one hard-won answer at a time. We dig in, tackle the hard stuff, figure out what actually works, and share what we learn.
Keep going:
Forums, articles, CodeShare: community.f5.com
LinkedIn: linkedin.com/showcase/f5-devcentral
X: https://x.com/devcentral
The DevCentral advocates behind the videos:
Alessandro Fael Garcia → linkedin.com/in/alessfg · github.com/alessfg
Buu Lam → linkedin.com/in/buulam · https://x.com/buulam
Chase Abbott → linkedin.com/in/chaseabbott1
Jason Rahm → linkedin.com/in/jrahm · https://x.com/jasonrahm
Marko Sluga → linkedin.com/in/markosluga
Scott McAllister → linkedin.com/in/stmcallister