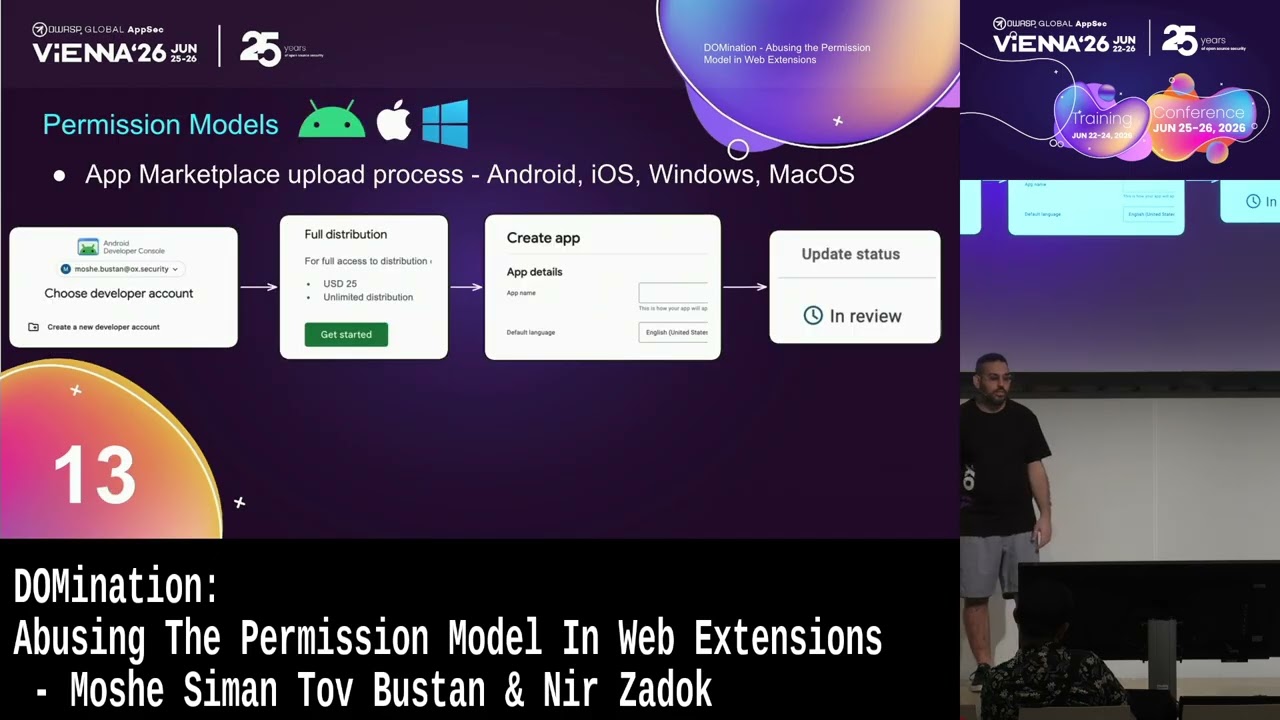
DOMination: Abusing The Permission Model In Web Extensions - Moshe Siman Tov Bustan & Nir Zadok @OWASPGLOBAL
DOMination: Abusing The Permission Model In Web Extensions - Moshe Siman Tov Bustan & Nir Zadok  @OWASPGLOBAL
Uploaded October 2026 | Updated November 2026, 2 days ago
-

Managed by the OWASP® Foundation
owasp.org
DOMination: Abusing The Permission Model In Web Extensions - Moshe Siman Tov Bustan & Nir ZadokJean Ramirez260924 OWASP Gregoire ValletOWASP AI Testing Guide In Practice: Securing LLM Applications - Matteo Meucci & Marco MoranaBenchmarking Scanner Blind Spots: How Runtime Context Uncovers Hidden VulnsKeep It Between Us: Manipulating Humans For Better AppSec (Ethically) - Nariman Aga-TagiyevAppSec Days PT - Injection Attacks Through the Ages  From Turing Machines to Prompt InjectionCTFs As A Community Of Practice Content Machine - Marco Macala, Florian Schier & Christian BuchingerYour RPA is Mine: Complete Takeover of RPA EcosystemsNoise vs. Signal: The Central Paradox of LLMs in Threat Modeling track 2BREAKOWASP DefectDojo
OWASP Foundation |

DOMination: Abusing The Permission Model In Web Extensions - Moshe Siman Tov Bustan & Nir Zadok

SHARE TO X SHARE TO REDDIT SHARE TO FACEBOOK WALLPAPER