Uploaded November 2026 | Updated November 2026, 3 days ago
What if your recon tool could understand "find leaked credentials for this company on the dark web, cross-reference with their exposed infrastructure, and show me the attack path" — and then actually do it, autonomously, with zero manual commands? CyberKB is a 214,000-line open platform that puts an AI copilot (Keke) in command of 131 offensive tools spanning reconnaissance, dark web OSINT, Shodan intelligence, breach databases, and a full Kali Linux shell — all orchestrated through natural language conversation. The Dark Web Intelligence Pipeline (DarkMonitor): CyberKB's DarkMonitor module queries .onion search engines concurrently through Tor, uses LLM-powered query refinement to generate optimal dark web search terms, applies AI relevance filtering to surface the most critical results.
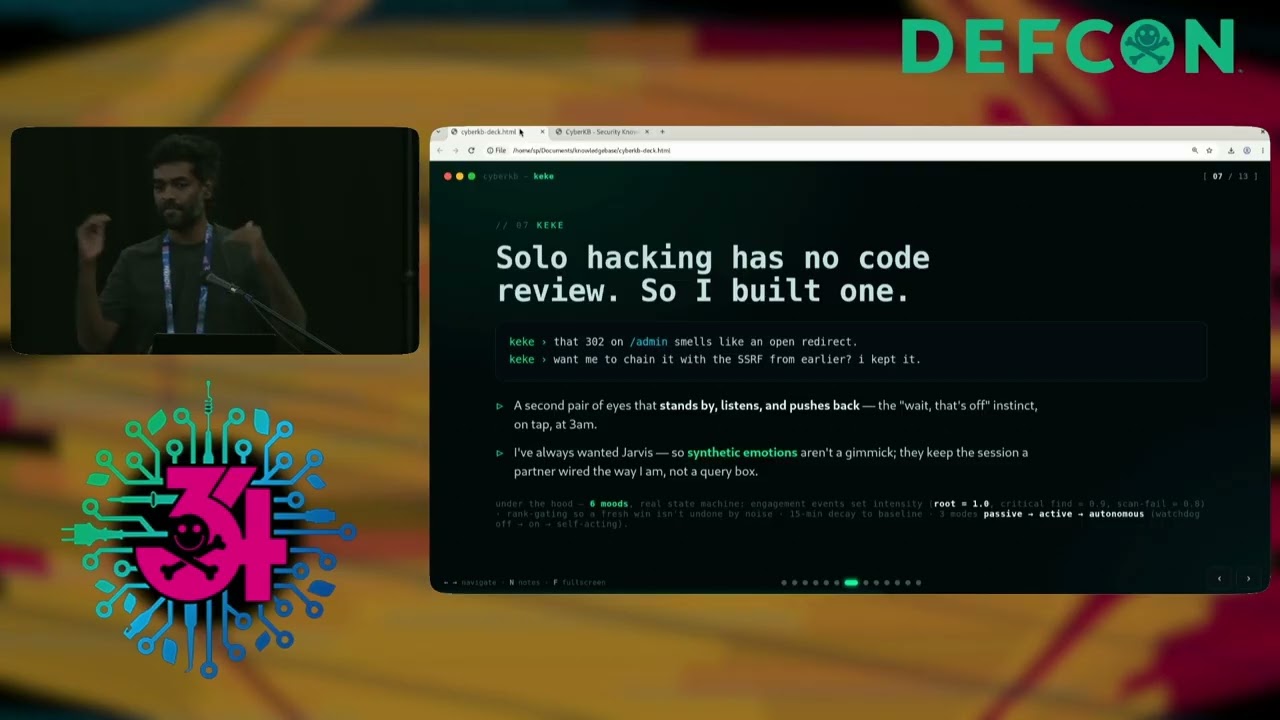
The AI Copilot (Keke): Keke isn't a wrapper around ChatGPT. It's a function-calling agent with direct execution access to: a privileged Kali container (nmap, curl, nikto, sqlmap, gobuster, hydra — the full toolkit), 16 dark web search engines via Tor, breach and paste database aggregators, a RAG-powered knowledge base with semantic search over ingested recon data, Shodan lookups and CVE correlation, MITRE ATT&CK technique mapping, attack graph generation and path prioritization, and engagement management (targets, credentials, findings, reports).
Scale Proof — 2,250-Domain Assessment: We demonstrate CyberKB against a real-world external attack surface assessment: 2,250 domains belonging to a single organization, producing 11,968 unique IPs, 8,494 hostnames, 2,444 CVEs, 80,238 open ports, and a knowledge graph of 6,390 nodes with 51,990 infrastructure relationship edges. The entire dataset was parsed, correlated, and ingested into the AI-queryable knowledge base in 25 seconds. Keke can now answer questions like "which x domains share infrastructure with known-vulnerable IPs" by searching the graph, not by re-scanning.
What This Means for Defenders: Every autonomous recon step Keke performs leaves detectable artifacts. We discuss what blue teams should monitor: DNS burst patterns from multi-engine enumeration, Tor exit node correlation with target infrastructure, behavioral signatures of AI-driven sequential probing, and how to distinguish human recon from autonomous agent recon. The same platform that empowers red teams reveals the detection surface that defenders can leverage.
What if your recon tool could understand "find leaked credentials for this company on the dark web, cross-reference with their exposed infrastructure, and show me the attack path" — and then actually do it, autonomously, with zero manual commands? CyberKB is a 214,000-line open platform that puts an AI copilot (Keke) in command of 131 offensive tools spanning reconnaissance, dark web OSINT, Shodan intelligence, breach databases, and a full Kali Linux shell — all orchestrated through natural language conversation. The Dark Web Intelligence Pipeline (DarkMonitor): CyberKB's DarkMonitor module queries .onion search engines concurrently through Tor, uses LLM-powered query refinement to generate optimal dark web search terms, applies AI relevance filtering to surface the most critical results.
The AI Copilot (Keke): Keke isn't a wrapper around ChatGPT. It's a function-calling agent with direct execution access to: a privileged Kali container (nmap, curl, nikto, sqlmap, gobuster, hydra — the full toolkit), 16 dark web search engines via Tor, breach and paste database aggregators, a RAG-powered knowledge base with semantic search over ingested recon data, Shodan lookups and CVE correlation, MITRE ATT&CK technique mapping, attack graph generation and path prioritization, and engagement management (targets, credentials, findings, reports).
Scale Proof — 2,250-Domain Assessment: We demonstrate CyberKB against a real-world external attack surface assessment: 2,250 domains belonging to a single organization, producing 11,968 unique IPs, 8,494 hostnames, 2,444 CVEs, 80,238 open ports, and a knowledge graph of 6,390 nodes with 51,990 infrastructure relationship edges. The entire dataset was parsed, correlated, and ingested into the AI-queryable knowledge base in 25 seconds. Keke can now answer questions like "which x domains share infrastructure with known-vulnerable IPs" by searching the graph, not by re-scanning.
What This Means for Defenders: Every autonomous recon step Keke performs leaves detectable artifacts. We discuss what blue teams should monitor: DNS burst patterns from multi-engine enumeration, Tor exit node correlation with target infrastructure, behavioral signatures of AI-driven sequential probing, and how to distinguish human recon from autonomous agent recon. The same platform that empowers red teams reveals the detection surface that defenders can leverage.