Uploaded November 2026 | Updated November 2026, 2 days ago
Many people are aware of the quantum threat to cryptography, but how extensive is this issue? We analyzed 1,000* high-profile open-source repositories, including OpenVPN, Curl, and Bitcoin, and found that cryptographic risk is pervasive and hidden. 94% of repositories contain at least one cryptographic issue that would become exploitable in a post-quantum setting*, while 92% contain an issue that is already considered insecure by today’s standards*. The median repository contains 185 quantum-relevant weaknesses of moderate severity or higher, nearly double the classical median of 95*, indicating that there is substantial and underrecognized quantum exposure. Notably, thousands of findings are what we call “PQ-invisible;” they appear secure under classical assumptions but would become vulnerable with sufficiently powerful quantum capabilities*, revealing a critical blind spot in current security practices.
These results highlight a gap between real-world cryptography and post-quantum readiness at a time when NIST migration timelines are approaching and Q-Day remains unpredictable. Unlike prior talks that focus on surface-level generalities, this talk is grounded in empirical analysis of source code across a large corpus of highly-used repositories.
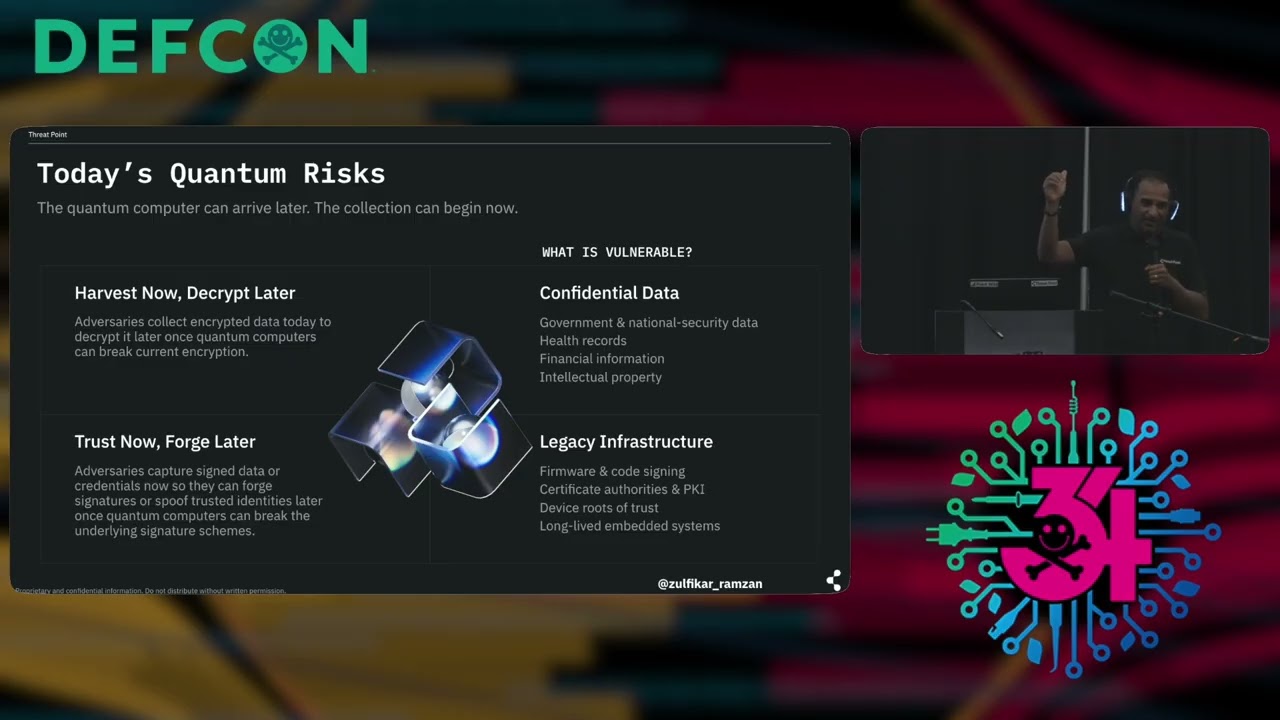
We will give a brief overview of the quantum threat, such as current estimates of quantum progress, NIST standardization, and attacks such as Harvest Now, Decrypt Later (HNDL) and Trust Now, Forge Later (TNFL). We will then present our methodology and results, including detailed breakdowns of cryptographic types, algorithms, and security postures across public-key cryptography, symmetric encryption, hashing, password hashing, TLS, and MACs.
Whether you’re new to the quantum threat to cryptography or all-too-familiar with it, we hope to provide a clearer understanding of the current state of cryptography and the post-quantum migration.
Many people are aware of the quantum threat to cryptography, but how extensive is this issue? We analyzed 1,000* high-profile open-source repositories, including OpenVPN, Curl, and Bitcoin, and found that cryptographic risk is pervasive and hidden. 94% of repositories contain at least one cryptographic issue that would become exploitable in a post-quantum setting*, while 92% contain an issue that is already considered insecure by today’s standards*. The median repository contains 185 quantum-relevant weaknesses of moderate severity or higher, nearly double the classical median of 95*, indicating that there is substantial and underrecognized quantum exposure. Notably, thousands of findings are what we call “PQ-invisible;” they appear secure under classical assumptions but would become vulnerable with sufficiently powerful quantum capabilities*, revealing a critical blind spot in current security practices.
These results highlight a gap between real-world cryptography and post-quantum readiness at a time when NIST migration timelines are approaching and Q-Day remains unpredictable. Unlike prior talks that focus on surface-level generalities, this talk is grounded in empirical analysis of source code across a large corpus of highly-used repositories.
We will give a brief overview of the quantum threat, such as current estimates of quantum progress, NIST standardization, and attacks such as Harvest Now, Decrypt Later (HNDL) and Trust Now, Forge Later (TNFL). We will then present our methodology and results, including detailed breakdowns of cryptographic types, algorithms, and security postures across public-key cryptography, symmetric encryption, hashing, password hashing, TLS, and MACs.
Whether you’re new to the quantum threat to cryptography or all-too-familiar with it, we hope to provide a clearer understanding of the current state of cryptography and the post-quantum migration.