Uploaded December 2019 | Updated September 2026, 2 days ago
In theory, brute force key recovery attacks against modern ciphers like AES should be impractical with the current state of computer hardware. It's often said that recovering an AES key should take longer than the remainder of the life of the sun. However, this assumes that keys are chosen properly, and that there is no way to determine whether a key is the correct one after a candidate key is used to decrypt a captured ciphertext.
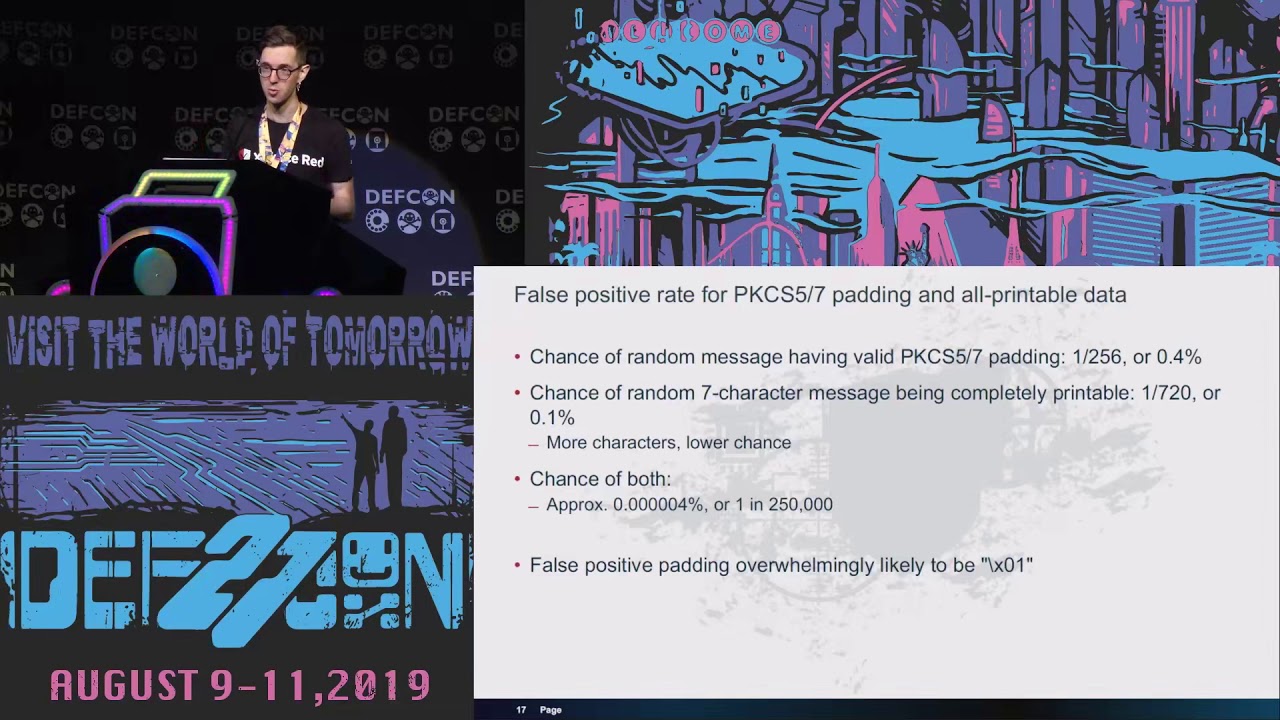
In practice, these conditions do not always hold. In much the same way that hash functions are impossible to reverse but hash cracking is still a practical attack, in the real world it is often possible to perform practical key search attacks. In this talk, we will discuss the common mistakes and common conditions that allow for practical brute force recovery of keys for modern block ciphers such as AES. We will also discuss optimizations to speed up key search efforts, and present our FOSS tool, which implements our approach.
In theory, brute force key recovery attacks against modern ciphers like AES should be impractical with the current state of computer hardware. It's often said that recovering an AES key should take longer than the remainder of the life of the sun. However, this assumes that keys are chosen properly, and that there is no way to determine whether a key is the correct one after a candidate key is used to decrypt a captured ciphertext.
In practice, these conditions do not always hold. In much the same way that hash functions are impossible to reverse but hash cracking is still a practical attack, in the real world it is often possible to perform practical key search attacks. In this talk, we will discuss the common mistakes and common conditions that allow for practical brute force recovery of keys for modern block ciphers such as AES. We will also discuss optimizations to speed up key search efforts, and present our FOSS tool, which implements our approach.