Uploaded December 2019 | Updated September 2026, 18 minutes ago
Nearby sharing apps are very convenient and fast when you want to transfer files and have been pre-installed on billions of devices. However, we found that most of them will also open a door for attackers to steal your files and even more.
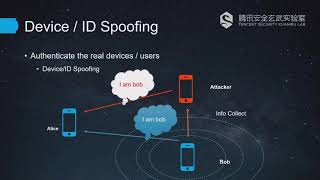
First, we did a comprehensive research about all top mobile vendors' pre-installed nearby sharing apps by reverse engineering. Many serious vulnerabilities are found on most of them and reported to vendors. Algorithm and design flaws in these apps can lead to file leaking and tampering, privacy leaks, arbitrary file downloads and even remote code execution. We will present all the related vulnerabilities' details and exploit techniques. Next, we conducted the same research on lots of third-party file sharing apps and found that they are even worse about security and are used by surprising more than 1 billion users. Files transferred between them are nearly naked when our MITM attack devices are nearby. Finally, we will summarize all the attack vectors and two common attack models. We will also present the attack demos and related tools.
Besides, we will present our practical mitigations. Currently, we are working with most of the top vendors to mitigate these vulnerabilities. Through this talk, we want to notify users and mobile vendors to pay more attention to this serious situation and fix it better and sooner.
Nearby sharing apps are very convenient and fast when you want to transfer files and have been pre-installed on billions of devices. However, we found that most of them will also open a door for attackers to steal your files and even more.
First, we did a comprehensive research about all top mobile vendors' pre-installed nearby sharing apps by reverse engineering. Many serious vulnerabilities are found on most of them and reported to vendors. Algorithm and design flaws in these apps can lead to file leaking and tampering, privacy leaks, arbitrary file downloads and even remote code execution. We will present all the related vulnerabilities' details and exploit techniques. Next, we conducted the same research on lots of third-party file sharing apps and found that they are even worse about security and are used by surprising more than 1 billion users. Files transferred between them are nearly naked when our MITM attack devices are nearby. Finally, we will summarize all the attack vectors and two common attack models. We will also present the attack demos and related tools.
Besides, we will present our practical mitigations. Currently, we are working with most of the top vendors to mitigate these vulnerabilities. Through this talk, we want to notify users and mobile vendors to pay more attention to this serious situation and fix it better and sooner.