Uploaded February 2023 | Updated September 2026, 2 weeks ago
A few videos ago, we modified our README to use a relative link instead of an absolute link to another file in the repo.
In this case we go the other direction and double-down on using an absolute link. There is a time for every purpose under heaven, and in this case we want to gather stones together.
The gemspec for the project and the entry on RubyGems explicitly link to the master branch version of the CHANGELOG. Because the CHANGELOG could exist in various states on different branches, it can introduce ambiguity as to which is the source of truth and become a tedious administrative chore to maintain.
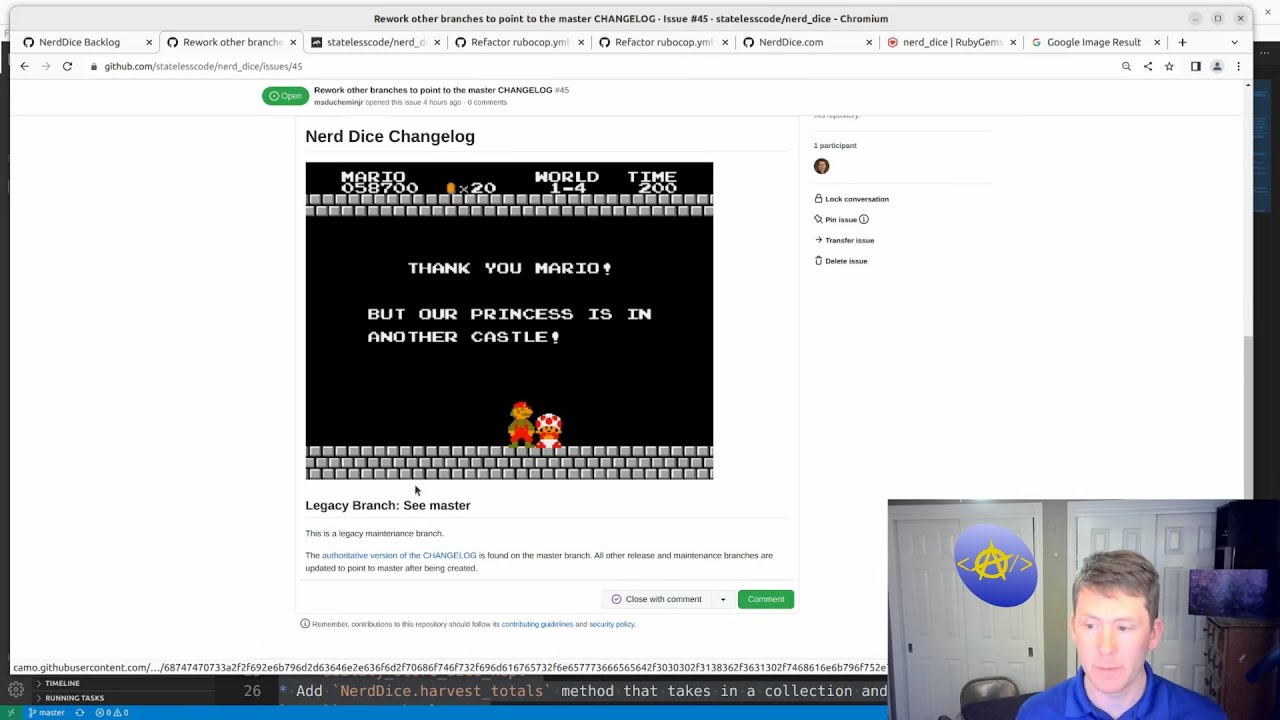
In order to have a clear authority as to which CHANGELOG is the authority, we update the CHANGELOG files on our legacy branches to explicitly point to the master branch. We even add in an image that pays homage to the iconic scenes in Super Mario Brothers where you complete a castle level and are greeted by a citizen of the Mushroom Kingdom who informs you that the princess is in another castle.
We use the GitHub Markdown editor to draft our new pointer to the master CHANGELOG, and then check out and paste in the contents to each legacy branch.
After pushing to the legacy branches and verifying that the intended changes are in place, I hem and haw about whether to update the master branch version now or not. Ultimately, we defer that CHANGELOG update for a couple more videos until we start determining which changes to to each branch.
This video covers:
00:00:12 Introduction
00:01:52 Demonstrate variance in CHANGELOG files across the various stable branches
00:02:26 Show how the gemspec and RubyGems refer explicitly to the master branch CHANGELOG
00:03:45 Draft a Markdown replacement for the CHANGELOG on legacy branches that points to the master CHANGELOG
00:05:51 Make change on 0-1-x branch
00:08:10 Make change on 0-2-x branch
00:10:02 Make change on 0-3-x branch
00:11:15 Make change on 0-4-x branch
00:12:25 Go to GitHub Actions and ensure all the builds passed.
00:12:50 Validate changes on all the legacy branches
00:13:35 Indecision about whether to update the master CHANGELOG now or not, ultimately decide to defer it to another video
00:15:09 Close issue and update backlog
#ruby #rubygems #codecast #screencast #NerdDice #DnD #roleplaying #softwaredevelopment #github #opensource #dice #documentation #changelog #mario #supermariobrothers #ourprincessisinanothercastle
See other related StatelessCode videos:
- Create a RubyGem 90: Fix README to Use Relative Links Instead of Absolute Links youtu.be/fHirL25vP-8
This video is CC0 - No rights reserved. (YouTube doesn't allow this option when publishing.) All code is released under the UNLICENSE. Stateless Code denies the concept of "intellectual property". Copying is not stealing.
A few videos ago, we modified our README to use a relative link instead of an absolute link to another file in the repo.
In this case we go the other direction and double-down on using an absolute link. There is a time for every purpose under heaven, and in this case we want to gather stones together.
The gemspec for the project and the entry on RubyGems explicitly link to the master branch version of the CHANGELOG. Because the CHANGELOG could exist in various states on different branches, it can introduce ambiguity as to which is the source of truth and become a tedious administrative chore to maintain.
In order to have a clear authority as to which CHANGELOG is the authority, we update the CHANGELOG files on our legacy branches to explicitly point to the master branch. We even add in an image that pays homage to the iconic scenes in Super Mario Brothers where you complete a castle level and are greeted by a citizen of the Mushroom Kingdom who informs you that the princess is in another castle.
We use the GitHub Markdown editor to draft our new pointer to the master CHANGELOG, and then check out and paste in the contents to each legacy branch.
After pushing to the legacy branches and verifying that the intended changes are in place, I hem and haw about whether to update the master branch version now or not. Ultimately, we defer that CHANGELOG update for a couple more videos until we start determining which changes to to each branch.
This video covers:
00:00:12 Introduction
00:01:52 Demonstrate variance in CHANGELOG files across the various stable branches
00:02:26 Show how the gemspec and RubyGems refer explicitly to the master branch CHANGELOG
00:03:45 Draft a Markdown replacement for the CHANGELOG on legacy branches that points to the master CHANGELOG
00:05:51 Make change on 0-1-x branch
00:08:10 Make change on 0-2-x branch
00:10:02 Make change on 0-3-x branch
00:11:15 Make change on 0-4-x branch
00:12:25 Go to GitHub Actions and ensure all the builds passed.
00:12:50 Validate changes on all the legacy branches
00:13:35 Indecision about whether to update the master CHANGELOG now or not, ultimately decide to defer it to another video
00:15:09 Close issue and update backlog
#ruby #rubygems #codecast #screencast #NerdDice #DnD #roleplaying #softwaredevelopment #github #opensource #dice #documentation #changelog #mario #supermariobrothers #ourprincessisinanothercastle
See other related StatelessCode videos:
- Create a RubyGem 90: Fix README to Use Relative Links Instead of Absolute Links youtu.be/fHirL25vP-8
This video is CC0 - No rights reserved. (YouTube doesn't allow this option when publishing.) All code is released under the UNLICENSE. Stateless Code denies the concept of "intellectual property". Copying is not stealing.