Uploaded October 2025 | Updated September 2026, 2 weeks ago
Follow SAI Conferences on Linkedin: linkedin.com/company/saiconference
Conference Website: saiconference.com/IntelliSys
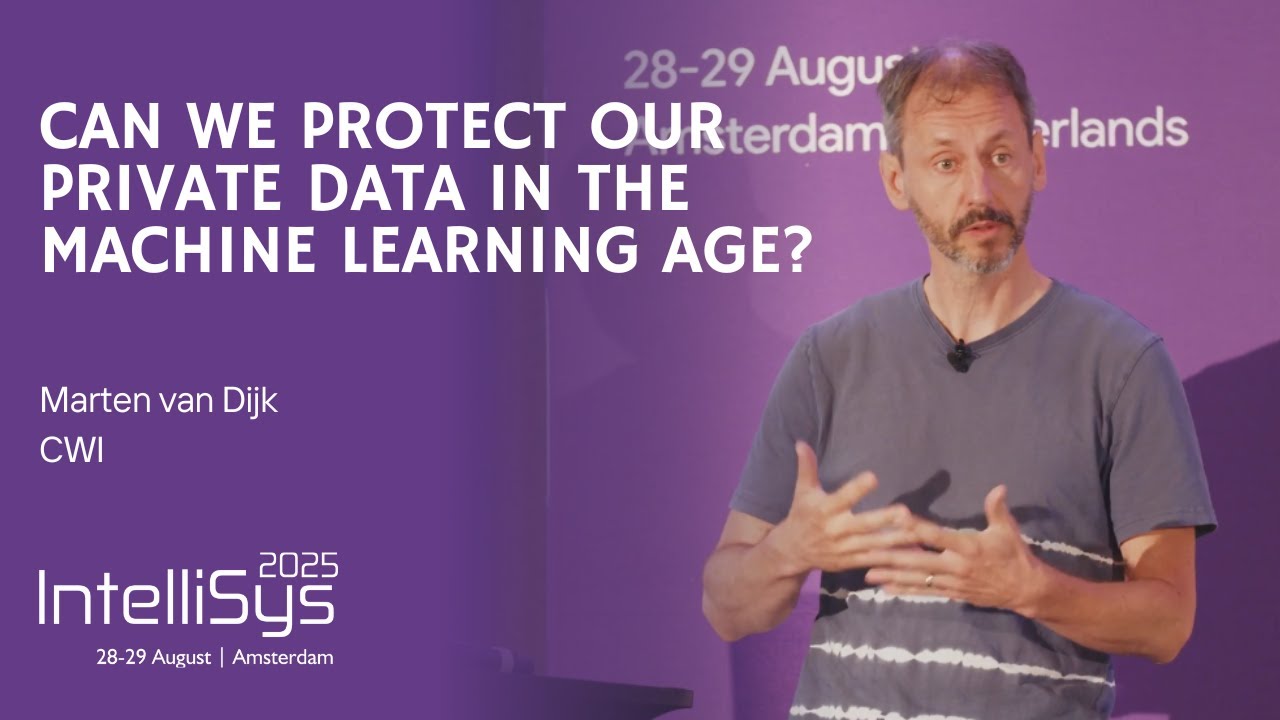
Join Marten van Dijk, IEEE Fellow and founder of the Computer Security group at CWI, the Netherlands, as he explores the challenges and innovations in protecting private data in the era of machine learning. Delivered at the Intelligent Systems Conference (IntelliSys) 2026, this keynote provides a comprehensive overview of secure computation, differential privacy, and the emerging field of privacy-preserving AI.
🔹 About the Speaker:
Marten van Dijk is a globally recognized expert in computer security, with over 20 years of experience spanning academia and industry, including Philips Research, RSA Laboratories, MIT, and Vrije Universiteit Amsterdam. He is the recipient of multiple prestigious awards, including the IEEE CS Edward J. McCluskey Technical Achievement Award 2023 and the A. Richard Newton Technical Impact Award 2015. His pioneering work includes the AEGIS secure processor, Physical Unclonable Functions (PUFs), Fully Homomorphic Encryption over the Integers, and Oblivious RAM, with a current focus on the intersection of security and machine learning.
🔹 Key Topics Covered in This Keynote:
★Evolution of AI and machine learning: from early neural networks to modern foundation models.
★Techniques in confidential computing: Secure Multi-Party Computation (MPC), partial and fully homomorphic encryption, secure processor architectures, and trusted execution environments (TEEs).
★Challenges of differential privacy: balancing privacy guarantees with practical utility in machine learning models.
★Introduction to PAC Privacy and instance-based cryptography as a potential paradigm shift.
★Practical considerations for federated learning and low-resource devices.
★Legal and governance aspects: GDPR, AI Act, and risk-based cybersecurity frameworks.
★Real-world examples of privacy-preserving techniques and limitations in deployment.
This talk provides a unique timeline connecting decades of research in cryptography, secure computation, and privacy with modern AI, highlighting where we stand and what remains to be achieved. Perfect for researchers, practitioners, and enthusiasts in machine learning, AI security, data privacy, federated learning, cryptography, and confidential computing.
🔹 Why Watch This Keynote:
Gain deep insights into the state-of-the-art methods for securing sensitive data, understand the trade-offs between privacy and model utility, and explore how emerging cryptographic techniques could redefine privacy in AI.
Follow SAI Conferences on Linkedin: linkedin.com/company/saiconference
Conference Website: saiconference.com/IntelliSys
Join Marten van Dijk, IEEE Fellow and founder of the Computer Security group at CWI, the Netherlands, as he explores the challenges and innovations in protecting private data in the era of machine learning. Delivered at the Intelligent Systems Conference (IntelliSys) 2026, this keynote provides a comprehensive overview of secure computation, differential privacy, and the emerging field of privacy-preserving AI.
🔹 About the Speaker:
Marten van Dijk is a globally recognized expert in computer security, with over 20 years of experience spanning academia and industry, including Philips Research, RSA Laboratories, MIT, and Vrije Universiteit Amsterdam. He is the recipient of multiple prestigious awards, including the IEEE CS Edward J. McCluskey Technical Achievement Award 2023 and the A. Richard Newton Technical Impact Award 2015. His pioneering work includes the AEGIS secure processor, Physical Unclonable Functions (PUFs), Fully Homomorphic Encryption over the Integers, and Oblivious RAM, with a current focus on the intersection of security and machine learning.
🔹 Key Topics Covered in This Keynote:
★Evolution of AI and machine learning: from early neural networks to modern foundation models.
★Techniques in confidential computing: Secure Multi-Party Computation (MPC), partial and fully homomorphic encryption, secure processor architectures, and trusted execution environments (TEEs).
★Challenges of differential privacy: balancing privacy guarantees with practical utility in machine learning models.
★Introduction to PAC Privacy and instance-based cryptography as a potential paradigm shift.
★Practical considerations for federated learning and low-resource devices.
★Legal and governance aspects: GDPR, AI Act, and risk-based cybersecurity frameworks.
★Real-world examples of privacy-preserving techniques and limitations in deployment.
This talk provides a unique timeline connecting decades of research in cryptography, secure computation, and privacy with modern AI, highlighting where we stand and what remains to be achieved. Perfect for researchers, practitioners, and enthusiasts in machine learning, AI security, data privacy, federated learning, cryptography, and confidential computing.
🔹 Why Watch This Keynote:
Gain deep insights into the state-of-the-art methods for securing sensitive data, understand the trade-offs between privacy and model utility, and explore how emerging cryptographic techniques could redefine privacy in AI.