Uploaded August 2026 | Updated November 2026, 3 days ago
Bluetooth Low Energy (BLE) security relies on a Long-Term Key (LTK) that serves as a root of trust. Users implicitly trust their paired devices, such as laptops, mice, and keyboards, assuming that once paired, they are secure. We show that this trust is fragile.
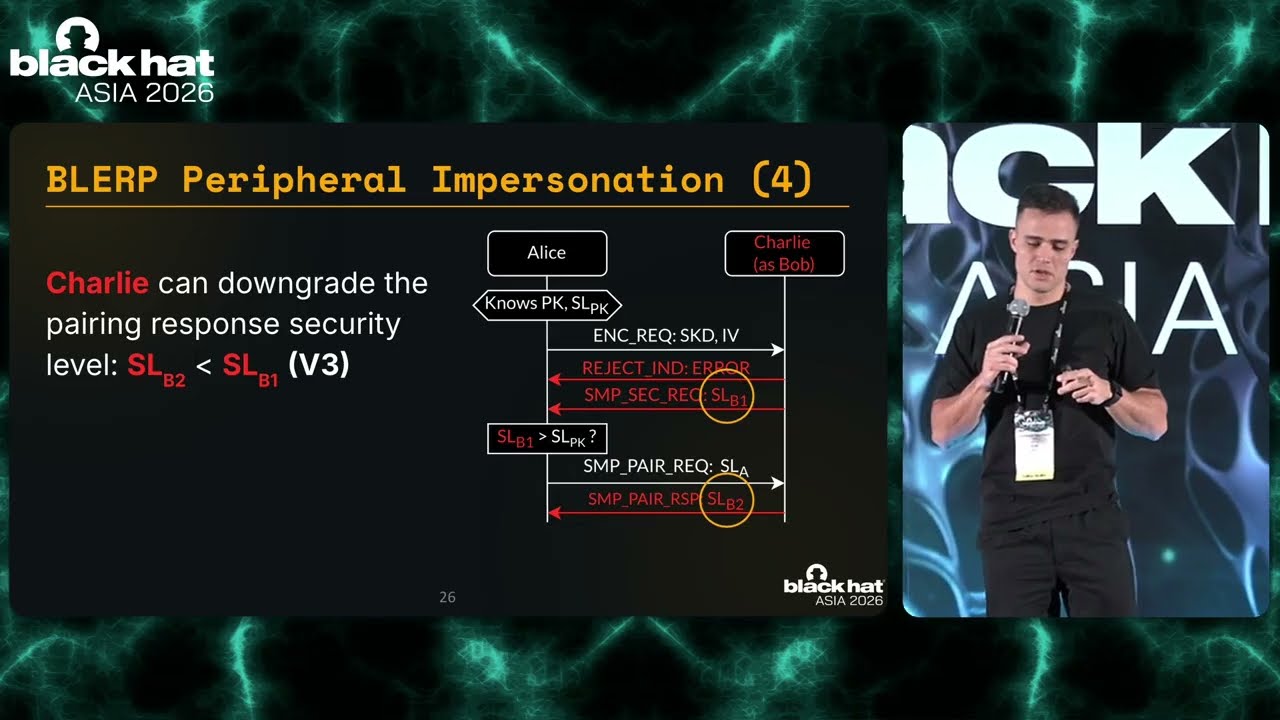
In this talk, we introduce the BLE Re-Pairing Attacks (BLERP), a new class of protocol-level attacks that weaponize the standard re-pairing mechanism to overwrite trusted LTKs with attacker-controlled keys, compromising the BLE security model. We reveal six critical design flaws affecting re-pairing in the latest Bluetooth standard (v6.1), and we show how these flaws enable device impersonation and Man-in-the-Middle (MitM) attacks, even against the most secure BLE configurations. The BLERP attacks are stealthy and practical: they are "0-click" on headless devices, such as keyboards, and require a single unauthenticated interaction on smartphones.
We describe the BLERP Toolkit, an open-source framework built on low-cost nRF52 hardware that enables over-the-air testing of BLE pairing and allows attendees to audit their own devices. The talk includes a live demonstration of a re-pairing Peripheral Impersonation attack against a smartphone and concludes with immediate, actionable mitigations to protect against the BLERP attacks. Attendees will learn about BLE security, how BLERP attacks undermine it, and how to defend against these newly identified threats.
Tommaso Sacchetti | PhD Candidate, EURECOM
Daniele Antonioli | Assistant Professor, EURECOM
blackhat.com/asia-26/briefings/schedule/?#exploiting-ble-re-pairing-with-the-blerp-attacks-50164
Bluetooth Low Energy (BLE) security relies on a Long-Term Key (LTK) that serves as a root of trust. Users implicitly trust their paired devices, such as laptops, mice, and keyboards, assuming that once paired, they are secure. We show that this trust is fragile.
In this talk, we introduce the BLE Re-Pairing Attacks (BLERP), a new class of protocol-level attacks that weaponize the standard re-pairing mechanism to overwrite trusted LTKs with attacker-controlled keys, compromising the BLE security model. We reveal six critical design flaws affecting re-pairing in the latest Bluetooth standard (v6.1), and we show how these flaws enable device impersonation and Man-in-the-Middle (MitM) attacks, even against the most secure BLE configurations. The BLERP attacks are stealthy and practical: they are "0-click" on headless devices, such as keyboards, and require a single unauthenticated interaction on smartphones.
We describe the BLERP Toolkit, an open-source framework built on low-cost nRF52 hardware that enables over-the-air testing of BLE pairing and allows attendees to audit their own devices. The talk includes a live demonstration of a re-pairing Peripheral Impersonation attack against a smartphone and concludes with immediate, actionable mitigations to protect against the BLERP attacks. Attendees will learn about BLE security, how BLERP attacks undermine it, and how to defend against these newly identified threats.
Tommaso Sacchetti | PhD Candidate, EURECOM
Daniele Antonioli | Assistant Professor, EURECOM
blackhat.com/asia-26/briefings/schedule/?#exploiting-ble-re-pairing-with-the-blerp-attacks-50164