Uploaded August 2023 | Updated September 2026, 2 weeks ago
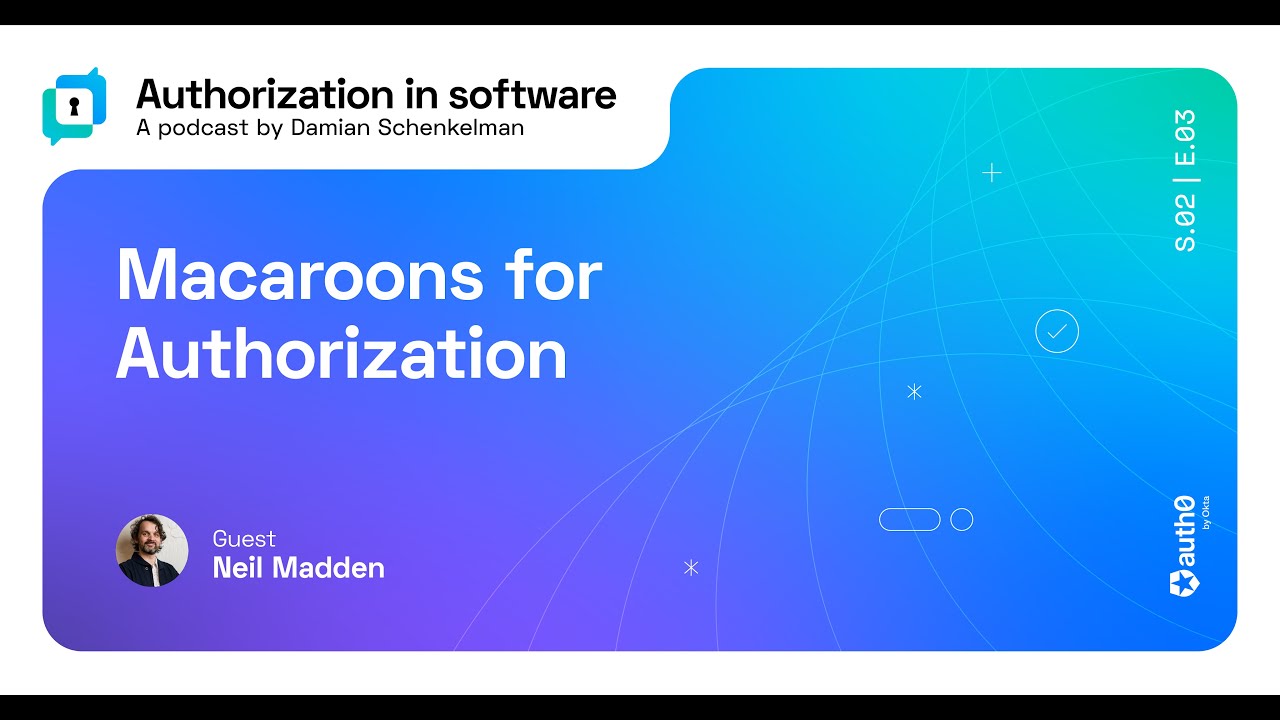
In this episode, host Damian Schenkelman and cybersecurity expert Neil Madden deep dive into the world of macaroons for authorization. Neil starts by distinguishing between JSON Web Tokens (JWT) and macaroons, and shares the origins and unique properties of the latter. They discuss how these Google-invented tokens can enhance security by enabling the addition of conditions, or "caveats", to the token even after it's been issued. The discussion also includes the difference between first-party and third-party caveats, key considerations for implementing macaroons, and how they can be integrated into existing systems like OAuth.
In this episode, host Damian Schenkelman and cybersecurity expert Neil Madden deep dive into the world of macaroons for authorization. Neil starts by distinguishing between JSON Web Tokens (JWT) and macaroons, and shares the origins and unique properties of the latter. They discuss how these Google-invented tokens can enhance security by enabling the addition of conditions, or "caveats", to the token even after it's been issued. The discussion also includes the difference between first-party and third-party caveats, key considerations for implementing macaroons, and how they can be integrated into existing systems like OAuth.