Uploaded August 2026 | Updated September 2026, 2 weeks ago
[EuroPython 2026 - S1 on 2026-07-16]
🎤 *Anatomy of a Phishing Campaign by Mike Fiedler*
🔗 https://ep2026.europython.eu/session/anatomy-of-a-phishing-campaign
📝 Abstract:
In July 2025, PyPI users received emails directing them to pypj.org—a near-perfect clone transparently proxying requests to pypi.org. Within hours, attackers compromised four accounts and uploaded malicious releases of the popular num2words package.
This talk dissects the complete attack chain: how attackers harvested email addresses from public package metadata, built a transparent proxy that relayed TOTP codes in real-time, and why traditional 2FA failed while WebAuthn-based authentication stopped the attack cold.
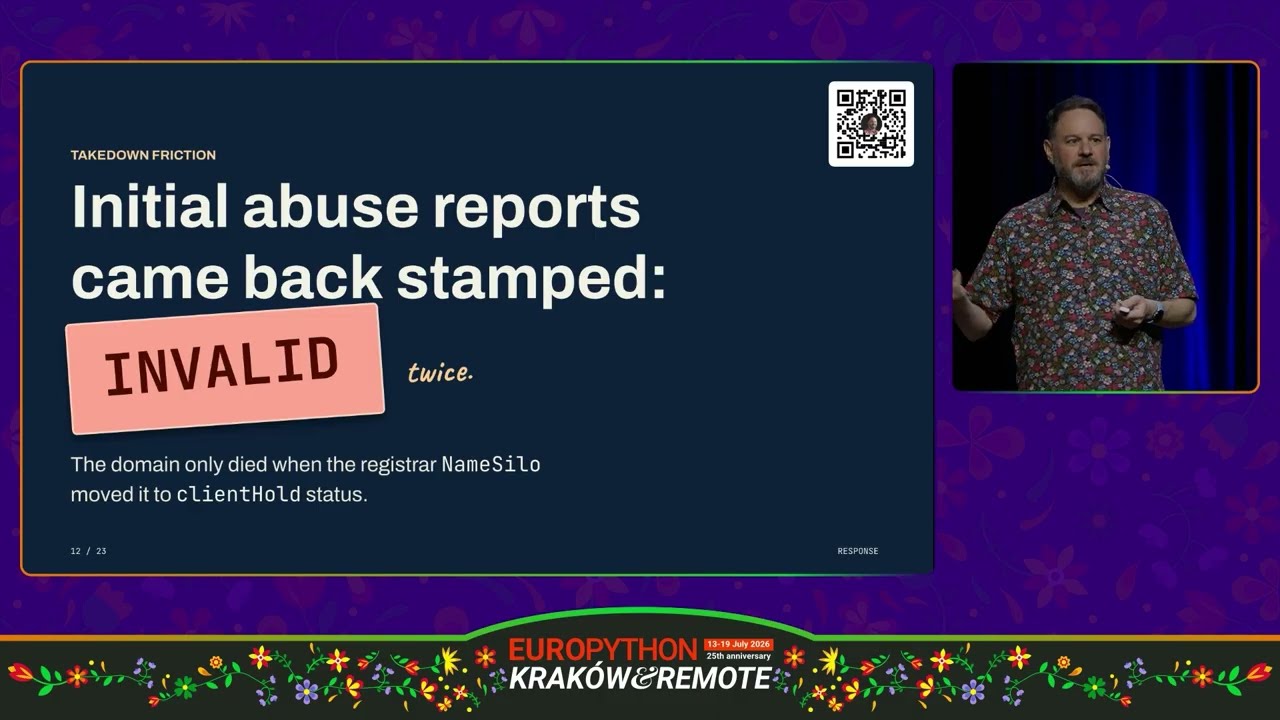
The session covers the incident response timeline, challenges getting malicious infrastructure taken down (including initial rejection of abuse reports), and defensive measures deployed afterward—including new email verification for TOTP logins from unrecognized devices.
Attendees will learn exactly how modern phishing attacks work against package repositories, the critical difference between "phishable" and "phishing-resistant" 2FA, and practical steps to protect accounts and packages from the next campaign. The talk also examines the September 2025 follow-up campaign targeting pypi-mirror.org and patterns across these ongoing attacks.
---
This work is licensed under a Creative Commons Attribution-NonCommercial-ShareAlike 4.0 International License: creativecommons.org/licenses/by-nc-sa/4.0
[EuroPython 2026 - S1 on 2026-07-16]
🎤 *Anatomy of a Phishing Campaign by Mike Fiedler*
🔗 https://ep2026.europython.eu/session/anatomy-of-a-phishing-campaign
📝 Abstract:
In July 2025, PyPI users received emails directing them to pypj.org—a near-perfect clone transparently proxying requests to pypi.org. Within hours, attackers compromised four accounts and uploaded malicious releases of the popular num2words package.
This talk dissects the complete attack chain: how attackers harvested email addresses from public package metadata, built a transparent proxy that relayed TOTP codes in real-time, and why traditional 2FA failed while WebAuthn-based authentication stopped the attack cold.
The session covers the incident response timeline, challenges getting malicious infrastructure taken down (including initial rejection of abuse reports), and defensive measures deployed afterward—including new email verification for TOTP logins from unrecognized devices.
Attendees will learn exactly how modern phishing attacks work against package repositories, the critical difference between "phishable" and "phishing-resistant" 2FA, and practical steps to protect accounts and packages from the next campaign. The talk also examines the September 2025 follow-up campaign targeting pypi-mirror.org and patterns across these ongoing attacks.
---
This work is licensed under a Creative Commons Attribution-NonCommercial-ShareAlike 4.0 International License: creativecommons.org/licenses/by-nc-sa/4.0


