Uploaded October 2026 | Updated November 2026, 3 days ago
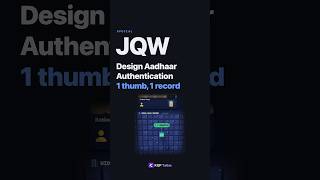
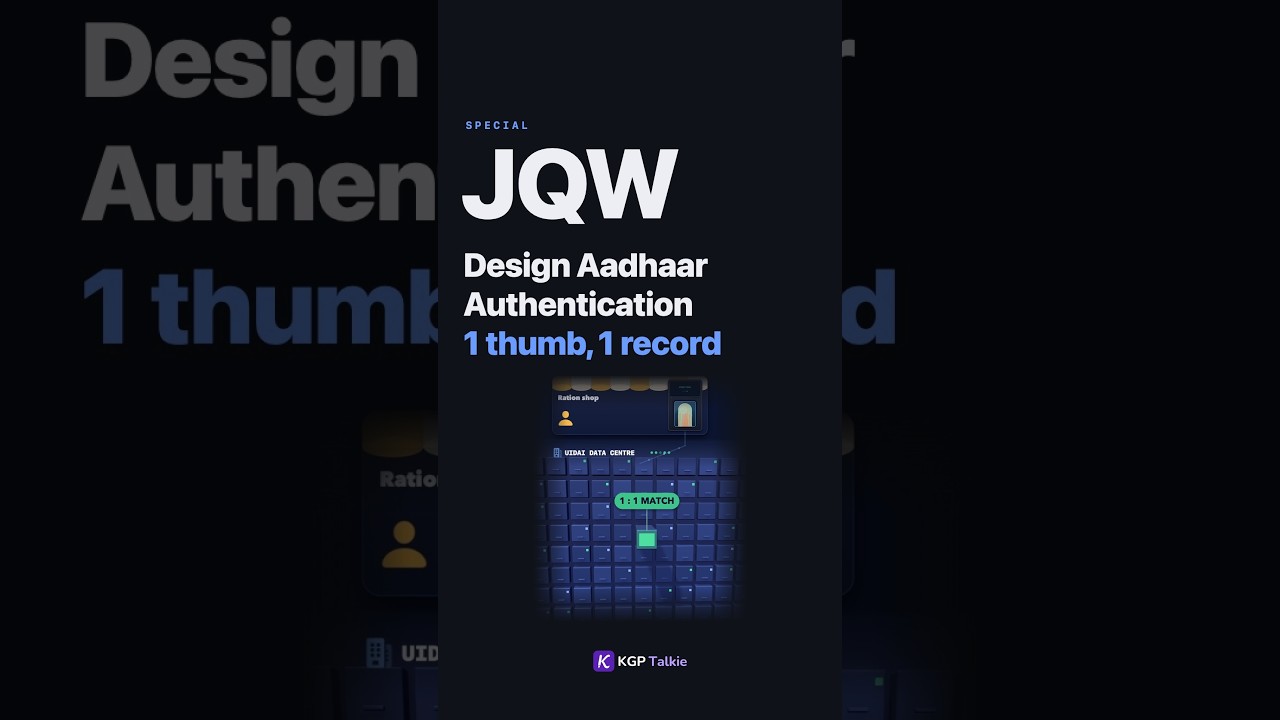
More than 1.3 billion people. One thumb on a scanner. Your identity is matched against just one record, and the answer comes back: yes. In a System Design Interview you get exactly this question: "Design Aadhaar Authentication System."
Most candidates say "store everyone's fingerprints in one database, search them all, and send the details back to the shop". Interviewers hear that all day. Searching everyone on every scan is slow, and sending details back leaks your identity to every counter.
- Fix 1: the request path. The shop's device works for a requesting entity (AUA), like a bank or the state's ration department. The request goes through an ASA, a secure network partner, to UIDAI's central store, CIDR. It carries the Aadhaar number plus one proof: OTP, fingerprint, iris or face, in a PID block encrypted on the certified device at capture. Everyone in between just passes on a sealed box
- Fix 2: one to one, not one to N. The Aadhaar number says whose record to open, so CIDR matches against that one record alone. That's why it's fast
- Fix 3: the answer is just yes or no. CIDR returns a digitally signed yes or no. No name, no address. Details only through e-KYC, with your consent, after an OTP or biometric match
- Fix 4: privacy by design. By law, UIDAI can't collect or keep the purpose of an authentication, and your bank account never reaches it. What stays is a thin log: which agency asked, when, which mode, yes or no. In your design, don't log the location either
- Fix 5: scale. Nearly 10 crore authentications a day, UIDAI's chairman said this September. Stateless match servers, two data centres, both active, and a target of about one second
- The follow-up: a mason's fingerprints are worn down and the scan keeps failing. A weak design says no and he goes home without his ration. A failed match is not fraud: retry with another finger, then iris, face, or an OTP on the registered mobile. The law says the requesting entity must offer another way. A fallback path, not a dead end
Put together, a strong answer: a sealed PID block, a one to one match, a signed yes or no, no purpose kept, and a fallback for every failed thumb.
Part 2, Aadhaar enrollment and its one to N dedup, is on the channel. Comment and tell me: has a fingerprint scan ever failed for you?
kgptalkie.com
#shorts #SystemDesign #SystemDesignInterview #Aadhaar #UIDAI #Biometrics #Authentication #eKYC #BackendInterview #InterviewPrep #SoftwareEngineering #KGPTalkie
More than 1.3 billion people. One thumb on a scanner. Your identity is matched against just one record, and the answer comes back: yes. In a System Design Interview you get exactly this question: "Design Aadhaar Authentication System."
Most candidates say "store everyone's fingerprints in one database, search them all, and send the details back to the shop". Interviewers hear that all day. Searching everyone on every scan is slow, and sending details back leaks your identity to every counter.
- Fix 1: the request path. The shop's device works for a requesting entity (AUA), like a bank or the state's ration department. The request goes through an ASA, a secure network partner, to UIDAI's central store, CIDR. It carries the Aadhaar number plus one proof: OTP, fingerprint, iris or face, in a PID block encrypted on the certified device at capture. Everyone in between just passes on a sealed box
- Fix 2: one to one, not one to N. The Aadhaar number says whose record to open, so CIDR matches against that one record alone. That's why it's fast
- Fix 3: the answer is just yes or no. CIDR returns a digitally signed yes or no. No name, no address. Details only through e-KYC, with your consent, after an OTP or biometric match
- Fix 4: privacy by design. By law, UIDAI can't collect or keep the purpose of an authentication, and your bank account never reaches it. What stays is a thin log: which agency asked, when, which mode, yes or no. In your design, don't log the location either
- Fix 5: scale. Nearly 10 crore authentications a day, UIDAI's chairman said this September. Stateless match servers, two data centres, both active, and a target of about one second
- The follow-up: a mason's fingerprints are worn down and the scan keeps failing. A weak design says no and he goes home without his ration. A failed match is not fraud: retry with another finger, then iris, face, or an OTP on the registered mobile. The law says the requesting entity must offer another way. A fallback path, not a dead end
Put together, a strong answer: a sealed PID block, a one to one match, a signed yes or no, no purpose kept, and a fallback for every failed thumb.
Part 2, Aadhaar enrollment and its one to N dedup, is on the channel. Comment and tell me: has a fingerprint scan ever failed for you?
kgptalkie.com
#shorts #SystemDesign #SystemDesignInterview #Aadhaar #UIDAI #Biometrics #Authentication #eKYC #BackendInterview #InterviewPrep #SoftwareEngineering #KGPTalkie