Uploaded August 2025 | Updated September 2026, 40 minutes ago
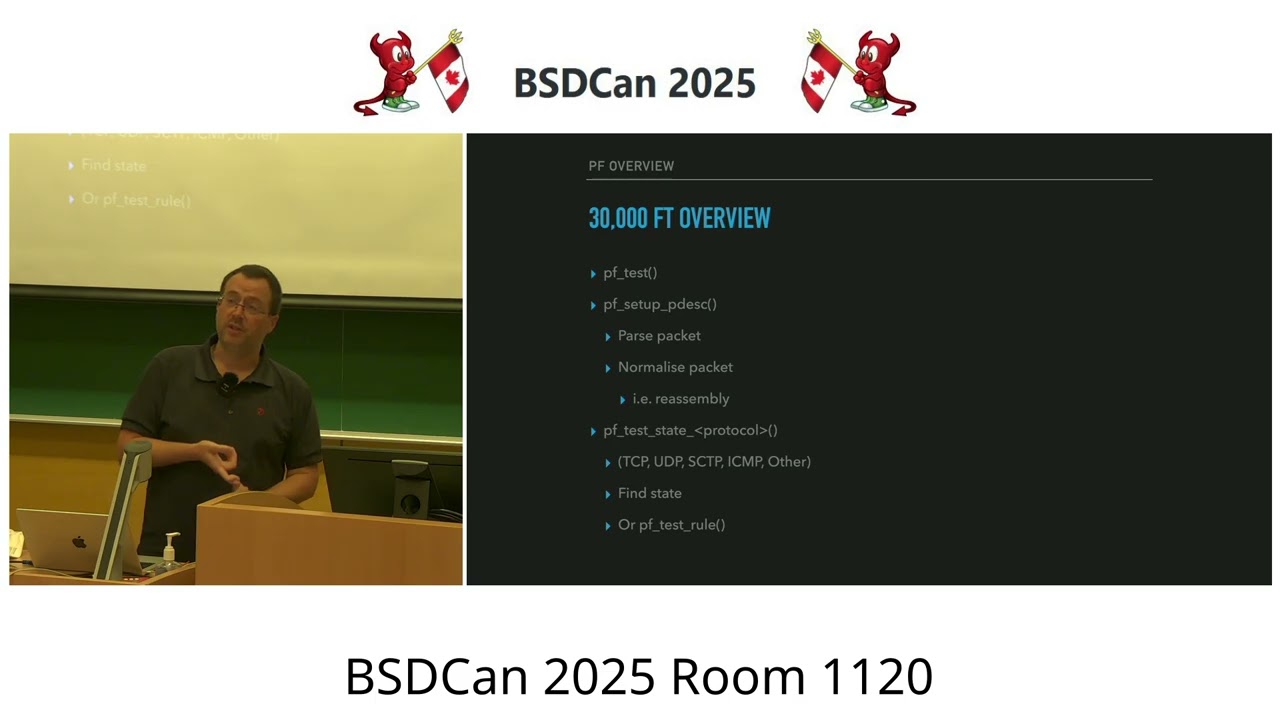
A walkthrough of a packet's journey through (FreeBSD's) pf, concentrating on the big picture and its implications.
We'll cover when packets are inspected, when rules are evaluated and how states are used. Along the way we'll cover what DTrace probes can show us, what some of pfctl's counters mean and just how many times pf can look at a single packet.
This talk is intended for firewall admins looking for a deeper understanding and aspiring pf developers. It is not a "How to use pf" talk.
A walkthrough of a packet's journey through (FreeBSD's) pf, concentrating on the big picture and its implications.
We'll cover when packets are inspected, when rules are evaluated and how states are used. Along the way we'll cover what DTrace probes can show us, what some of pfctl's counters mean and just how many times pf can look at a single packet.
This talk is intended for firewall admins looking for a deeper understanding and aspiring pf developers. It is not a "How to use pf" talk.


