Uploaded July 2026 | Updated September 2026, 2 weeks ago
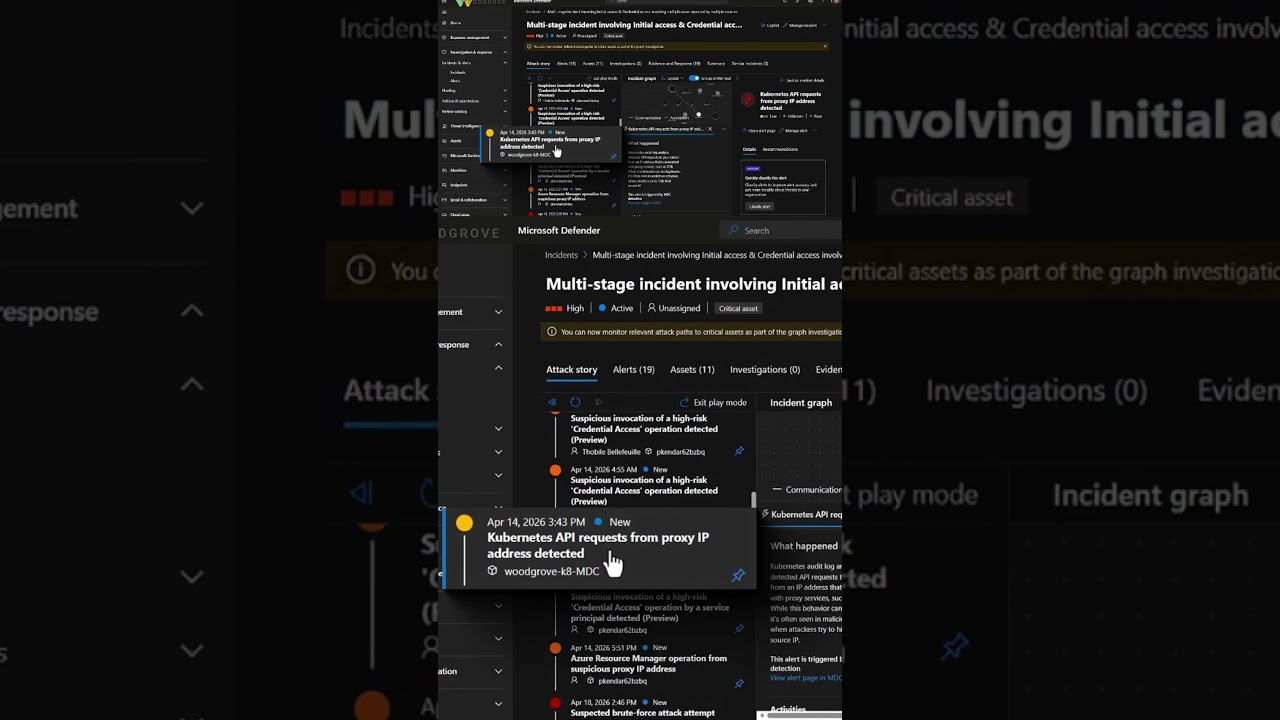
What does a multi-stage cloud attack look like when it's stitched into one story? Microsoft Defender for Cloud correlated 19 alerts into a single incident in near real time — tracing initial access from a Kubernetes API request, identity compromise via a stolen service principal, and cross-cloud lateral movement: a brute-force attack from an exposed Azure Kubernetes Service cluster targeting an AWS RDS resource.
▶ Full episode: youtu.be/CnqmC-CQs48
▶ Get started: https://aka.ms/DefenderCloudSecurity
#Shorts #DefenderForCloud #ContainerSecurity #Kubernetes #MicrosoftSecurity
What does a multi-stage cloud attack look like when it's stitched into one story? Microsoft Defender for Cloud correlated 19 alerts into a single incident in near real time — tracing initial access from a Kubernetes API request, identity compromise via a stolen service principal, and cross-cloud lateral movement: a brute-force attack from an exposed Azure Kubernetes Service cluster targeting an AWS RDS resource.
▶ Full episode: youtu.be/CnqmC-CQs48
▶ Get started: https://aka.ms/DefenderCloudSecurity
#Shorts #DefenderForCloud #ContainerSecurity #Kubernetes #MicrosoftSecurity